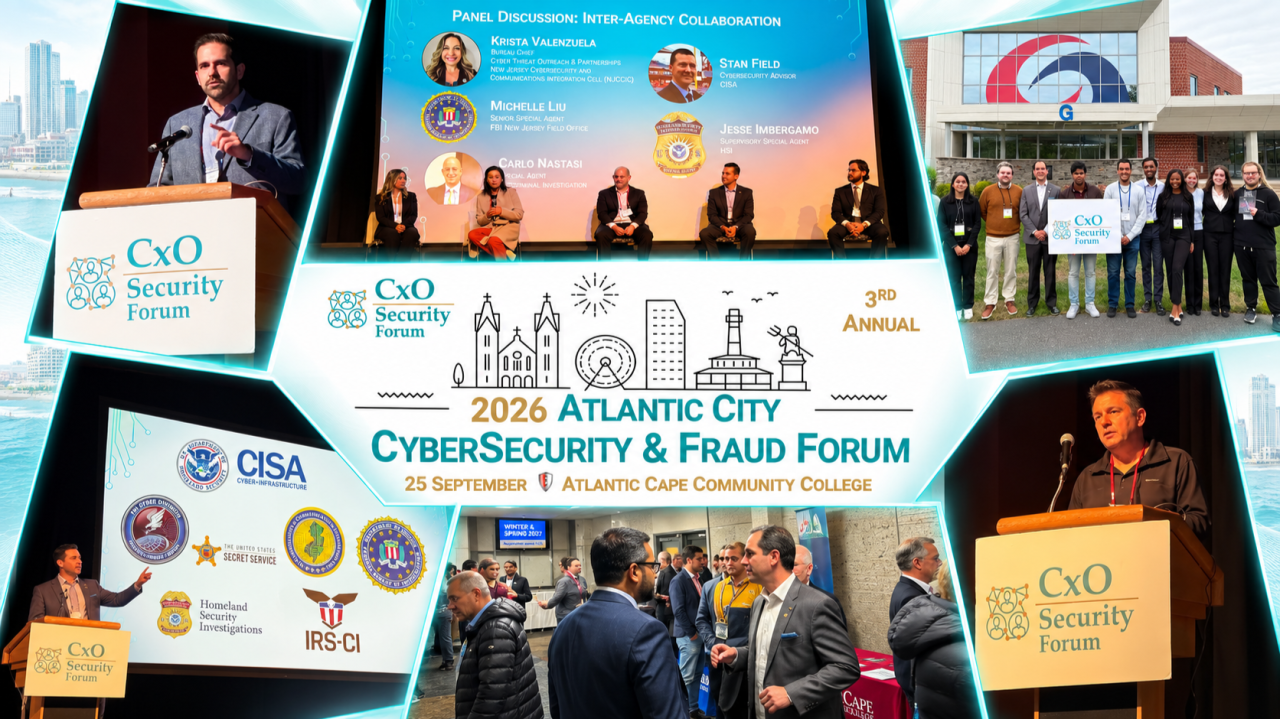
The 3rd Annual Atlantic City CyberSecurity & Fraud Forum brought together cybersecurity executives, federal investigators, AI experts, educators, and students to examine how cybersecurity, fraud, identity, and artificial intelligence are increasingly interconnected. Discussions explored outcome-driven security strategy, AI-powered attacks and autonomous agents, identity governance, Zero Trust, cryptocurrency investigations, AI model integrity, third-party risk, and the future cybersecurity workforce. A consistent theme emerged: today’s security challenges rarely fit within traditional organizational boundaries, making collaboration across security, fraud, finance, legal, government, and academia more important than ever. The central takeaway was that trust must be explicit, constrained, observable, and verifiable—and that the relationships needed to respond effectively to tomorrow’s incidents must be built before those incidents happen.