The CxO Security Forum brought together cybersecurity executives during Black Hat USA for an exclusive, invitation-only experience focused on meaningful connections, candid conversation, and peer-driven insight. Designed as a break from the traditional conference environment, the event gave senior security leaders an opportunity to connect with fellow practitioners, exchange perspectives, and enjoy an evening of networking in a relaxed setting.
Category: Industry Conferences
Senior cybersecurity, risk, technology, and business leaders gathered at the 3M Open for a candid discussion on third-party risk, trust, and resilience. The conversation explored how organizations can move beyond traditional questionnaires and compliance checklists to better measure risk, validate trust, and make more informed business decisions.
Gartner Security & Risk Management Summit 2026: Five Strategic Lessons Every CISO Should Take Back from National Harbor By Michael Hiskey Each year, Gartner Security & Risk Management Summit provides …
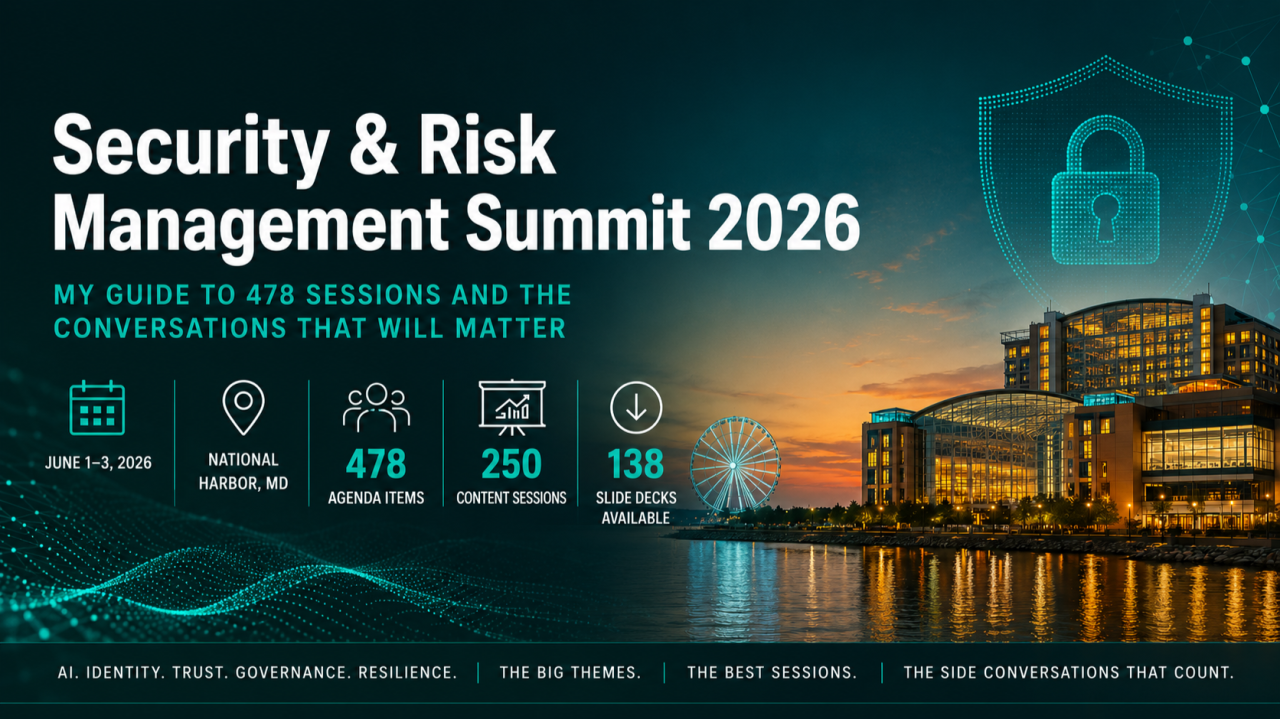
Security & Risk Management Summit 2026 — A Field Guide & Compendium National Harbor, MD · June 1–3, 2026 · 478 sessions 1. The Big Picture This year’s Gartner Security …
Security & Risk Management Summit 2026 — A Field Guide & CompendiumRead More »
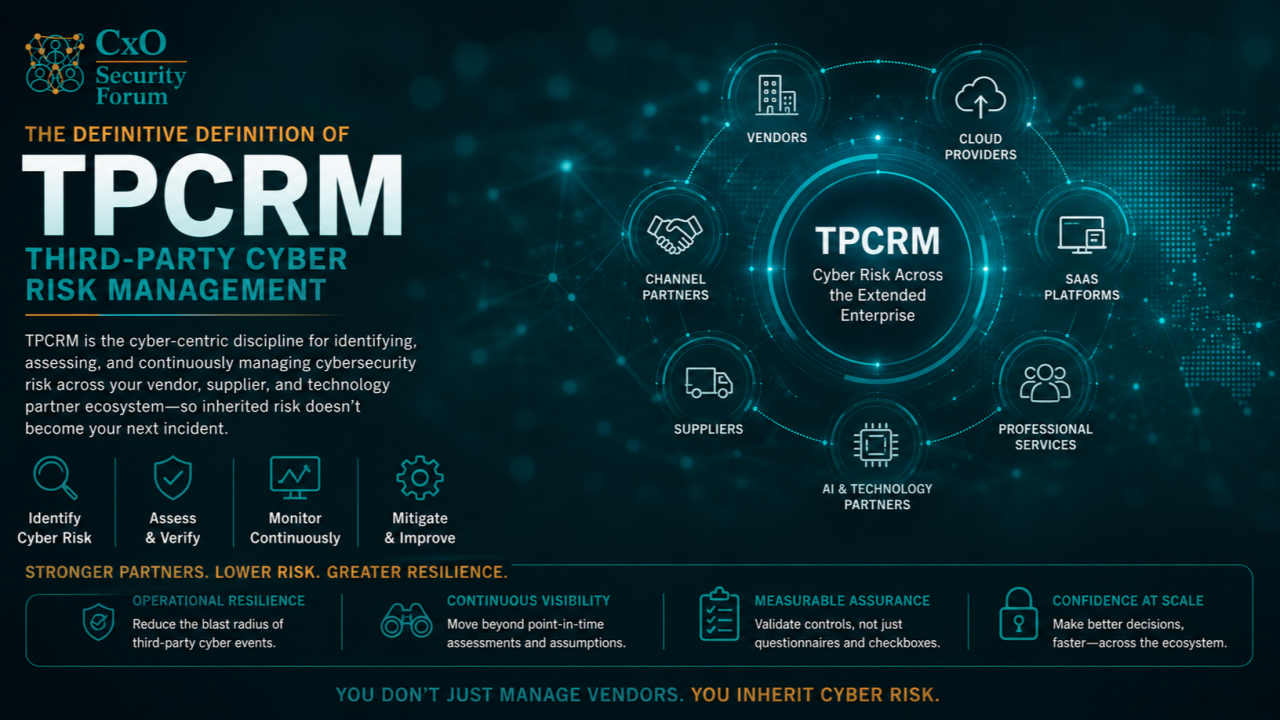
And Why CISOs Suddenly Care So Much… Organizations No Longer Just Manage Vendors–They Inherit Cyber Risk Third-Party Cyber Risk Management (TPCRM) is a term increasingly advanced by Gartner and now …
What is Third-Party Cyber Risk Management (TPCRM)?Read More »
Reflections from the National Cyber Innovation Forum Inside the U.S. Capitol Yesterday, I had the opportunity to attend the National Cyber Innovation Forum — an invite-only gathering held inside the …
Power, Patriotism, and the Future of Cyber: Inside the National Cyber Innovation ForumRead More »