NYC CxO Security Forum
Quarterly Executive Briefing
Tuesday 20 October 2026
Days
Hours
Minutes
Seconds
A Private, Peer-Led Forum for Cybersecurity Leaders
CxO Security Forum brings together senior executives in cybersecurity, risk, and compliance to engage in peer-driven dialogue — not one-way presentations or vendor pitches. Our curated discussions are designed to elevate strategic decision-making, sharpen leadership perspective, and support both professional growth and personal mastery in today’s complex threat landscape.
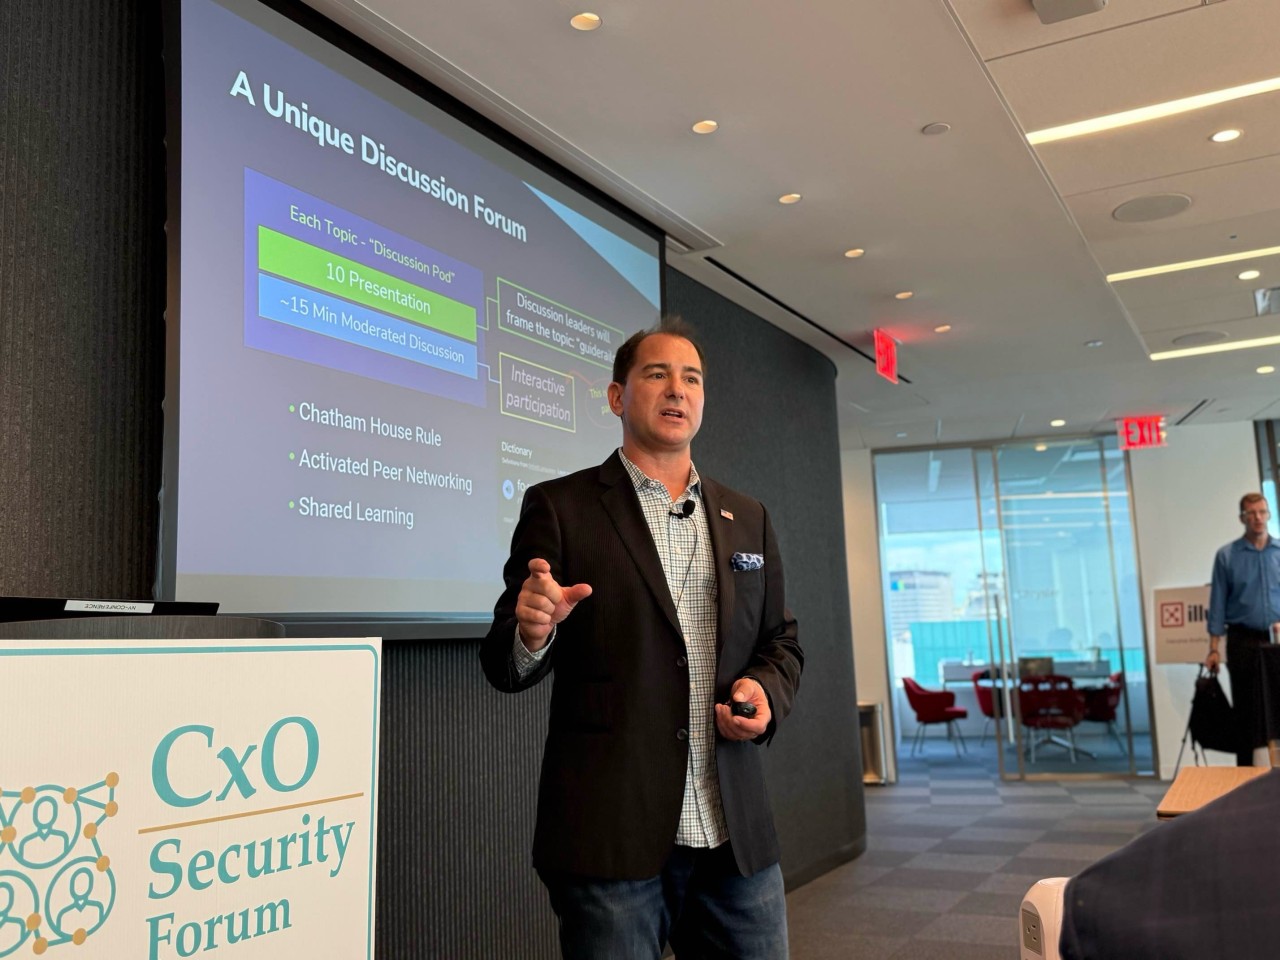
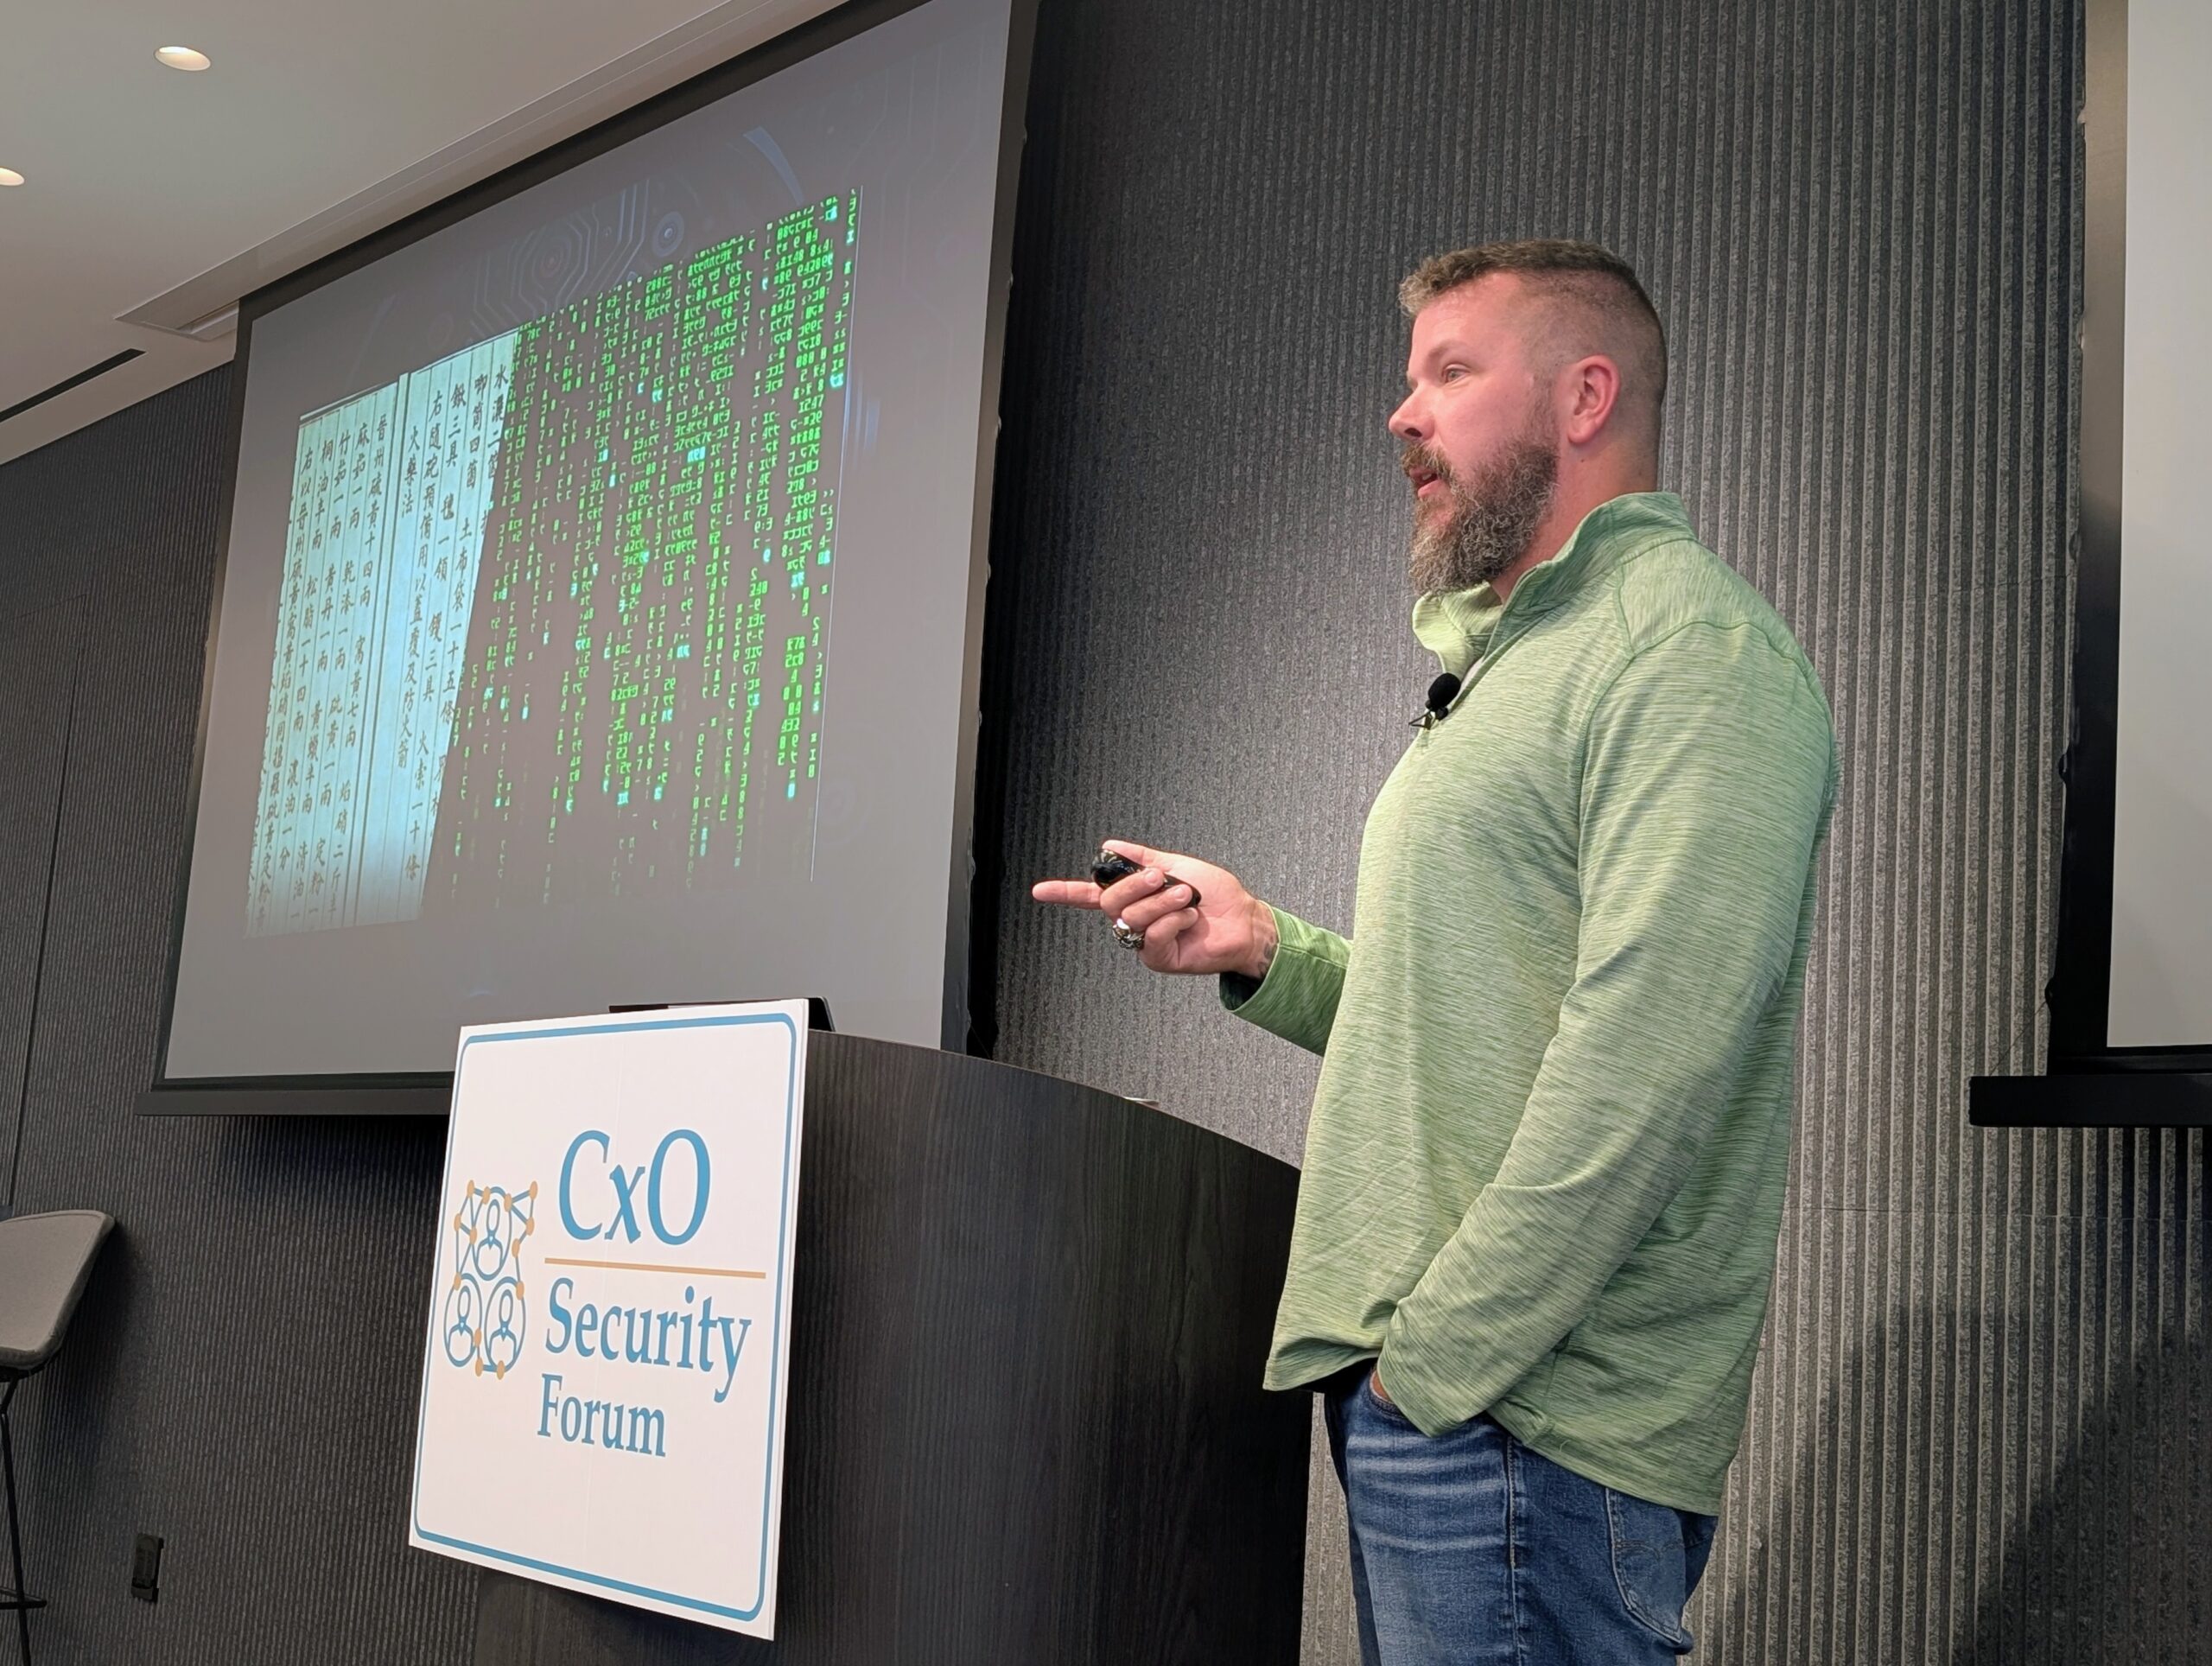
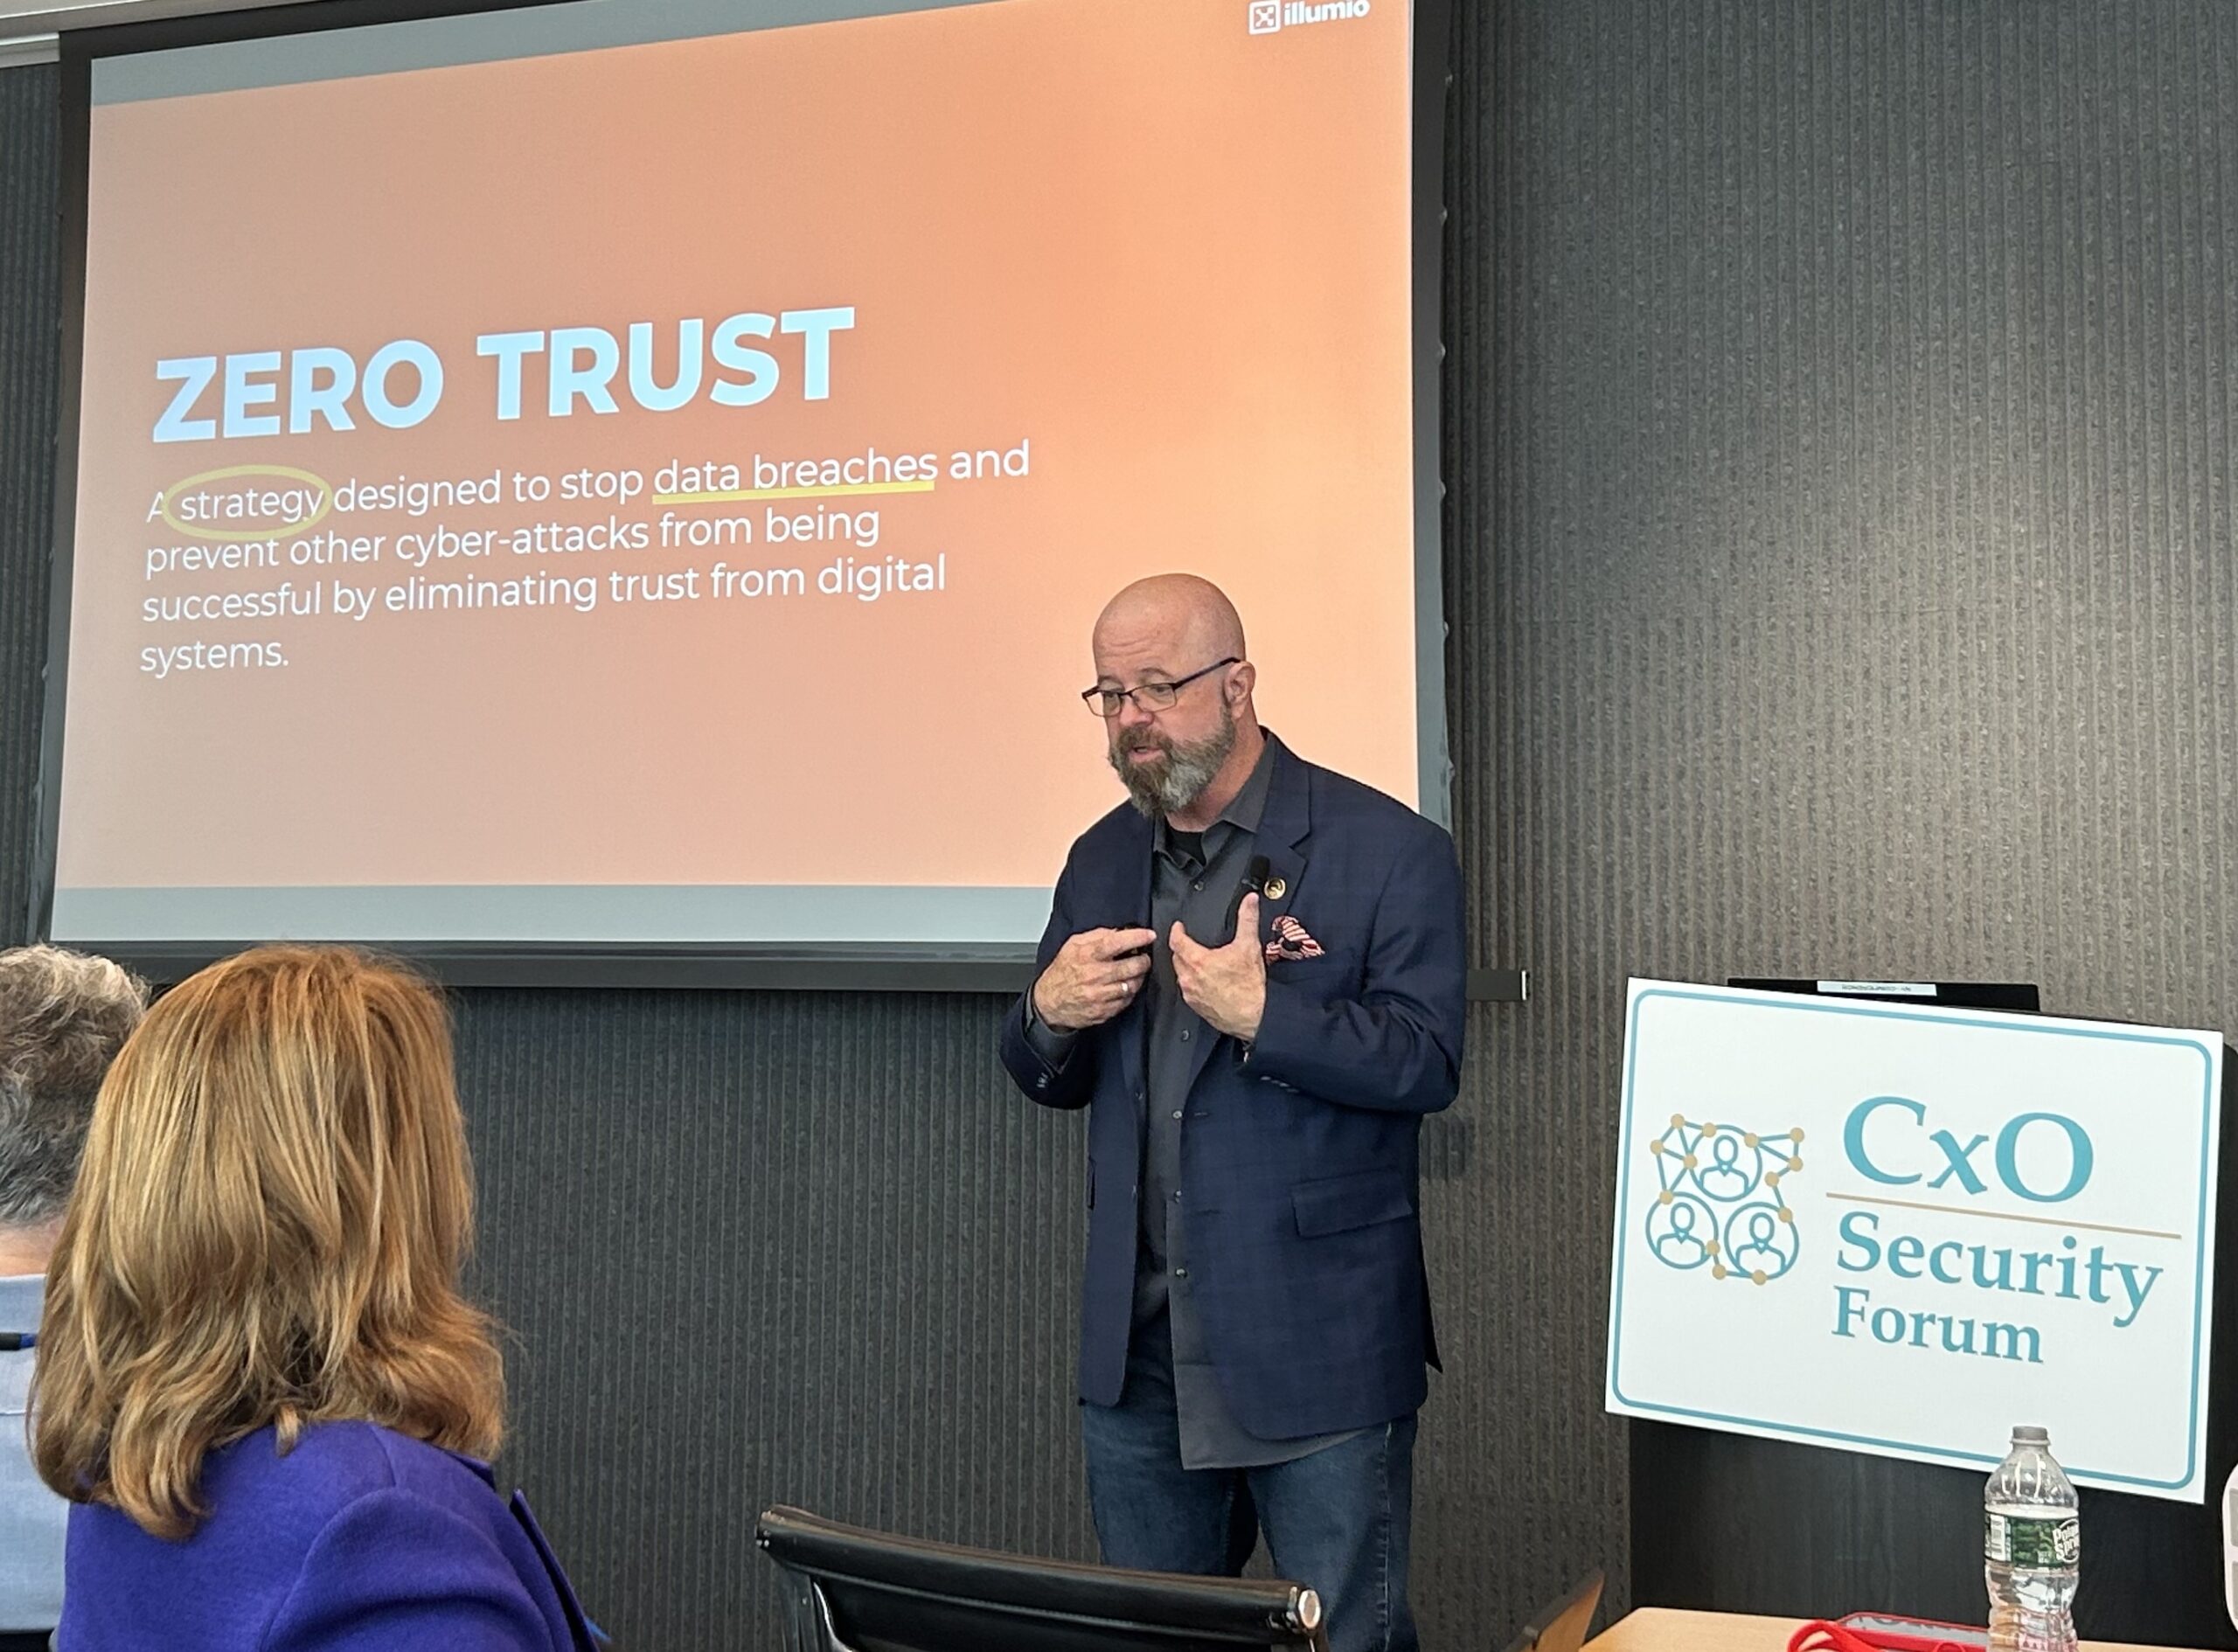
Each Executive Briefing has a unique agenda, which follows our engaging format with Discussion Leaders and thoughtful “TED Talk” presentations followed by moderated conversations where the assembled executives from the Community share their best practices, experiences, lessons learned, etc.
Participants gain:
- Trusted peer insight: candid discussion with leaders facing the same strategic challenges
- Personal & professional growth: sharpen leadership and strategic judgment through real executive exchange
- Actionable dialogue: moderated, high-impact conversations focused on what matters now
- No noise, no pitches: gatherings where peers drive the agenda and learning
- Stronger decision confidence: discussions that help you avoid costly missteps and evaluate solutions with clarity
June 2026 Agenda & Summary
LOOK BACK: You can review the agenda, as well as a summary with detailed notes from our last New York City CxO Security Forum.
(click the document icon above)
Thank You to Our Partners
Agenda
Our community-led gatherings ALWAYS have an amazing agenda filled with thoughtful Discussion Leaders and security, risk, & compliance influencers – including nationally-recognized authors and cyber-celebrities!
As with past NYC CxO Security Forum briefings, this gathering will feature a tightly curated agenda built around real-world insight, peer experience, and practical guidance — not theory or sales pitches.
🪪 Identity, NHI & Enterprise Risk — Back by popular demand: a fresh look at IAM and what non-human identities mean for our teams, policies and controls. Tim Rohrbaugh will double down on the risks facing CISOs/CIOs and share strategies he has devised to mitigate them.
⚖️ Agents, Access & Accountability — Ron Plesco, Partner at DLA Piper, will explore the legal implications of AI agents, delegated access and accountability—including what leaders should consider in contracts and prepare for before an incident. You may remember Tim Brown describing how DLA Piper quarterbacked SolarWinds’ incident response; Ron will build on that conversation.
🚀 Start-Up Showcase — Welcome AWS, a new sponsor of the CxO Security Forum Community! Look for three short talks from innovative cyber solution providers in their incubator portfolio—fresh perspectives on emerging problems, with room for your questions.
Practitioner-led. Moderated. No pitches. Chatham House Rule.
As always, each session will be succinct, moderated, and discussion-driven, building toward a cohesive set of takeaways rather than disconnected presentations.
Registration & Networking
3:00 PMWelcome/Introductions
3:30 PMIdentity, Reimagined: Rethinking IAM for the Human and Non-Human Era
[Discussion Pod #1]
Identity and Access Management (IAM) is evolving rapidly as organizations confront the growing number of non-human identities, including AI agents, service accounts, bots, and automated processes. This presentation explores why traditional IAM approaches need a fresh look, how expanding identity ecosystems affect security teams and policies, and what emerging legal, regulatory, and contractual requirements mean for identity governance. Discover how security leaders can rethink identity strategies to address new risks, clarify accountability, and strengthen access controls across an increasingly automated enterprise.
3:45 PMTranscend
[Start-Up Showcase #1]
Transcend was founded in 2017 by Ben Brook and Mike Farrell, who met as Harvard computer science undergrads. Their simple question about their own personal data revealed just how fragmented and unenforceable data permissions were across enterprise systems. That question became the seed for building the platform that answers "can I use this data" in real-time, by encoding business rules, agent guardrails, consent, and preferences directly into the systems that process customer data. Today Transcend is the leading data decision infrastructure company for the AI era trusted by Fortune 500 brands.
4:10 PMAgents, Access & Accountability
[Discussion Pod #2]
As non-human identities multiply and agentic AI systems begin making decisions, accessing sensitive data, and taking actions with increasing autonomy, the boundaries of identity, privilege, and accountability are being fundamentally reshaped. Meanwhile, the AI/cyber arms race is accelerating, giving defenders new capabilities while creating new attack surfaces, legal exposure, and questions of responsibility when things go wrong.
This session led by Ron Plesco, Partner, DLA Piper, examines the emerging legal implications of machine identities and autonomous AI agents, from excessive or unmanaged privileges to data exposure, liability, regulatory obligations, and the challenge of assigning accountability for AI-driven actions. Through a CISO-focused lens, we’ll explore how security leaders can rethink identity governance, establish meaningful human oversight, and prepare for a threat landscape where AI is both a powerful defense mechanism and an increasingly sophisticated weapon. The goal: move beyond the hype to identify practical steps that help organizations innovate responsibly, manage risk, and remain accountable as the AI/cyber arms race evolves.
4:15 PMOuttake
[Start-Up Showcase #2]
At Outtake, we have spent 3 years building products that defend the integrity of the Internet with the core insight that trust is an economics problem. A high trust network makes falsehood expensive to maintain & truth universally accessible. This way bad actors pay high costs, and good actors interact fluidly within the network.
To accomplish this mission, we mapped the public Internet in depth - websites, authors, social content, software packages, and agents. On the behalf of companies like NVIDIA, Anthropic, OpenAI and governments like the United States, we went to war with nation-state attackers, bot farms & malicious agentic swarms to ensure falsehood becomes expensive for bad actors. In doing so, Outtake uncovered the underlying trust graph of the Internet – blooming clusters full of impersonations, scams, fraud, and malware sitting in stark contrast to high integrity nodes of verified good actors & their infrastructure. The rapidly growing volume of agentic traffic now seeks accessible truth as it routes towards those high integrity nodes which constitute the best counterparties, services, goods, and information.
Outtake’s mission is to build a high trust Internet because we believe trusted agent & human collaboration will unlock the next chapter of civilizational growth. We accomplish this by building products which continuously make truth more accessible & falsehood more expensive on digital networks.
4:40 PMThe AI–Cyber Arms Race: Mythos, Mayhem, or Much Ado About Nothing?
[Discussion Pod #3]
As AI accelerates both cyberattack capabilities and defensive innovation, security leaders must separate real threats from hype. Using the debate around “Mythos Armageddon” as a starting point, this presentation explores real-world lessons, emerging attack and defense techniques, practical best practices, and the importance of sharing threat intelligence. Join a candid, peer-driven discussion on what CISOs need to prepare for now, where the risks may be overstated, and how organizations can stay ahead in an increasingly AI-powered cyber arms race.
4:45 PMTeleskope
[Start-Up Showcase #3]
Teleskope is building a platform to automate data protection at scale, from detection to remediation and prevention.
Our platform seamlessly monitors cloud and SaaS data stores to provide a comprehensive inventory of assets, hidden or otherwise, alongside associated security and compliance risks. Our classification engine, powered by a multi-model machine learning engine, adapts to your unique environment, identifying sensitive data and any associated personas, such as employees or customers.
Teleskope can automatically enforce compliance requirements, redact sensitive data or remediate security vulnerabilities directly at the source, and allows your developers to implement any custom security or privacy protocols through our open apis, helping to shift security left and reduce the manual overhead on security and engineering teams.
Our mission is to ensure that as technology accelerates, the security of information is never left behind. We are equipping organizations to detect risks, automate protection, and scale with confidence.
Our vision is to create a world where protecting data is simple, scalable, and second nature, so organizations can innovate without jeopardizing their customers or business.
5:10 PMNetworking & Organized Interaction Break
5:15 PMNon-humans evolved but they are still non-humans 😉
[Discussion Pod #4]
A practical approach to managing our new friends by applying what we know about their siblings: algorithms, services and applications.
AI agents are entering the enterprise with access to tools, internal systems and sensitive data—often operating under the credentials of the people using them. When the activity looks like the employee, how does security distinguish what the human did from what the agent did?
Tim Rohrbaugh, founder of RadicalNotion.AI and former CISO of JetBlue Airways, brings a practical perspective: we have managed non-human accounts for decades, and those foundations still apply. What has changed is predictability. Unlike traditional applications executing predefined rules, agents infer, adapt and take actions that can vary even when the instructions remain the same.
In this interactive discussion, Tim will explore how to extend familiar security practices to AI agents: separate their identities from human accounts, provision only the access they need, establish a controlled path from experimentation to production, and adapt monitoring to less predictable behavior. Drawing on his own work with AI tools and models, he will challenge participants to consider what they can implement now—and how to make those controls workable for the people adopting AI across the business.
5:30 PMReception & Networking
Refreshments, food, cocktails & discussions till 8pm
6:00 PMRequest an Invitation
**Request an Invitation**
Registration is open only to qualified senior executives. (Sorry, this excludes Sales/Marketing/Business Development!)
Forum Discussion Leaders
(Past, Present & Future)
Tim Rohrbaugh
Founder - RadicalNotion.AI, 3x Public Co. CISO
Tim Rohrbaugh brings 20+ years of C-level cybersecurity leadership to the frontier of AI for security and applied engineering. As founder of RadicalNotion.AI and former CISO of JetBlue Airways, he has built and operated enterprise programs that protect high-value, regulated data— including responsibility for safeguarding more than 40 million consumer records at a public financial services company.
A career security architect and systems engineer, Tim advances a practical view of GenAI as “augmented intelligence”: trustworthy, domain-tuned reasoning agents that reduce noise, challenge bias, and accelerate evidence-backed decisions without exposing IP. He has served as Vice Chair of the Airlines for America Cyber Security Council and as a board member of the Online Trust Alliance, where he contributed to national privacy and security policy. His work has been recognized with multiple awards, including Top Global CISO by Cyber Defense Magazine. Tim holds two joint patents in identity verification and authentication and is a frequent speaker and advisor to boards and engineering teams alike.
Ron Plesco
Partner, DLA Piper
Ron Plesco, a former prosecutor, is an internationally known information security and privacy lawyer with more than 20 years of experience in cyber investigations, privacy, threat intelligence, information assurance, identity management, cyber threats and cyber-enabled frauds, data analytics and artificial intelligence.
Ronald's clients represent the top global retail, financial, manufacturing, automotive, technology, communications, defense, life sciences and private equity corporations.
Jeff Klein
Partner, DLA Piper
Jeff Klein advises high-growth technology and other companies through all stages of the corporate lifecycle and investors that support these companies. He has deep experience in formation issues (including founder equity issues), venture, growth and other equity financing transactions, mergers and acquisitions (M&A), commercial transactions, external general counsel matters, securities laws, corporate governance, and joint ventures.
Thomas Klein
AWS Startups PGM Security & Government, Amazon Web Services
Thomas Klein, is a Senior Portfolio Growth Manager for Government & Security at Amazon Web Services (AWS), where he focuses on supporting growth and advancing cloud solutions for government and security-focused organizations. In his role, he works at the intersection of cloud technology, security, and public-sector priorities, helping organizations navigate evolving technology needs and opportunities. His work supports the broader adoption of cloud capabilities to advance mission objectives, strengthen security, and drive innovation.
Alex Dhillon
Alex Dhillon, Founder and CEO, Outtake
Alex Dhillon is the founder and CEO of Outtake, a cybersecurity company he launched in 2023 after nearly five years as an AI engineer at Palantir. Outtake uses autonomous AI agents to detect and remove cyberthreats — including phishing, impersonation, and fake content — in near real time, and counts OpenAI, AppLovin, Bill Ackman's Pershing Square, and federal agencies among its customers.
In January 2026, Outtake raised a $40 million Series B led by Iconiq, with participation from CRV, S32, and angel investors including Microsoft CEO Satya Nadella, Palo Alto Networks CEO Nikesh Arora, Anduril co-founder Trae Stephens, Palantir tech chief Shyam Sankar, and Bill Ackman. Alex describes the company's mission as building a "trust layer for the Internet" — meeting the moment as AI raises both the speed and sophistication of modern cyberthreats.
Jess Dandorph
Head of Sale Engineering - Sr. Director, Transcend
Jess Dandorph leads Solutions Engineering at Transcend, the autonomous agent and data control platform trusted by Fortune 500 companies. She works with enterprise security, privacy and data leaders to build governance into the systems and AI agents that use customer data. Jess has more than 10 years of experience in customer data infrastructure, spanning advertising, customer data platforms and privacy. Her focus today is helping enterprises answer a new question: can this agent do this, for this purpose, right now?
Elizabeth "Lizzy" Nammour
CEO & Founder, Teleskope
Originally from Lebanon, Elizabeth ("Lizzy") Nammour earned a Computer Science degree with a minor in Engineering Entrepreneurship from the University of Pennsylvania. She began her career as a software engineer at companies like Amazon and Booz Allen, focusing on data security challenges. At Airbnb, Lizzy led the security engineering team in developing internal tools for tracking, understanding, and securing vast amounts of user data. In 2022, she identified a market gap in data security software and left Airbnb to create Teleskope, a product that applies similar technology to address data privacy and security concerns.
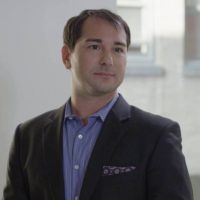
Michael Hiskey
[Moderator] Founder, CxO Security Forum | Author | Speaker | Executive Strategist
Michael Hiskey, is an author, blogger, and speaker with more than 20 years of experience in enterprise B2B strategy across cybersecurity, fintech, data, and AI. His work has appeared in Forbes, InformationWeek, WSJ.com, ITProPortal, and he has been featured on CNBC and C|Net.
A seasoned executive, Michael has held Chief Marketing Officer and Chief Strategy Officer roles at companies including Avanan, Socure, Semarchy, Trifacta, and Data Connectors, as well as leadership positions at IBM and MicroStrategy. He has lived and worked on three continents, managing global teams and driving measurable ROI for complex organizations.
Michael is the founder of the CxO Security Forum, a community-led network reinventing how executives connect for education, mentoring, and peer exchange. Having moderated and organized hundreds of cybersecurity conferences, roundtables, and executive forums, he is dedicated to creating practitioner-first environments that foster collaboration between industry, government, and academia.
He holds an MBA from Columbia Business School, and lives on Long Island with his wife and two daughters. More at linkedin.com/in/mphnyc.
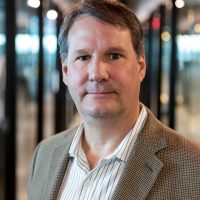
Tim Brown
CISO & VP, SolarWinds
Tim Brown joined SolarWinds in 2017 as vice president of security and is now the CISO for SolarWinds, overseeing internal IT security, product security, and security strategy. After the SUNBURST attack in December 2020, Tim Brown led the response and remediation efforts. Tim has spoken to thousands of customers and has been instrumental in all customer remediation support and services.
He has worked closely with the SolarWinds® CEO in designing the future state of security and their “Secure by Design” philosophy. This new philosophy on software design will not only benefit SolarWinds but the industry as a whole, and it sets a precedent for responses to future cyberattacks.
As a former Dell Fellow and CTO, Tim deeply understands the challenges and aspirations of the person responsible for driving digital innovation and change. Tim has over 25 years of experience, and his trusted advisor status has taken him from meeting with members of Congress and the Senate to the Situation Room in the White House. He’s also an avid inventor and holds 18 issued patents on security-related topics.
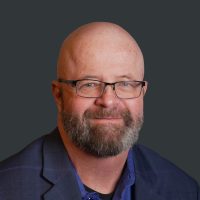
John Kindervag
Creator of Zero Trust
Chief Evangelist at Illumio
John Kindervag is considered one of the world’s foremost cybersecurity experts. With over 25 years of experience as a practitioner and industry analyst, he is best known for creating the revolutionary Zero Trust Model of Cybersecurity. As Chief Evangelist at Illumio, John Kindervag is responsible for accelerating awareness and adoption of Zero Trust Segmentation.
Most recently, John led cybersecurity strategy as a Senior Vice President at On2IT.
He previously served as Field CTO at Palo Alto Networks and, before that, spent over eight years as a Vice President and Principal Analyst on the security and risk team at Forrester Research.
In 2021, John was named to the President’s National Security Telecommunications Advisory Committee (NSTAC) Zero Trust Sub-Committee and was a primary author of the NSATC Zero Trust report that was delivered to the President. That same year, he was also named CISO Magazine’s Cybersecurity Person of the Year. John serves as an advisor to several organizations, including the Cloud Security Alliance and venture capital firm NightDragon.
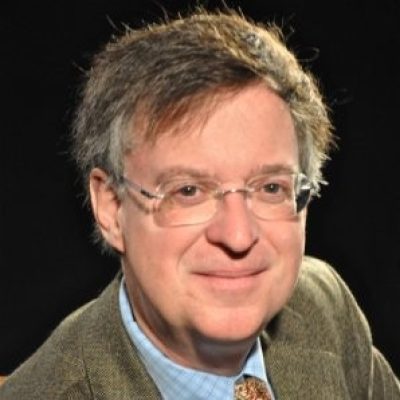
Richard Stiennon
Chief Research Analyst - IT Harvest
frmr. VP of Research - Gartner
Richard founded IT-Harvest in 2005 to cover the 4,550+ vendors that make up the IT security industry. He has presented on the topic of cybersecurity in 32 countries on six continents. He was a lecturer at Charles Sturt University in Australia. He is the author of Surviving Cyberwar (Government Institutes, 2010) and Washington Post Best Seller, There Will Be Cyberwar, as well as the annual Security Yearbook, published by Wiley for 2025. He was the VP of Research at Gartner. He has a B.S. in Aerospace Engineering from the University of Michigan, and his MA in War in the Modern World from King’s College, London.
Kurtis Minder
CEO & Co-Founder, GroupSense
Author, Cyber Recon: My Life in Cyber Espionage and Ransomware Negotiation
Kurtis Minder is one of the world’s foremost experts in ransomware response and cyber threat intelligence. As CEO and co-founder of GroupSense, he has led negotiations in some of the largest ransomware and data extortion cases globally, engaging directly with threat actors and nation-state affiliates.
With over 25 years in cybersecurity—including roles at Fortinet, AT&T, and Citrix-acquired Caymus Systems—Kurtis has combined operational security, cyber reconnaissance, and real-world intelligence tradecraft into a uniquely effective digital risk strategy. His pioneering work and insights have been featured in The New Yorker, BBC, The Wall Street Journal, and Fortune.
At ACCSFF 2025, Kurtis will deliver a TED-style keynote and participate in a moderated discussion on themes from his acclaimed new book, Cyber Recon, offering a rare behind-the-scenes look at the people, tools, and tactics behind today’s cyber espionage and ransomware ecosystem.
Dr. Chase Cunningham, PhD.
“Dr. Zero Trust” - Author, Speaker and Industry Thought-Leader
Dr. Chase Cunningham is a globally recognized cybersecurity strategist, bestselling author, and trusted advisor to both the public and private sectors. Widely known as “Dr. Zero Trust,” Chase pioneered the Zero Trust security framework during his time as a Senior Analyst at Forrester Research—an approach now adopted as a standard across government and Fortune 500 enterprises alike.
Over a 20+ year career that spans the U.S. Navy, Department of Defense, and senior industry roles, Chase has led initiatives in cryptographic systems, threat intelligence, cyber forensics, and national cyber defense strategy. He holds a PhD in Computer Science and Cybersecurity, with research centered on insider threats and advanced detection algorithms. He also maintains CISSP and CEH certifications.
An engaging keynote speaker and regular contributor to leading cybersecurity forums, Chase is the author of several acclaimed books including Cyber Warfare: Truth, Tactics, and Strategies and his latest, Buy the Breach: Hacking Failure for Market Success. In Buy the Breach, he unveils a contrarian but data-backed strategy for turning corporate cyber failures into personal financial gains—arming cyber professionals with the tools to outperform hedge funds by investing in the inevitable post-breach market rebound.
Chase is a rare voice who blends deep technical expertise with sharp financial insight. Whether briefing the Executive Branch or advising the boardroom, his mission is clear: empower defenders, demystify complexity, and challenge the status quo.
Josh Woodruff
Author, Agentic AI + Zero Trust: A Guide for Business Leaders
IANS Faculty | CSA Zero Trust Working Groups
Josh Woodruff is the author of Agentic AI + Zero Trust: A Guide for Business Leaders, a practical framework for safely operationalizing autonomous AI using Zero Trust principles. Drawing on nearly 30 years of experience as both a CIO and CISO, Josh translates real-world enterprise deployments into clear executive guidance on trust, governance, and risk in agentic systems.
The book—co-authored with Michelle Savage and featuring a foreword by Zero Trust pioneer John Kindervag—cuts through AI hype to explain why most AI initiatives stall in pilot mode, and what successful organizations do differently. Josh is also the Founder and CEO of Massive Scale Consulting, co-leads the Cloud Security Alliance Zero Trust Working Group, and serves as IANS Faculty, advising enterprises across regulated and high-risk industries.
Known for his ability to frame complex AI and security challenges in plain executive language, Josh focuses on helping leaders design guardrails that accelerate innovation without sacrificing control, accountability, or resilience.
Barak Perelman
CEO & Co-Founder, Opti
Barak Perelman is the CEO & Co-founder of Opti, where he is focused on addressing structural challenges in identity, governance, and accountability as AI becomes embedded into enterprise systems. A seasoned cybersecurity operator and founder, Barak brings more than two decades of hands-on experience building products, leading strategy, and protecting critical infrastructure in highly complex environments.
Previously, Barak was the Co-founder and CEO of Indegy, an industrial cybersecurity company that built a comprehensive security and governance platform for industrial networks. Indegy was acquired by Tenable in 2019, where Barak went on to serve as VP OT Security, helping integrate industrial and enterprise security perspectives. Earlier in his career, he led product design at Stratoscale, where he managed large-scale cybersecurity projects.
Barak holds degrees in computer science, mathematics, and physics, as well as an MBA. He is known for his ability to connect deep technical systems thinking with executive-level governance concerns, particularly around identity, accountability, and the unintended consequences of AI-driven automation inside large enterprises.
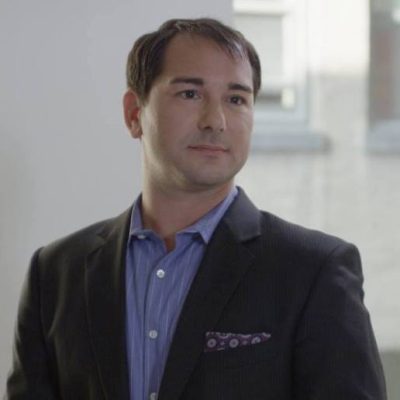
Michael Hiskey
[Moderator] Founder, CxO Security Forum | Author | Speaker | Executive Strategist
Michael Hiskey is an author, blogger, and speaker with more than 20 years of experience in enterprise B2B strategy across cybersecurity, fintech, data, and AI. His work has appeared in Forbes, InformationWeek, WSJ.com, ITProPortal, and he has been featured on CNBC and C|Net.
A seasoned executive, Michael has held Chief Marketing Officer and Chief Strategy Officer roles at companies including Avanan, Socure, Semarchy, Trifacta, and Data Connectors, as well as leadership positions at IBM and MicroStrategy. He has lived and worked on three continents, managing global teams and driving measurable ROI for complex organizations.
Michael is the founder of the CxO Security Forum, a community-led network reinventing how executives connect for education, mentoring, and peer exchange. Having moderated and organized hundreds of cybersecurity conferences, roundtables, and executive forums, he is dedicated to creating practitioner-first environments that foster collaboration between industry, government, and academia.
He holds an MBA from Columbia Business School, and lives on Long Island with his wife and two daughters. More at linkedin.com/in/mphnyc.
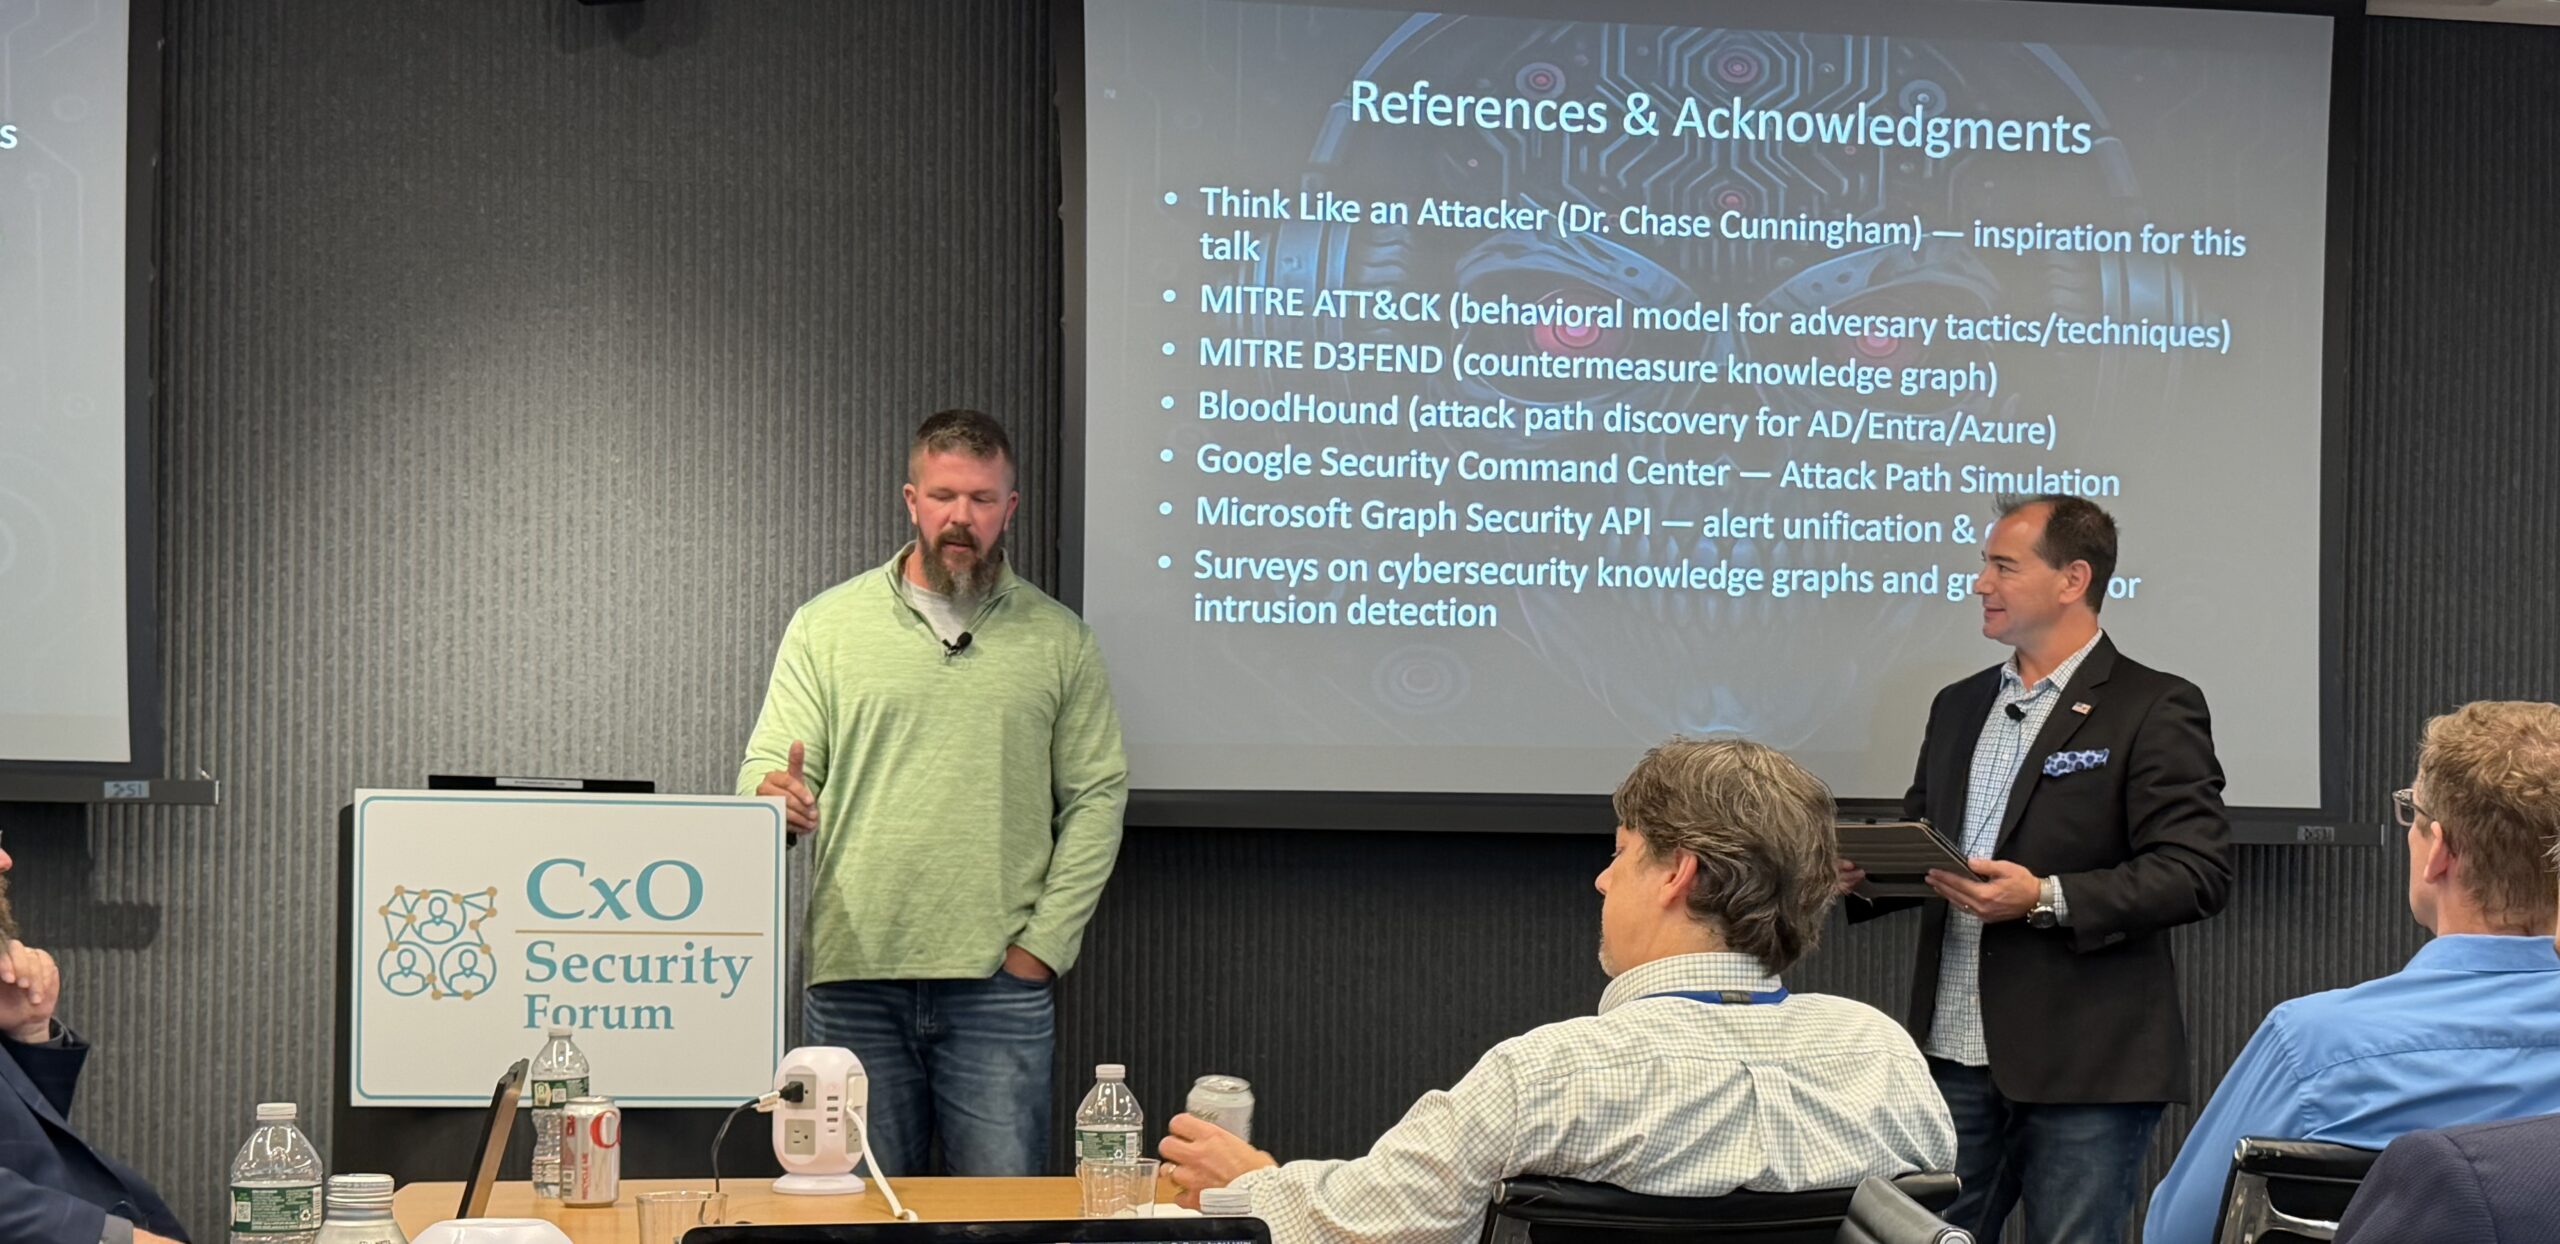
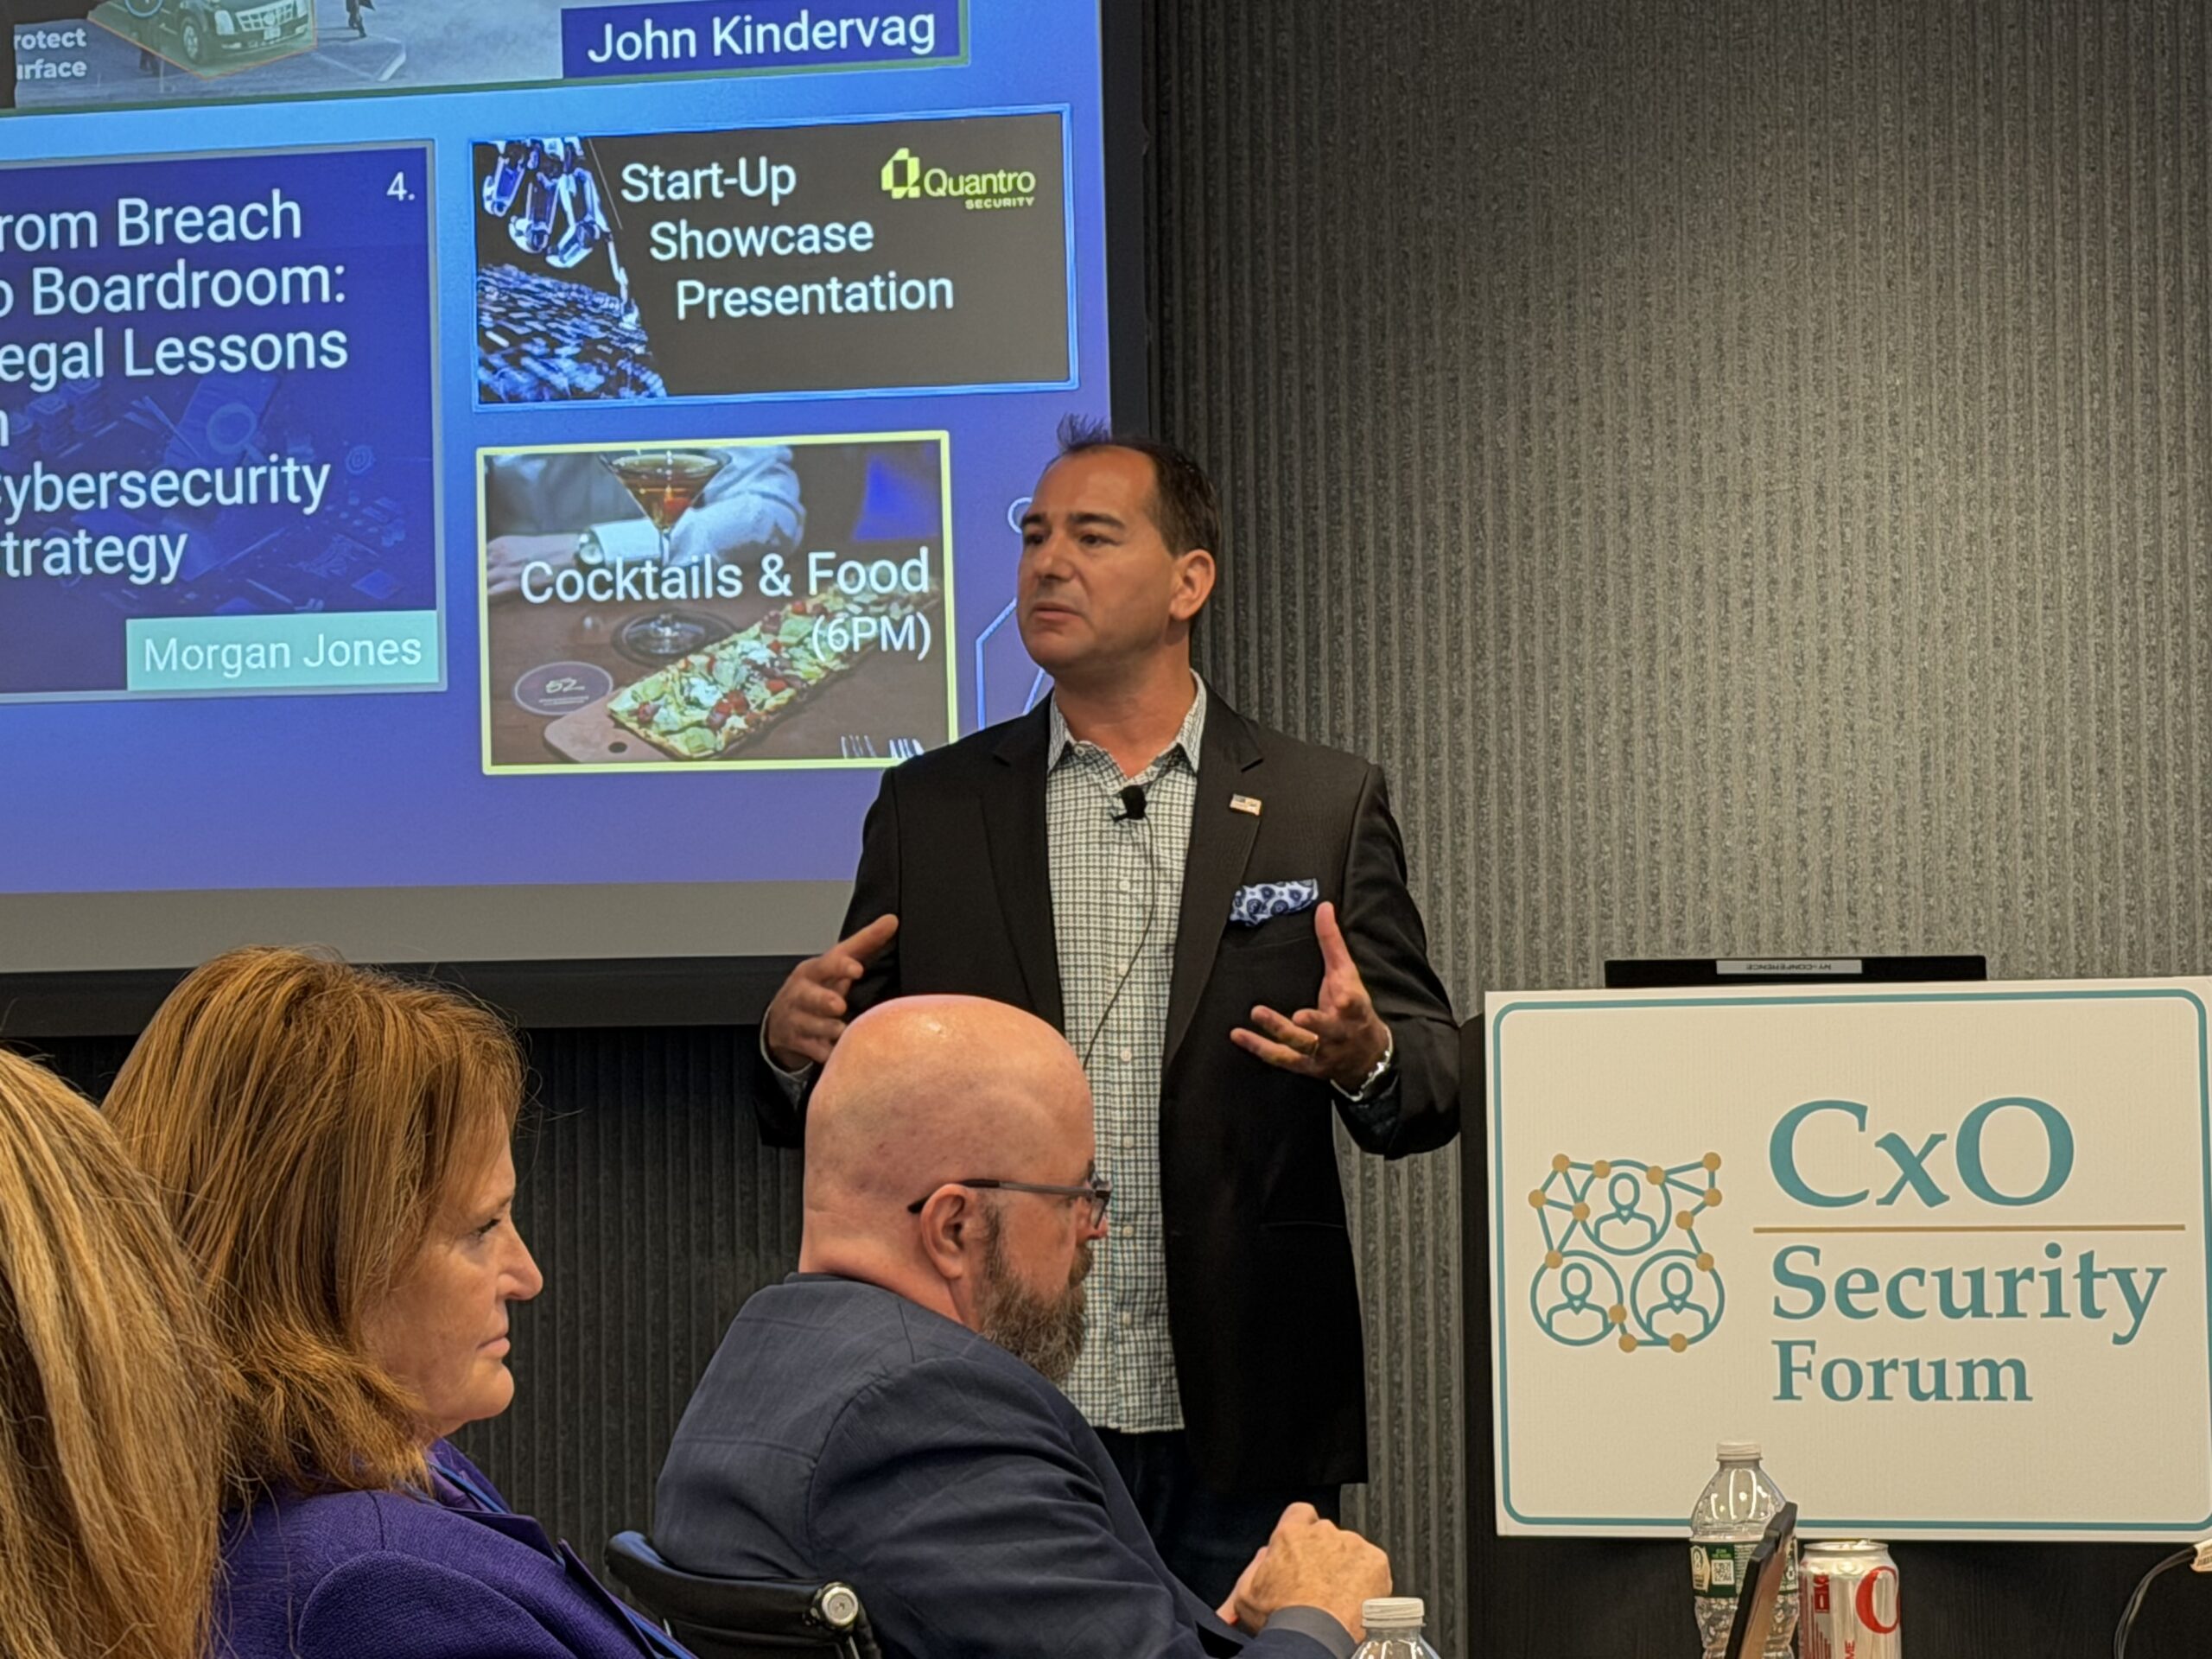
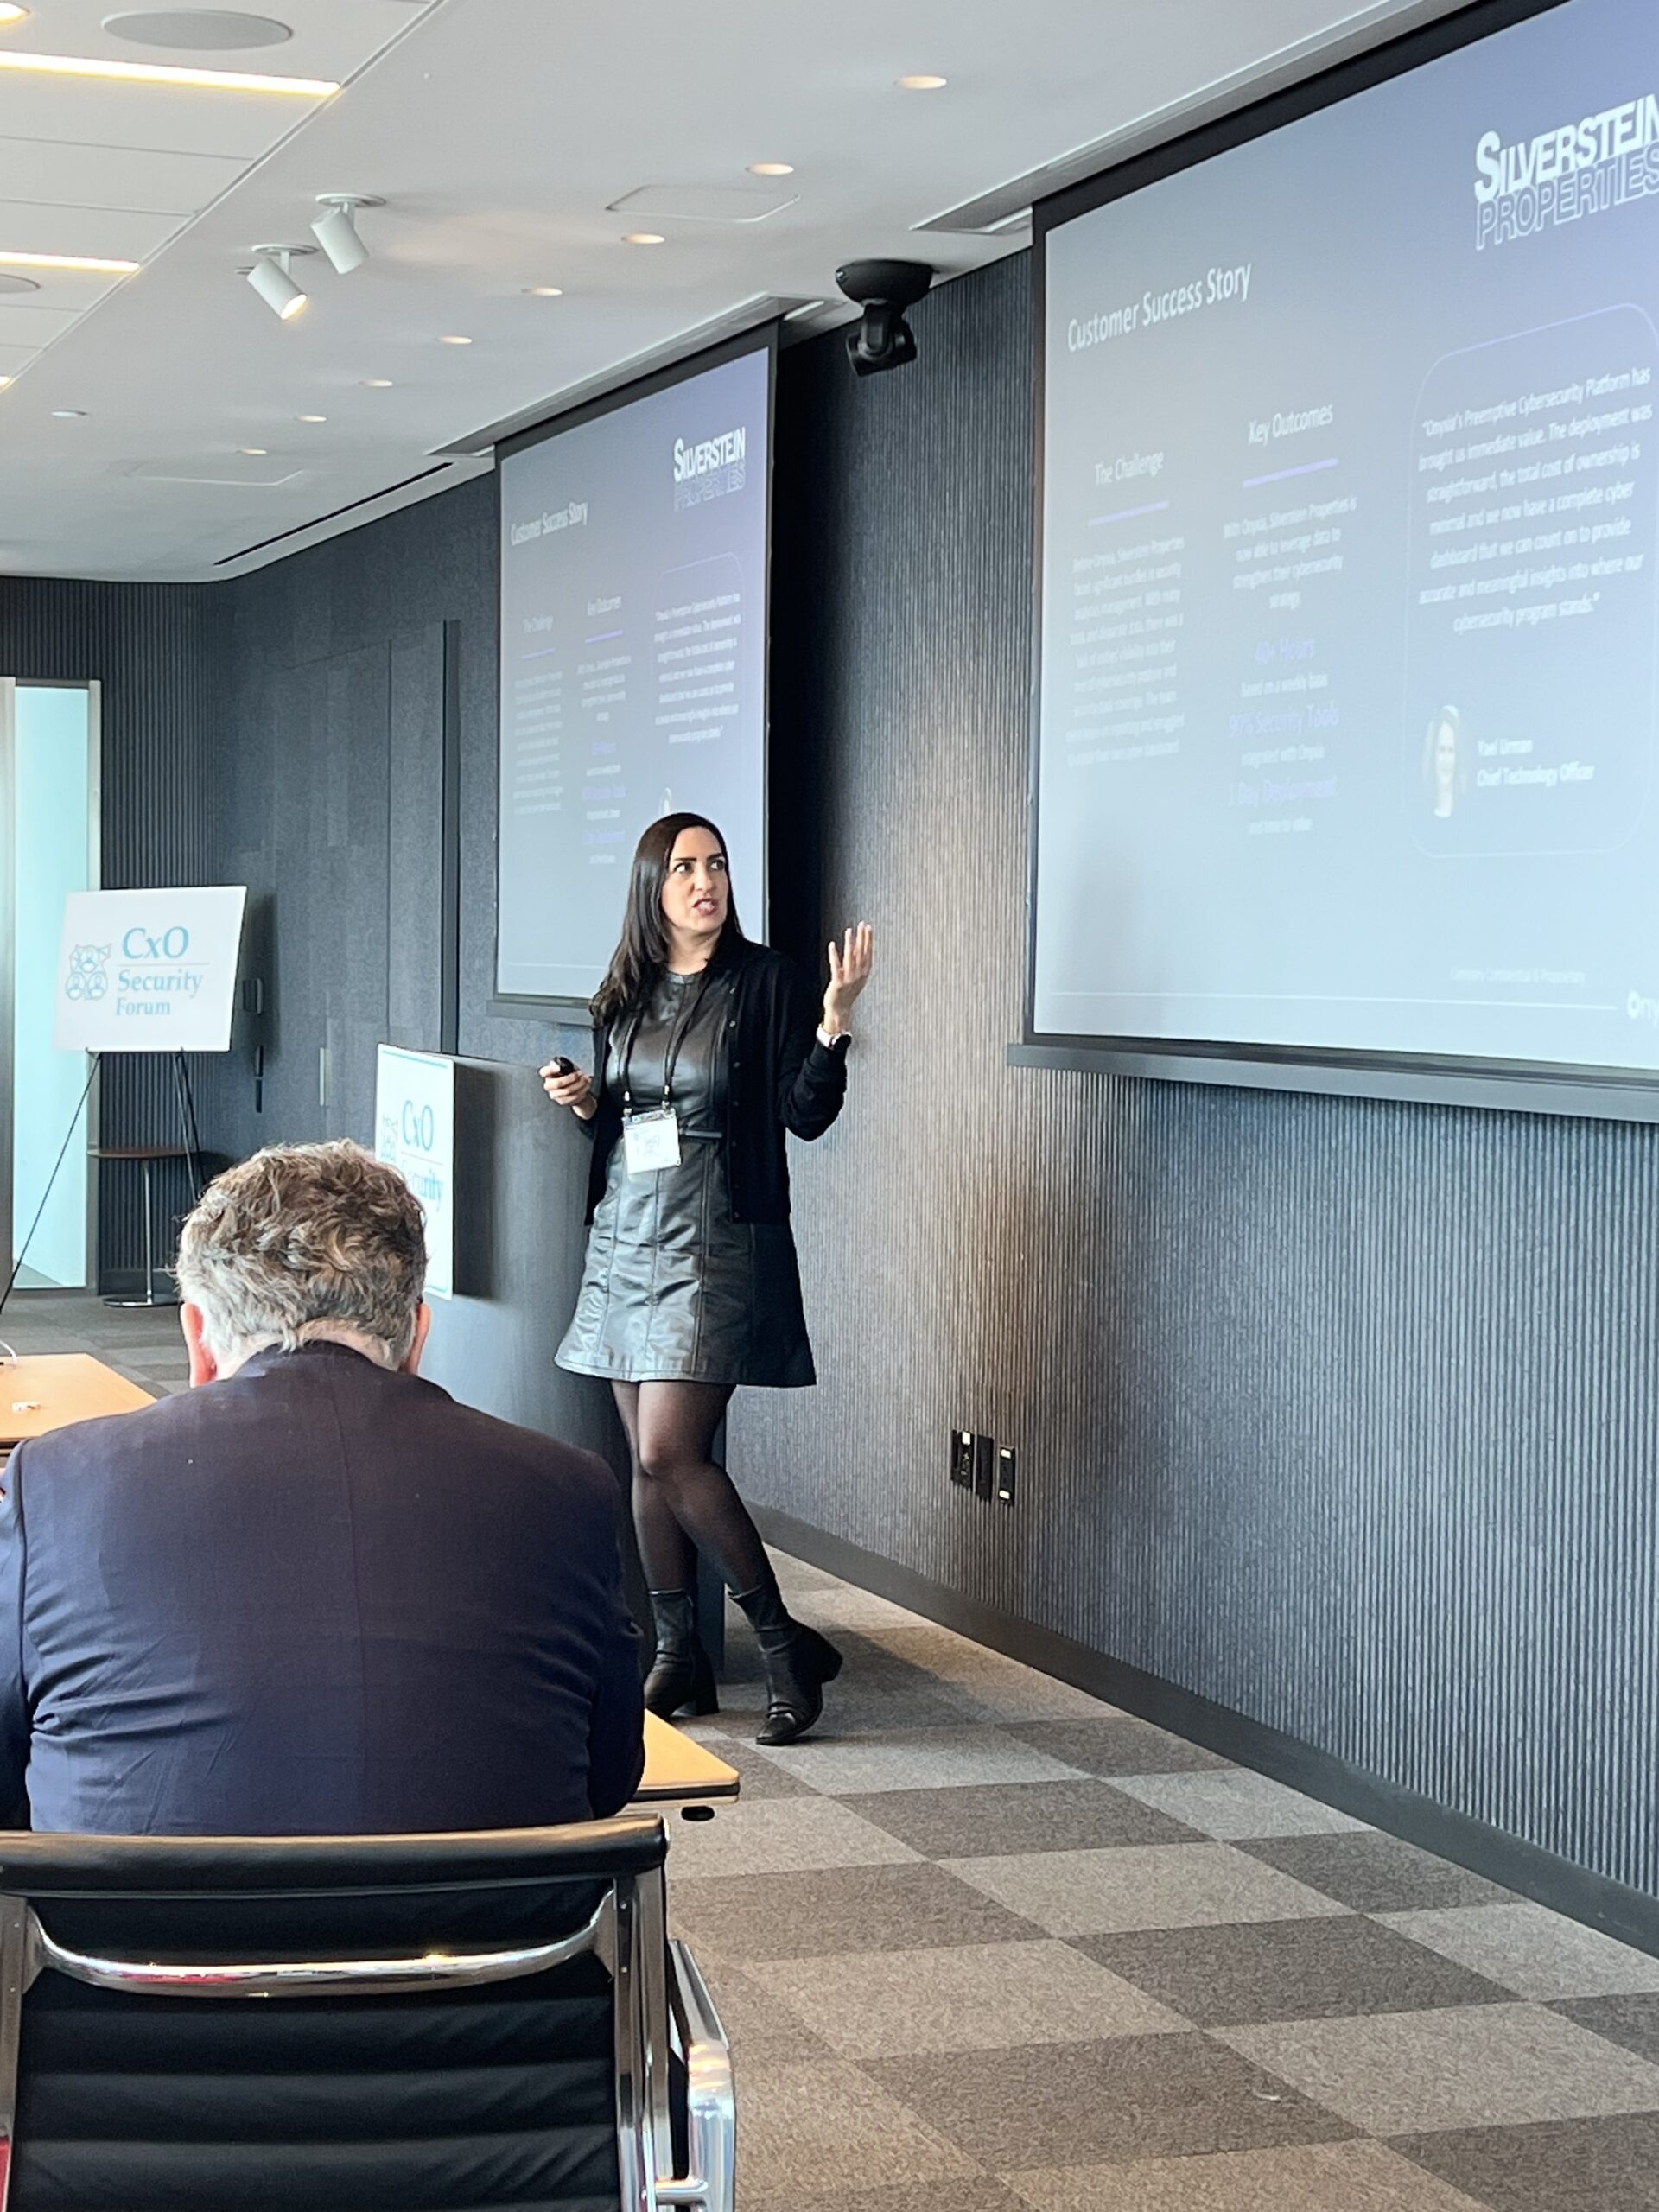
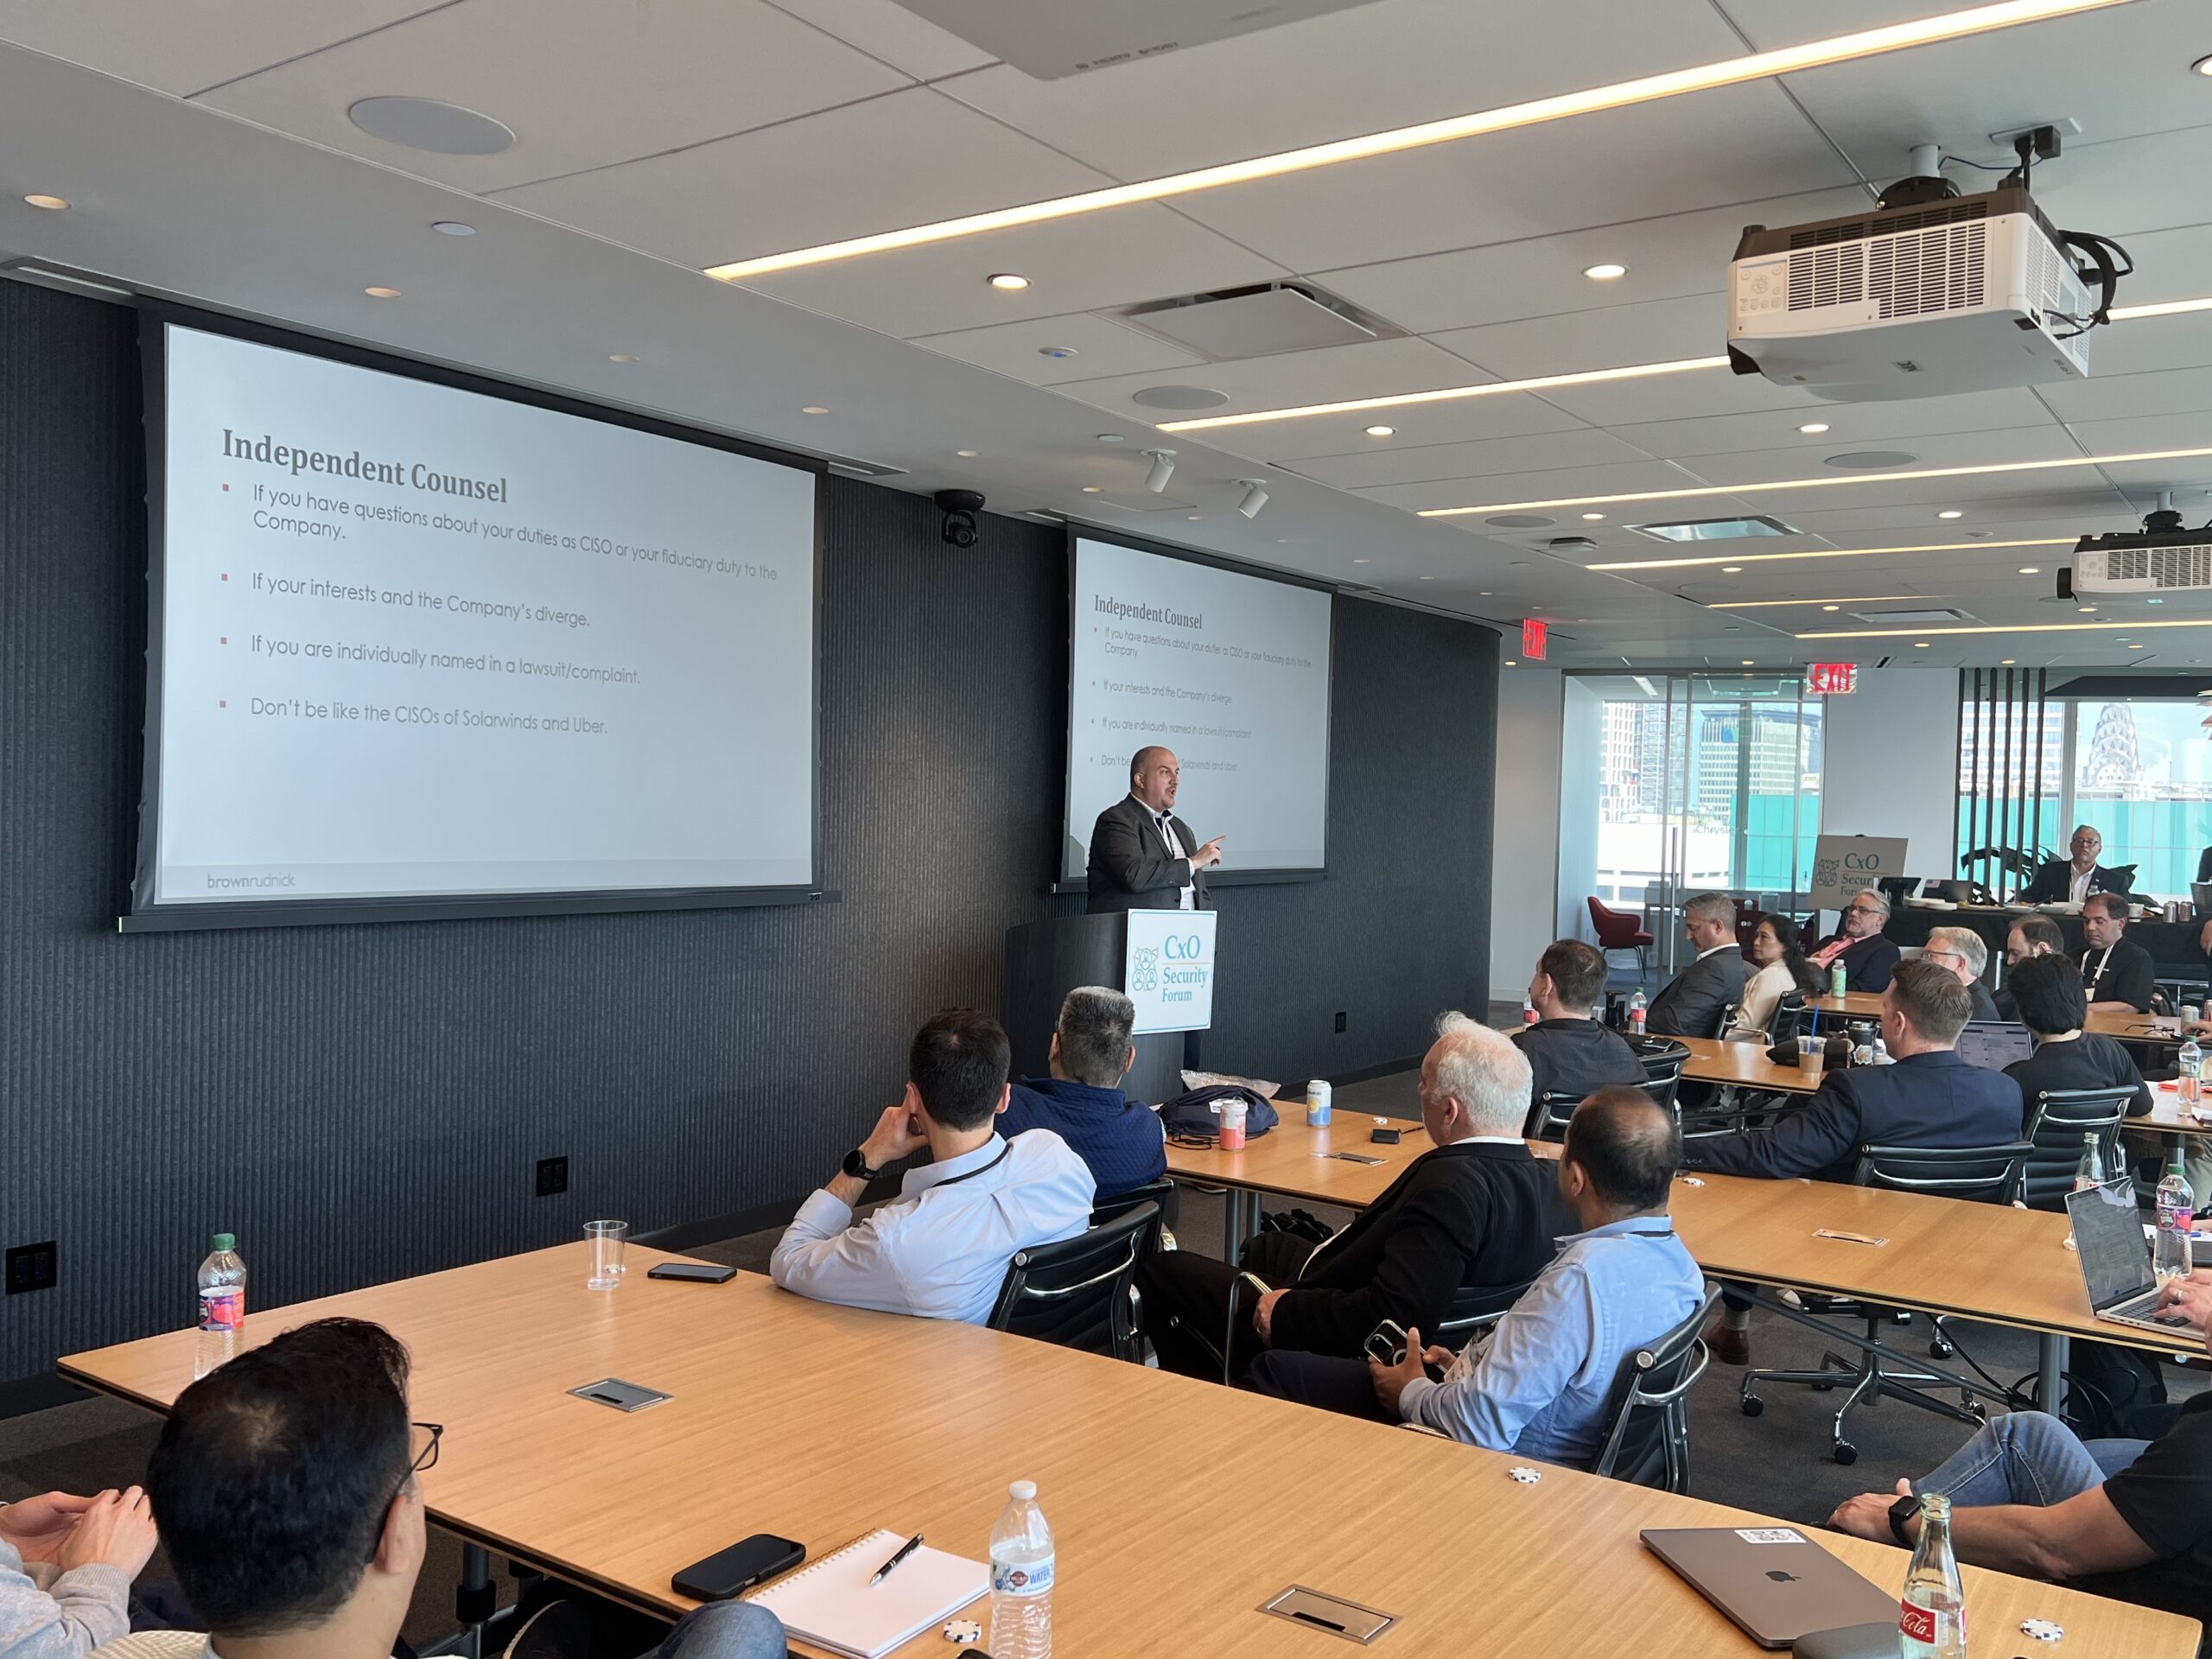
About CxO Forum
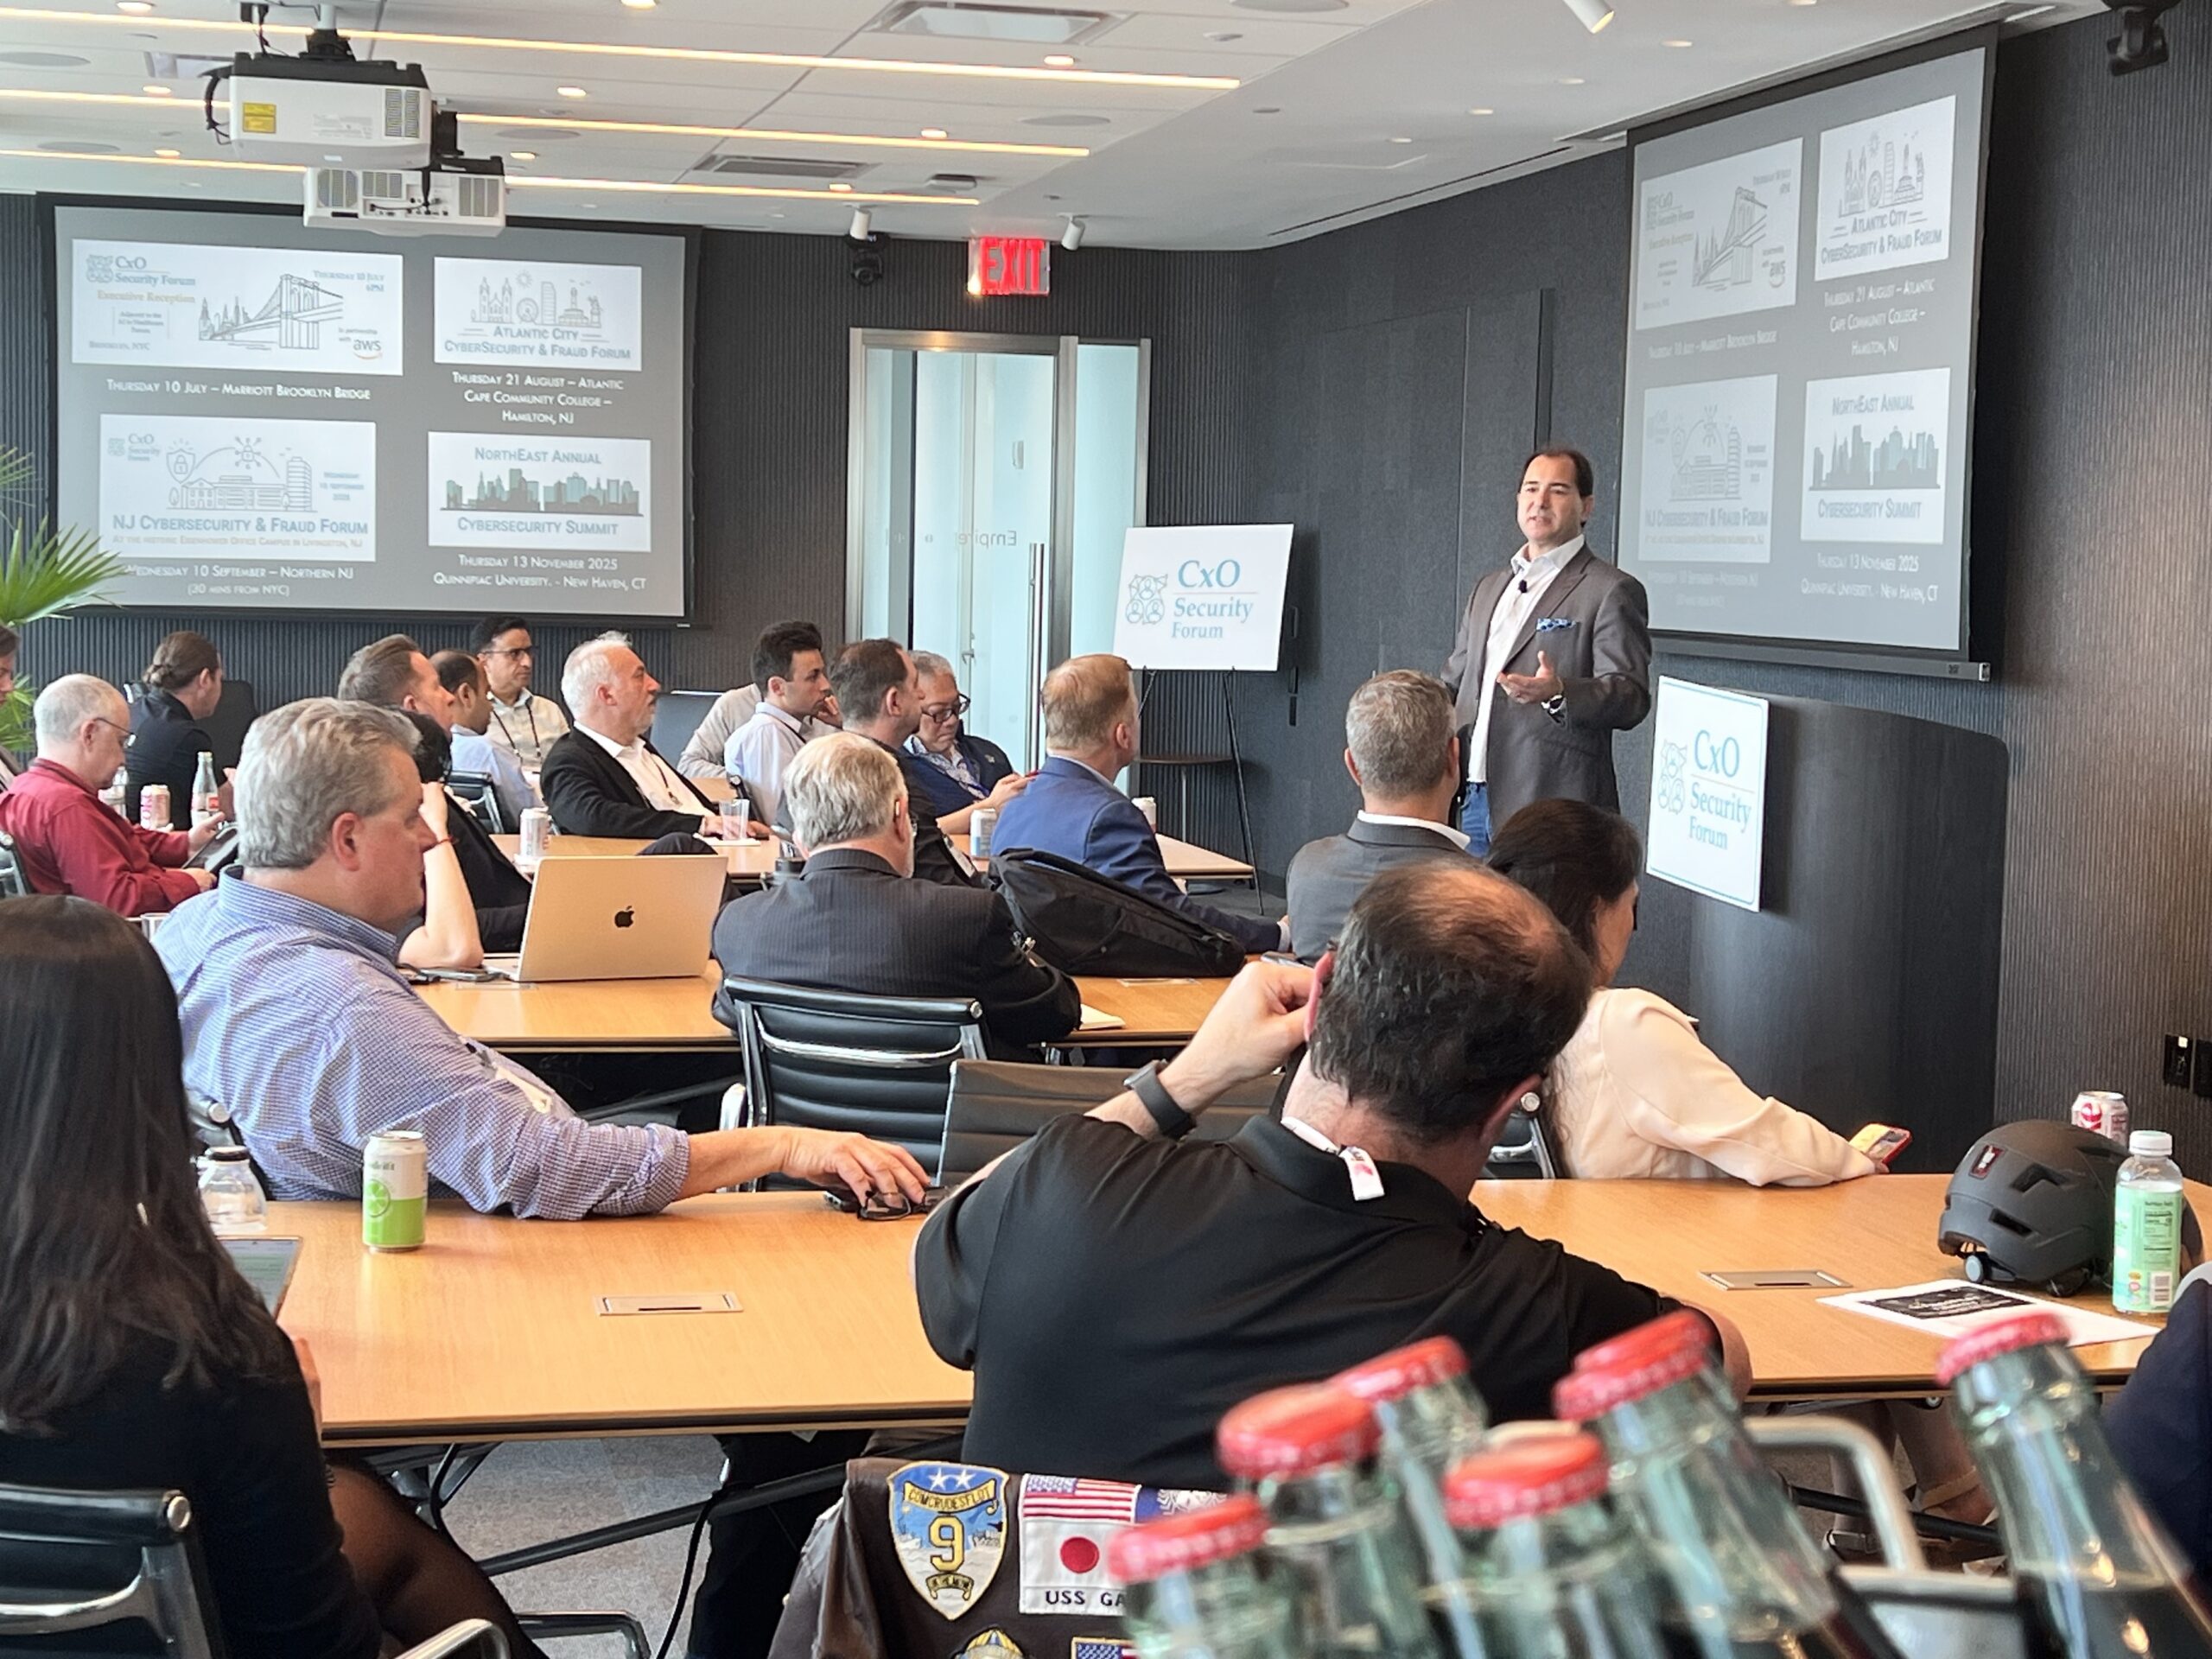
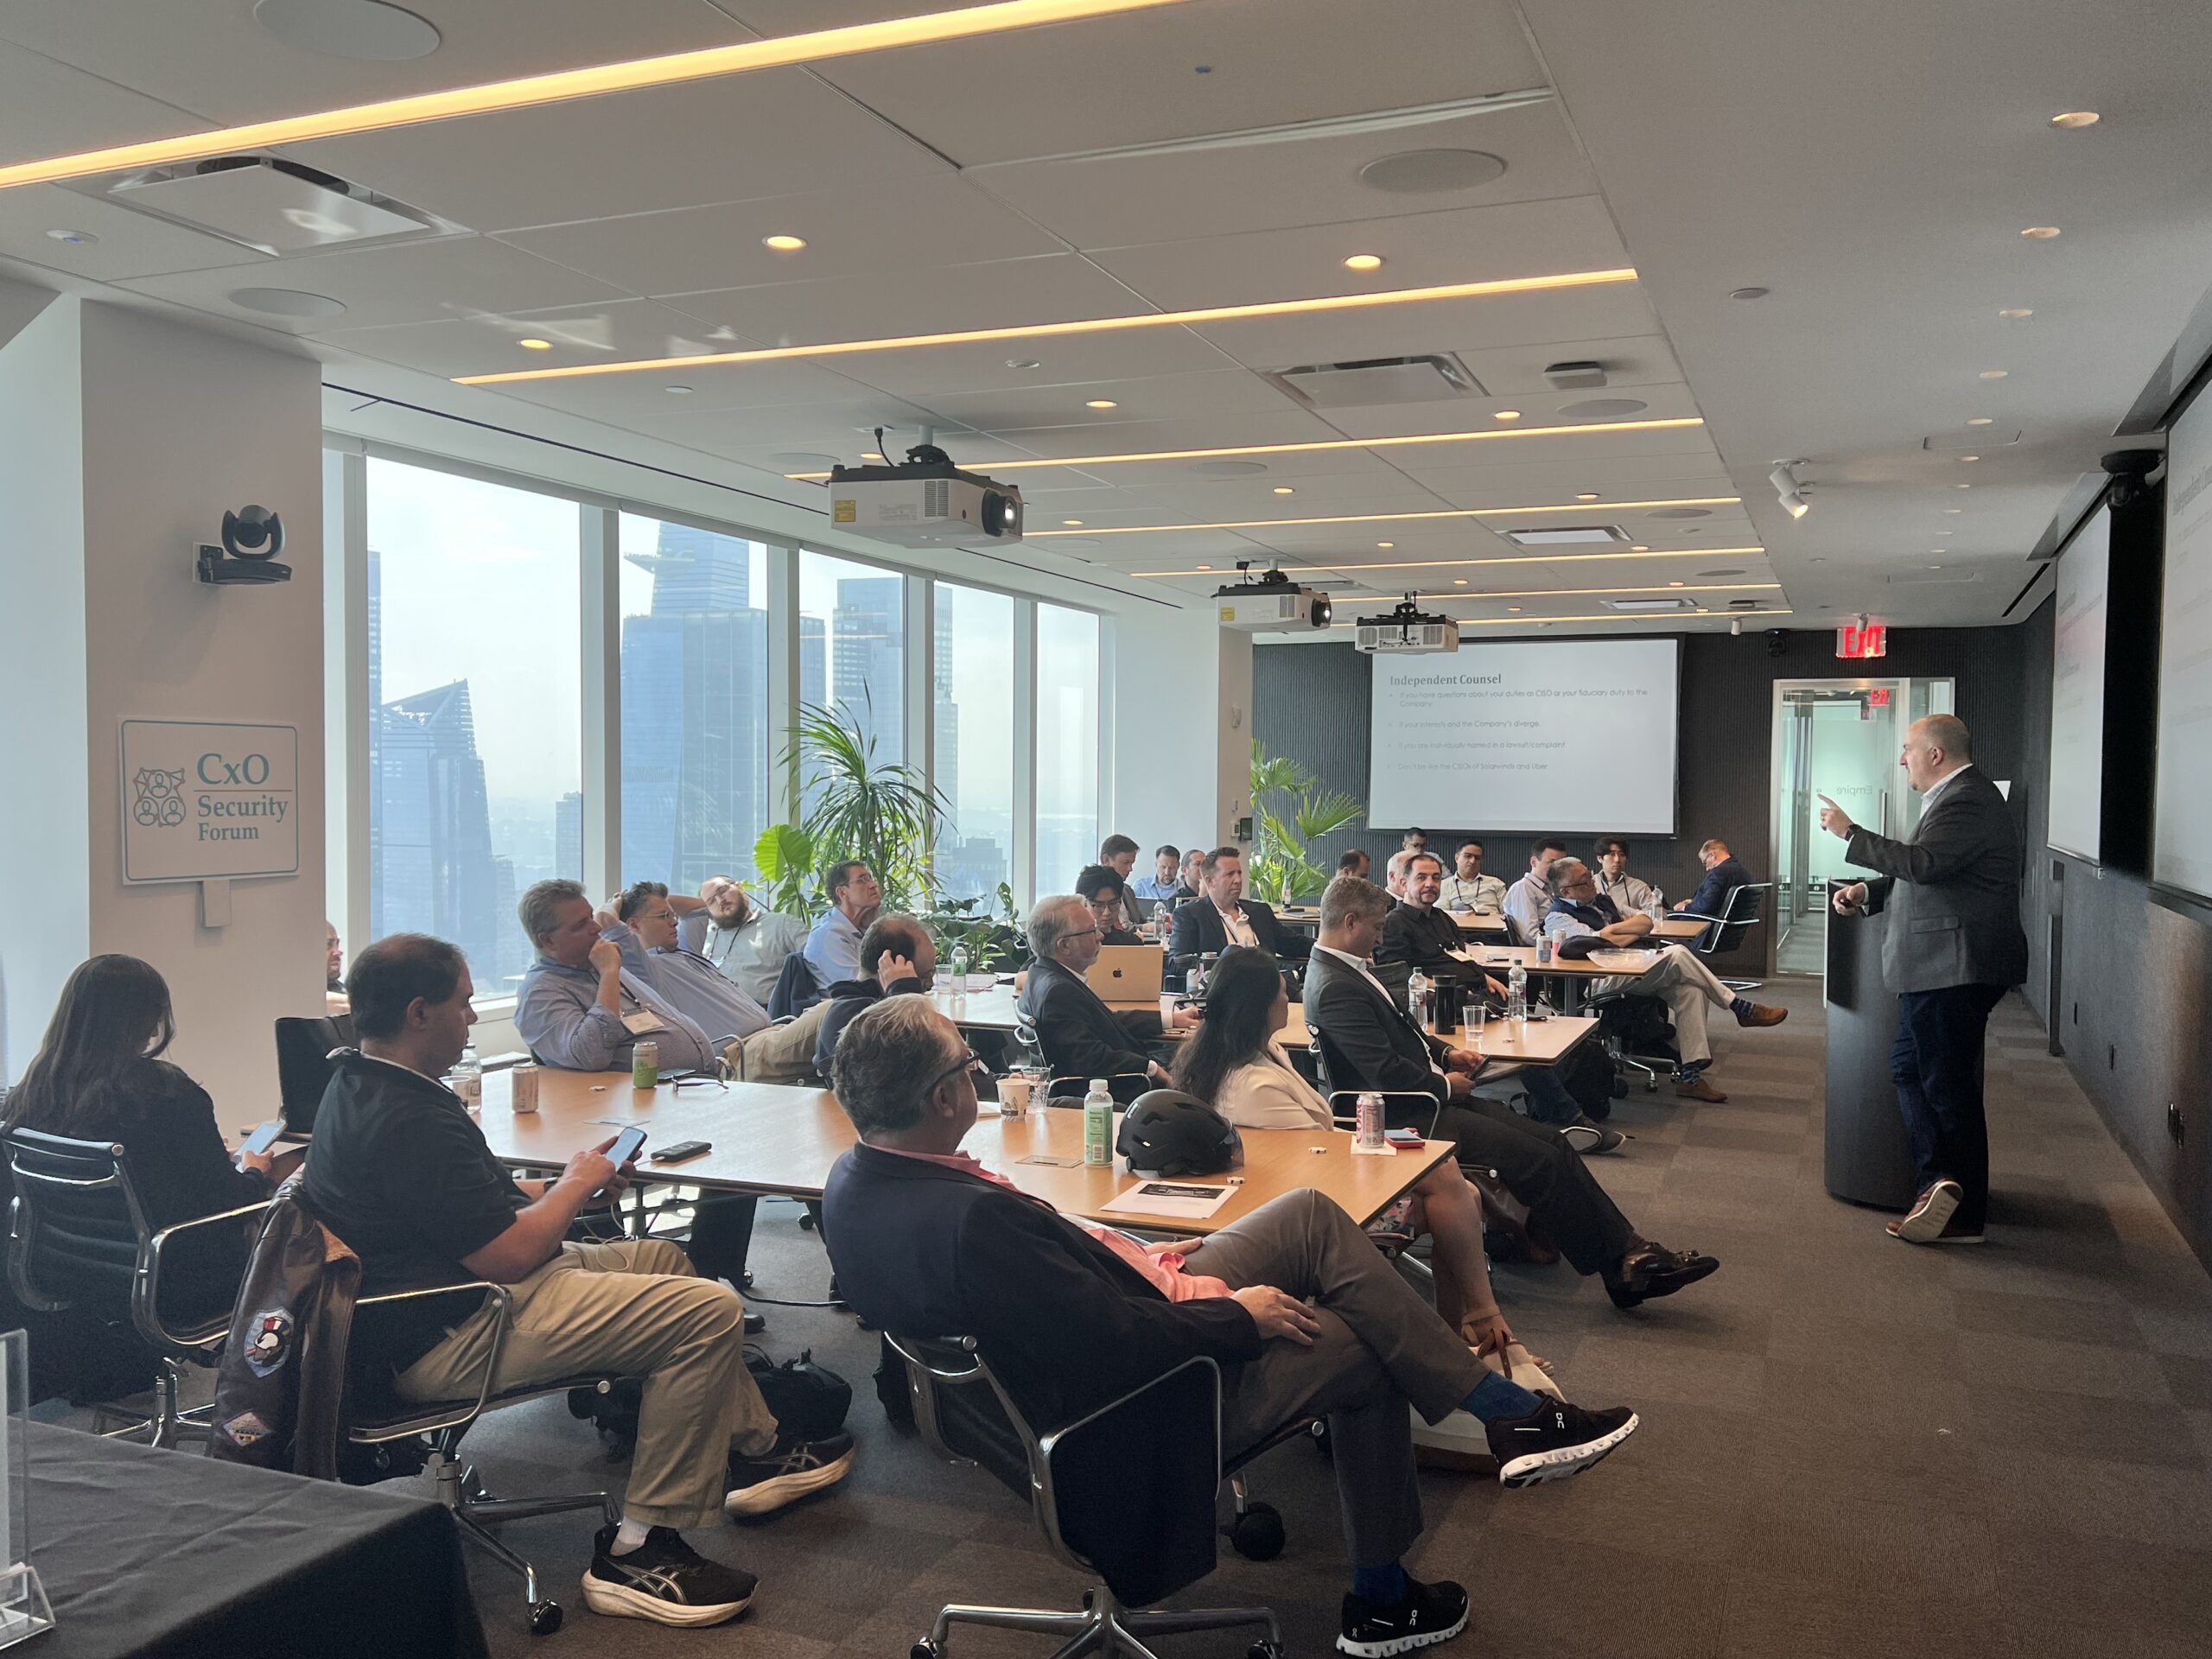
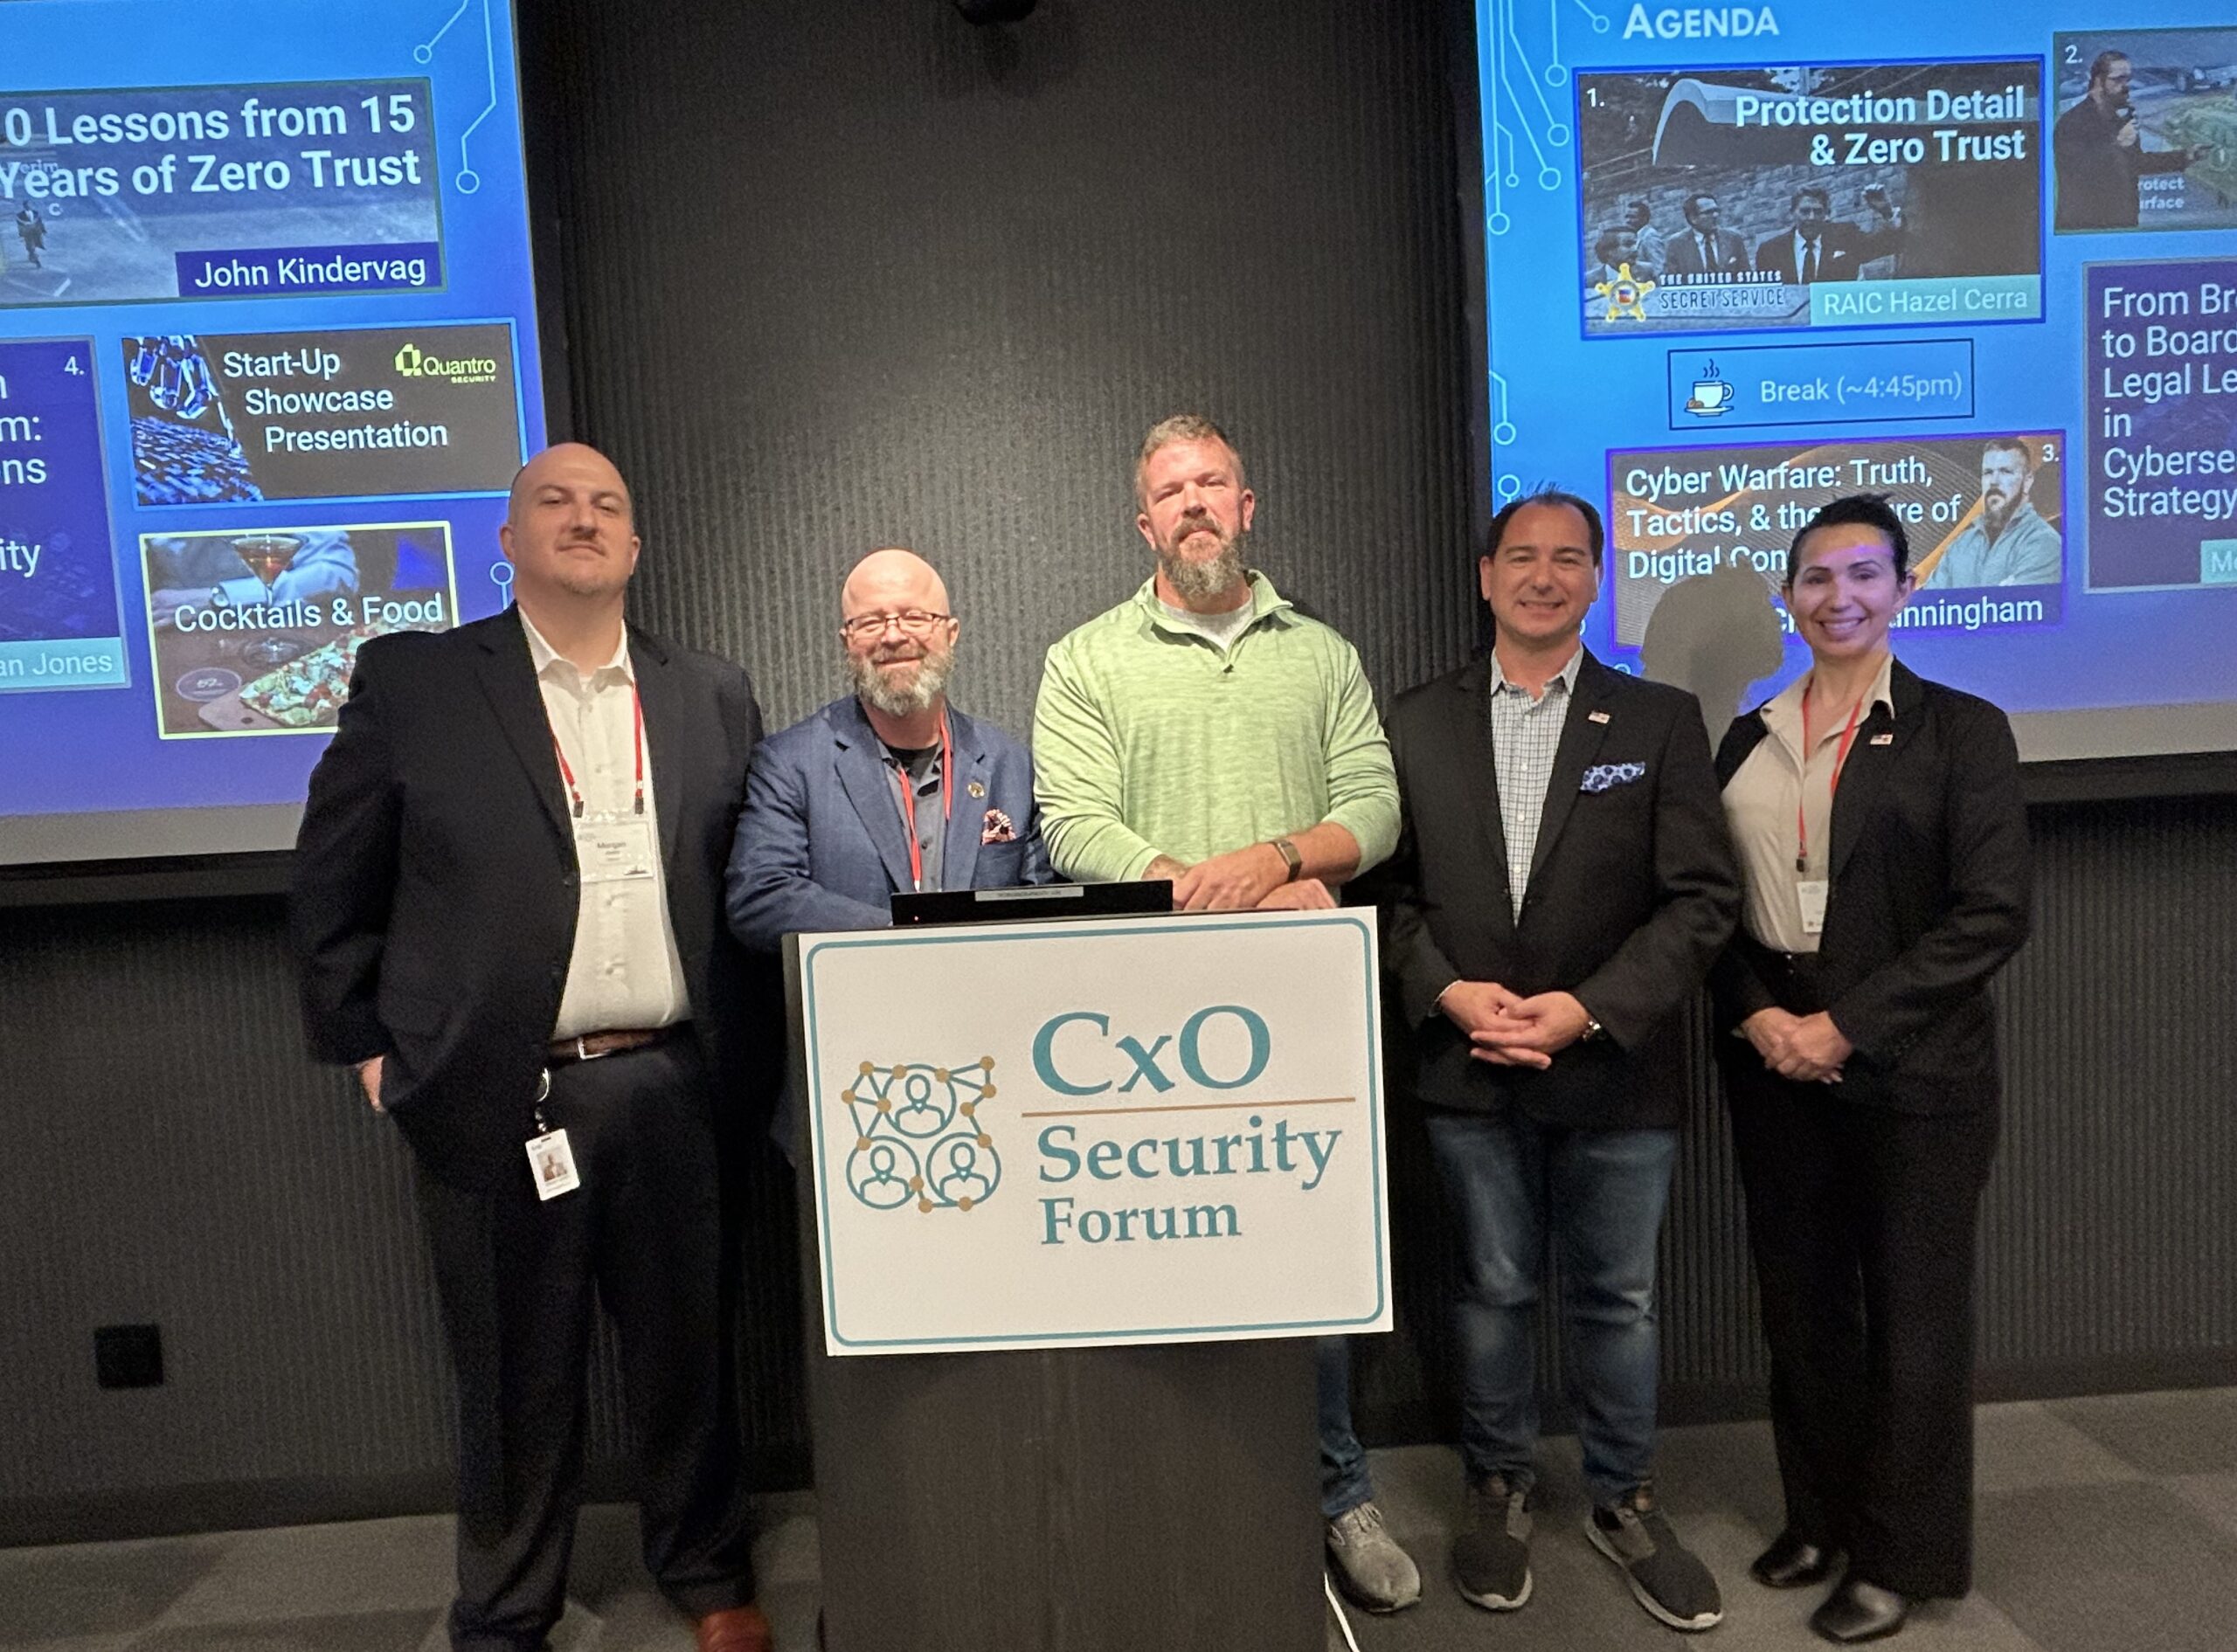
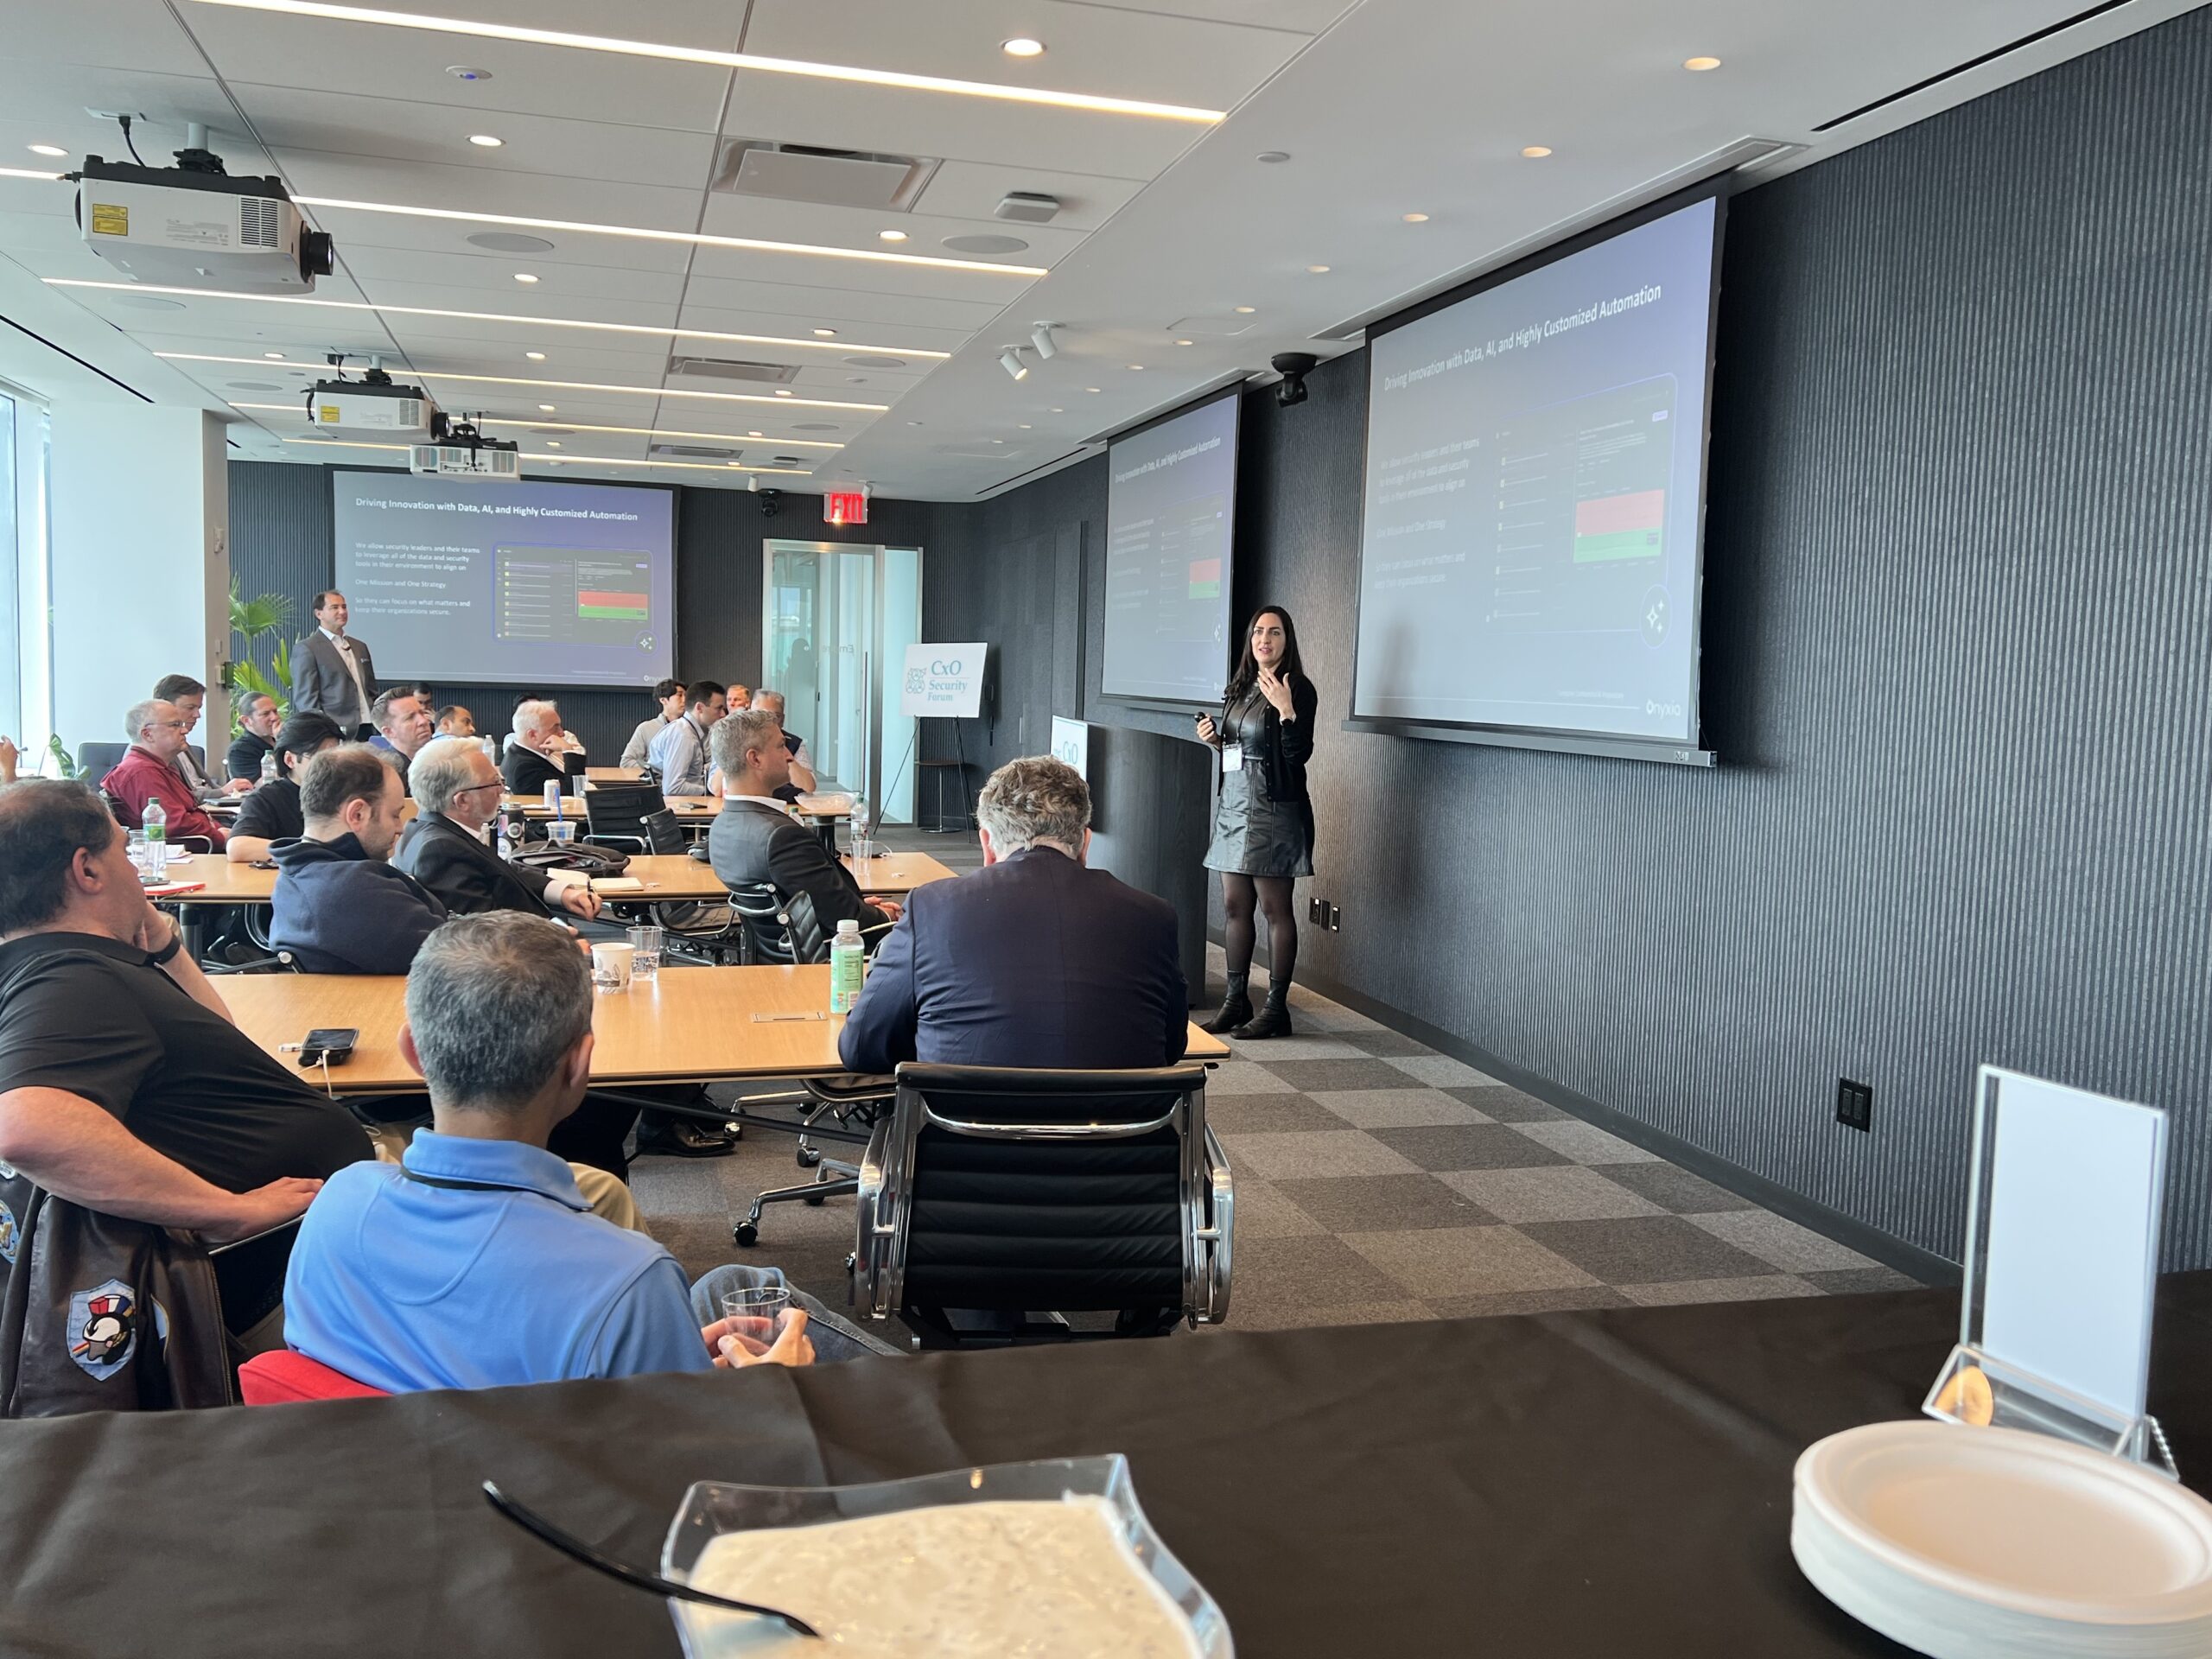
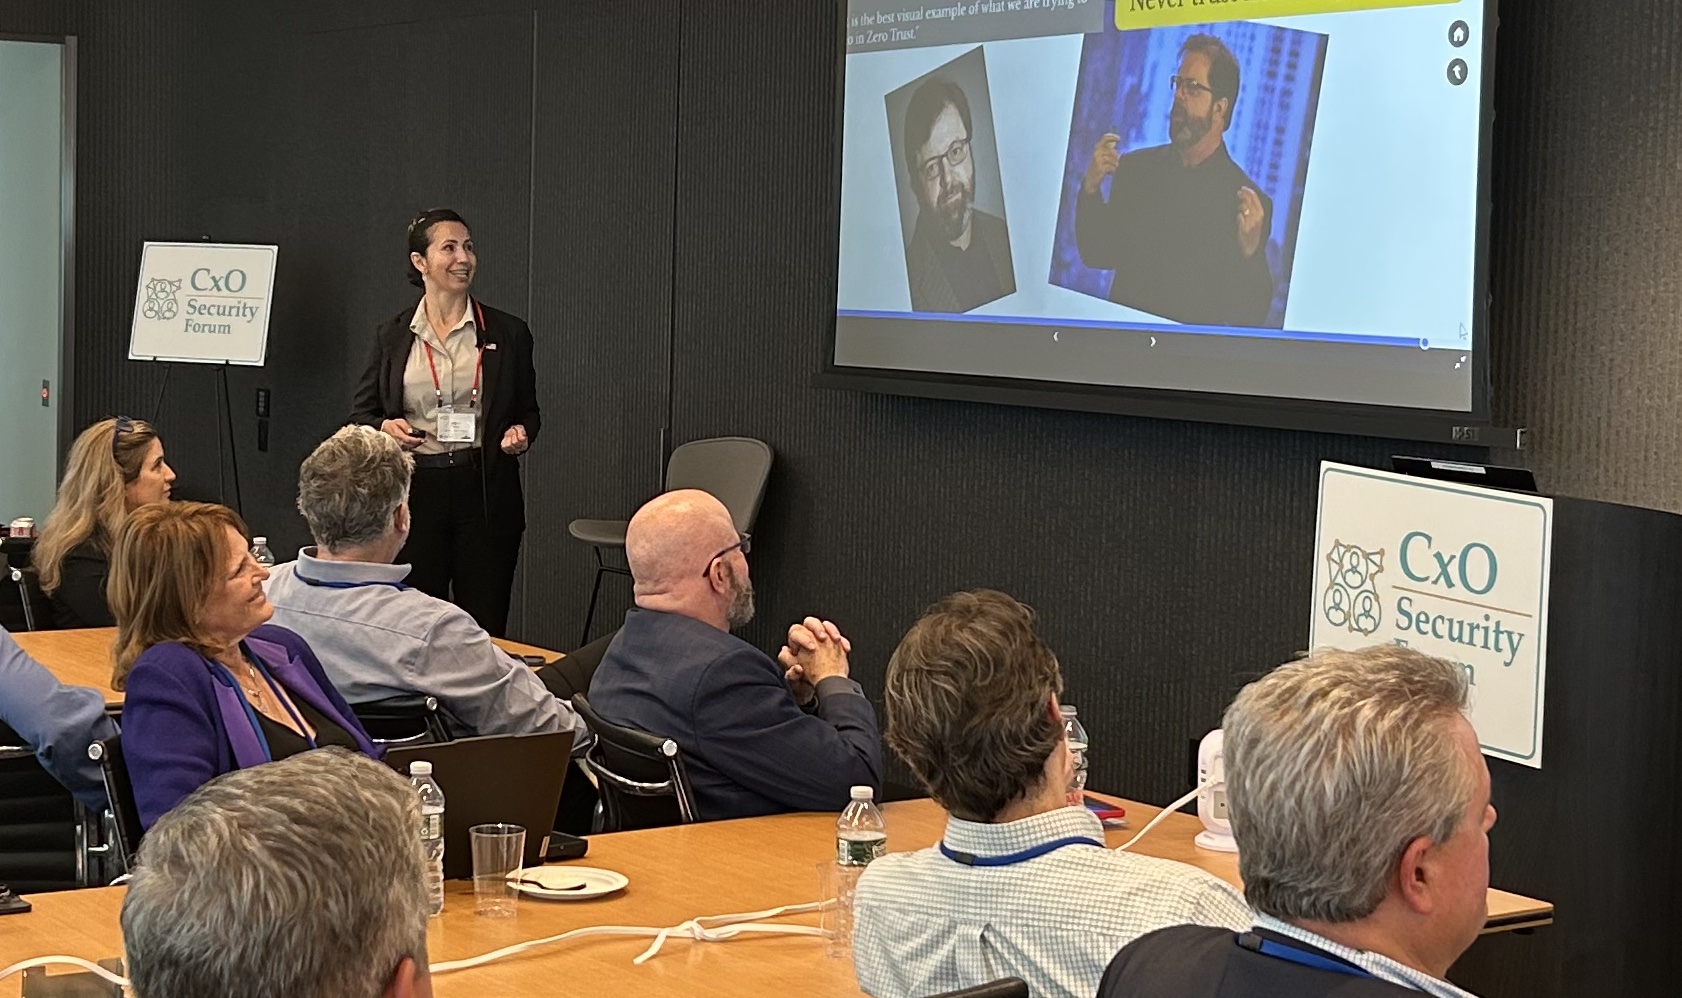
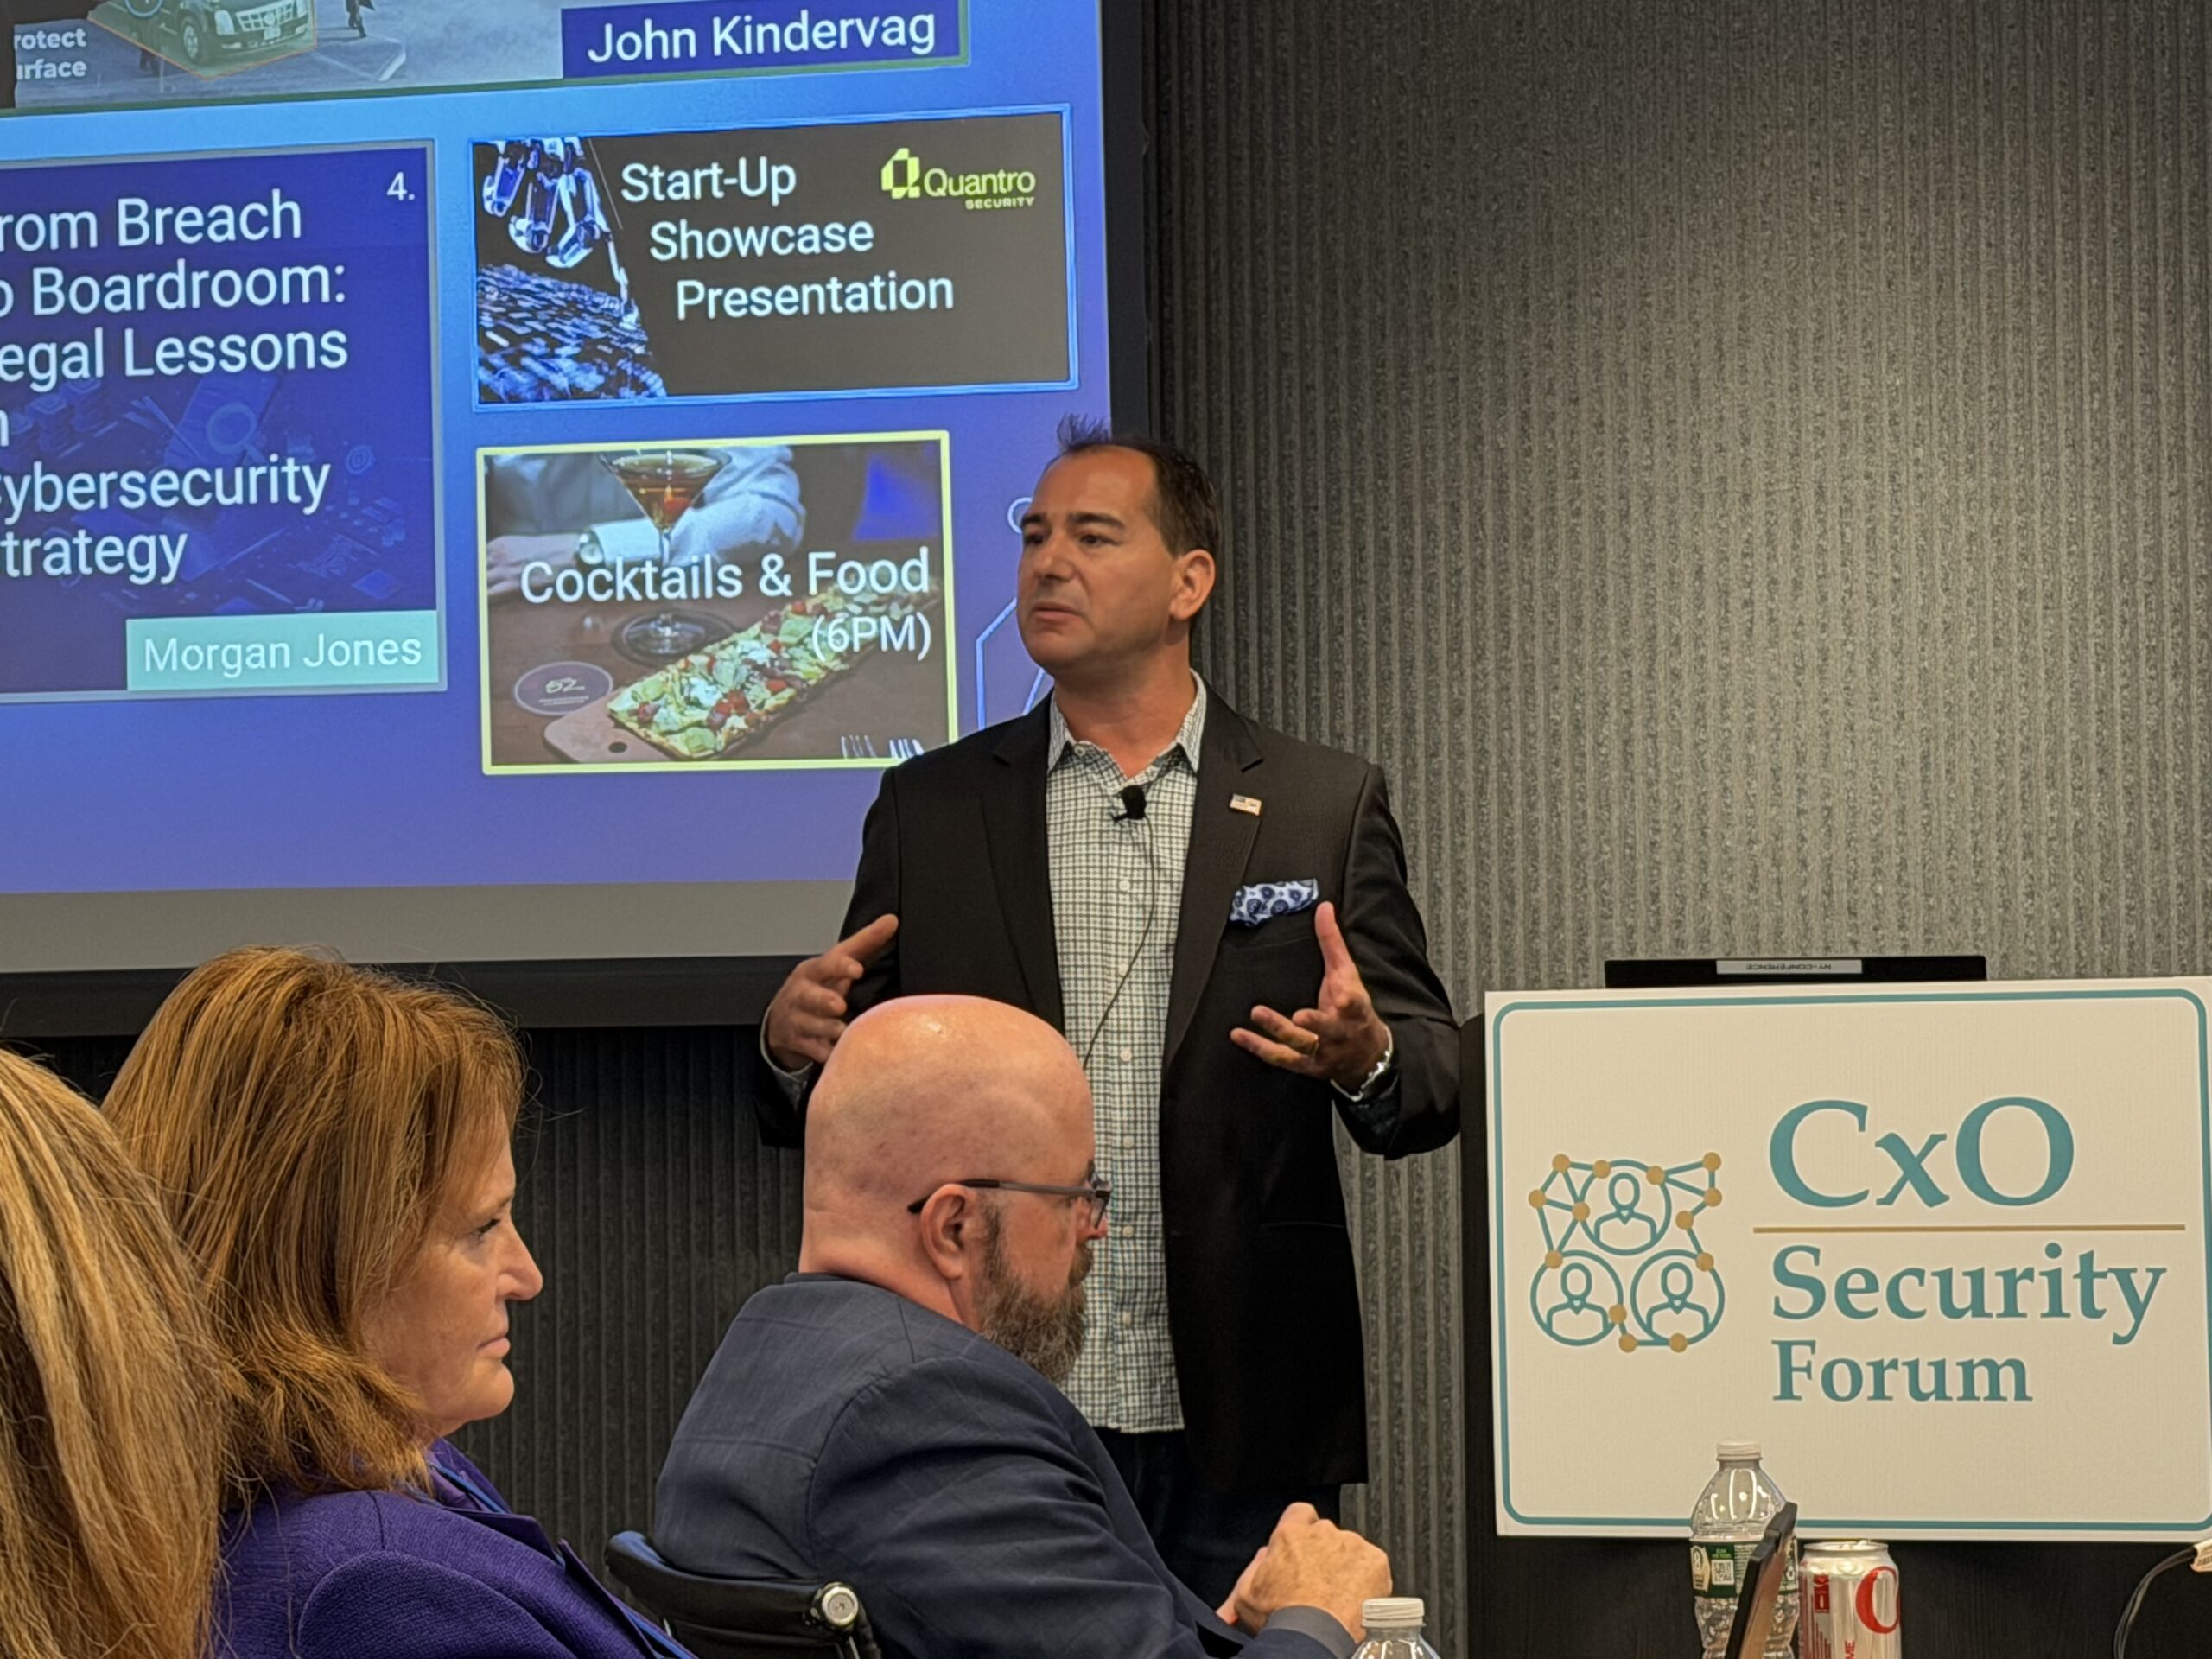
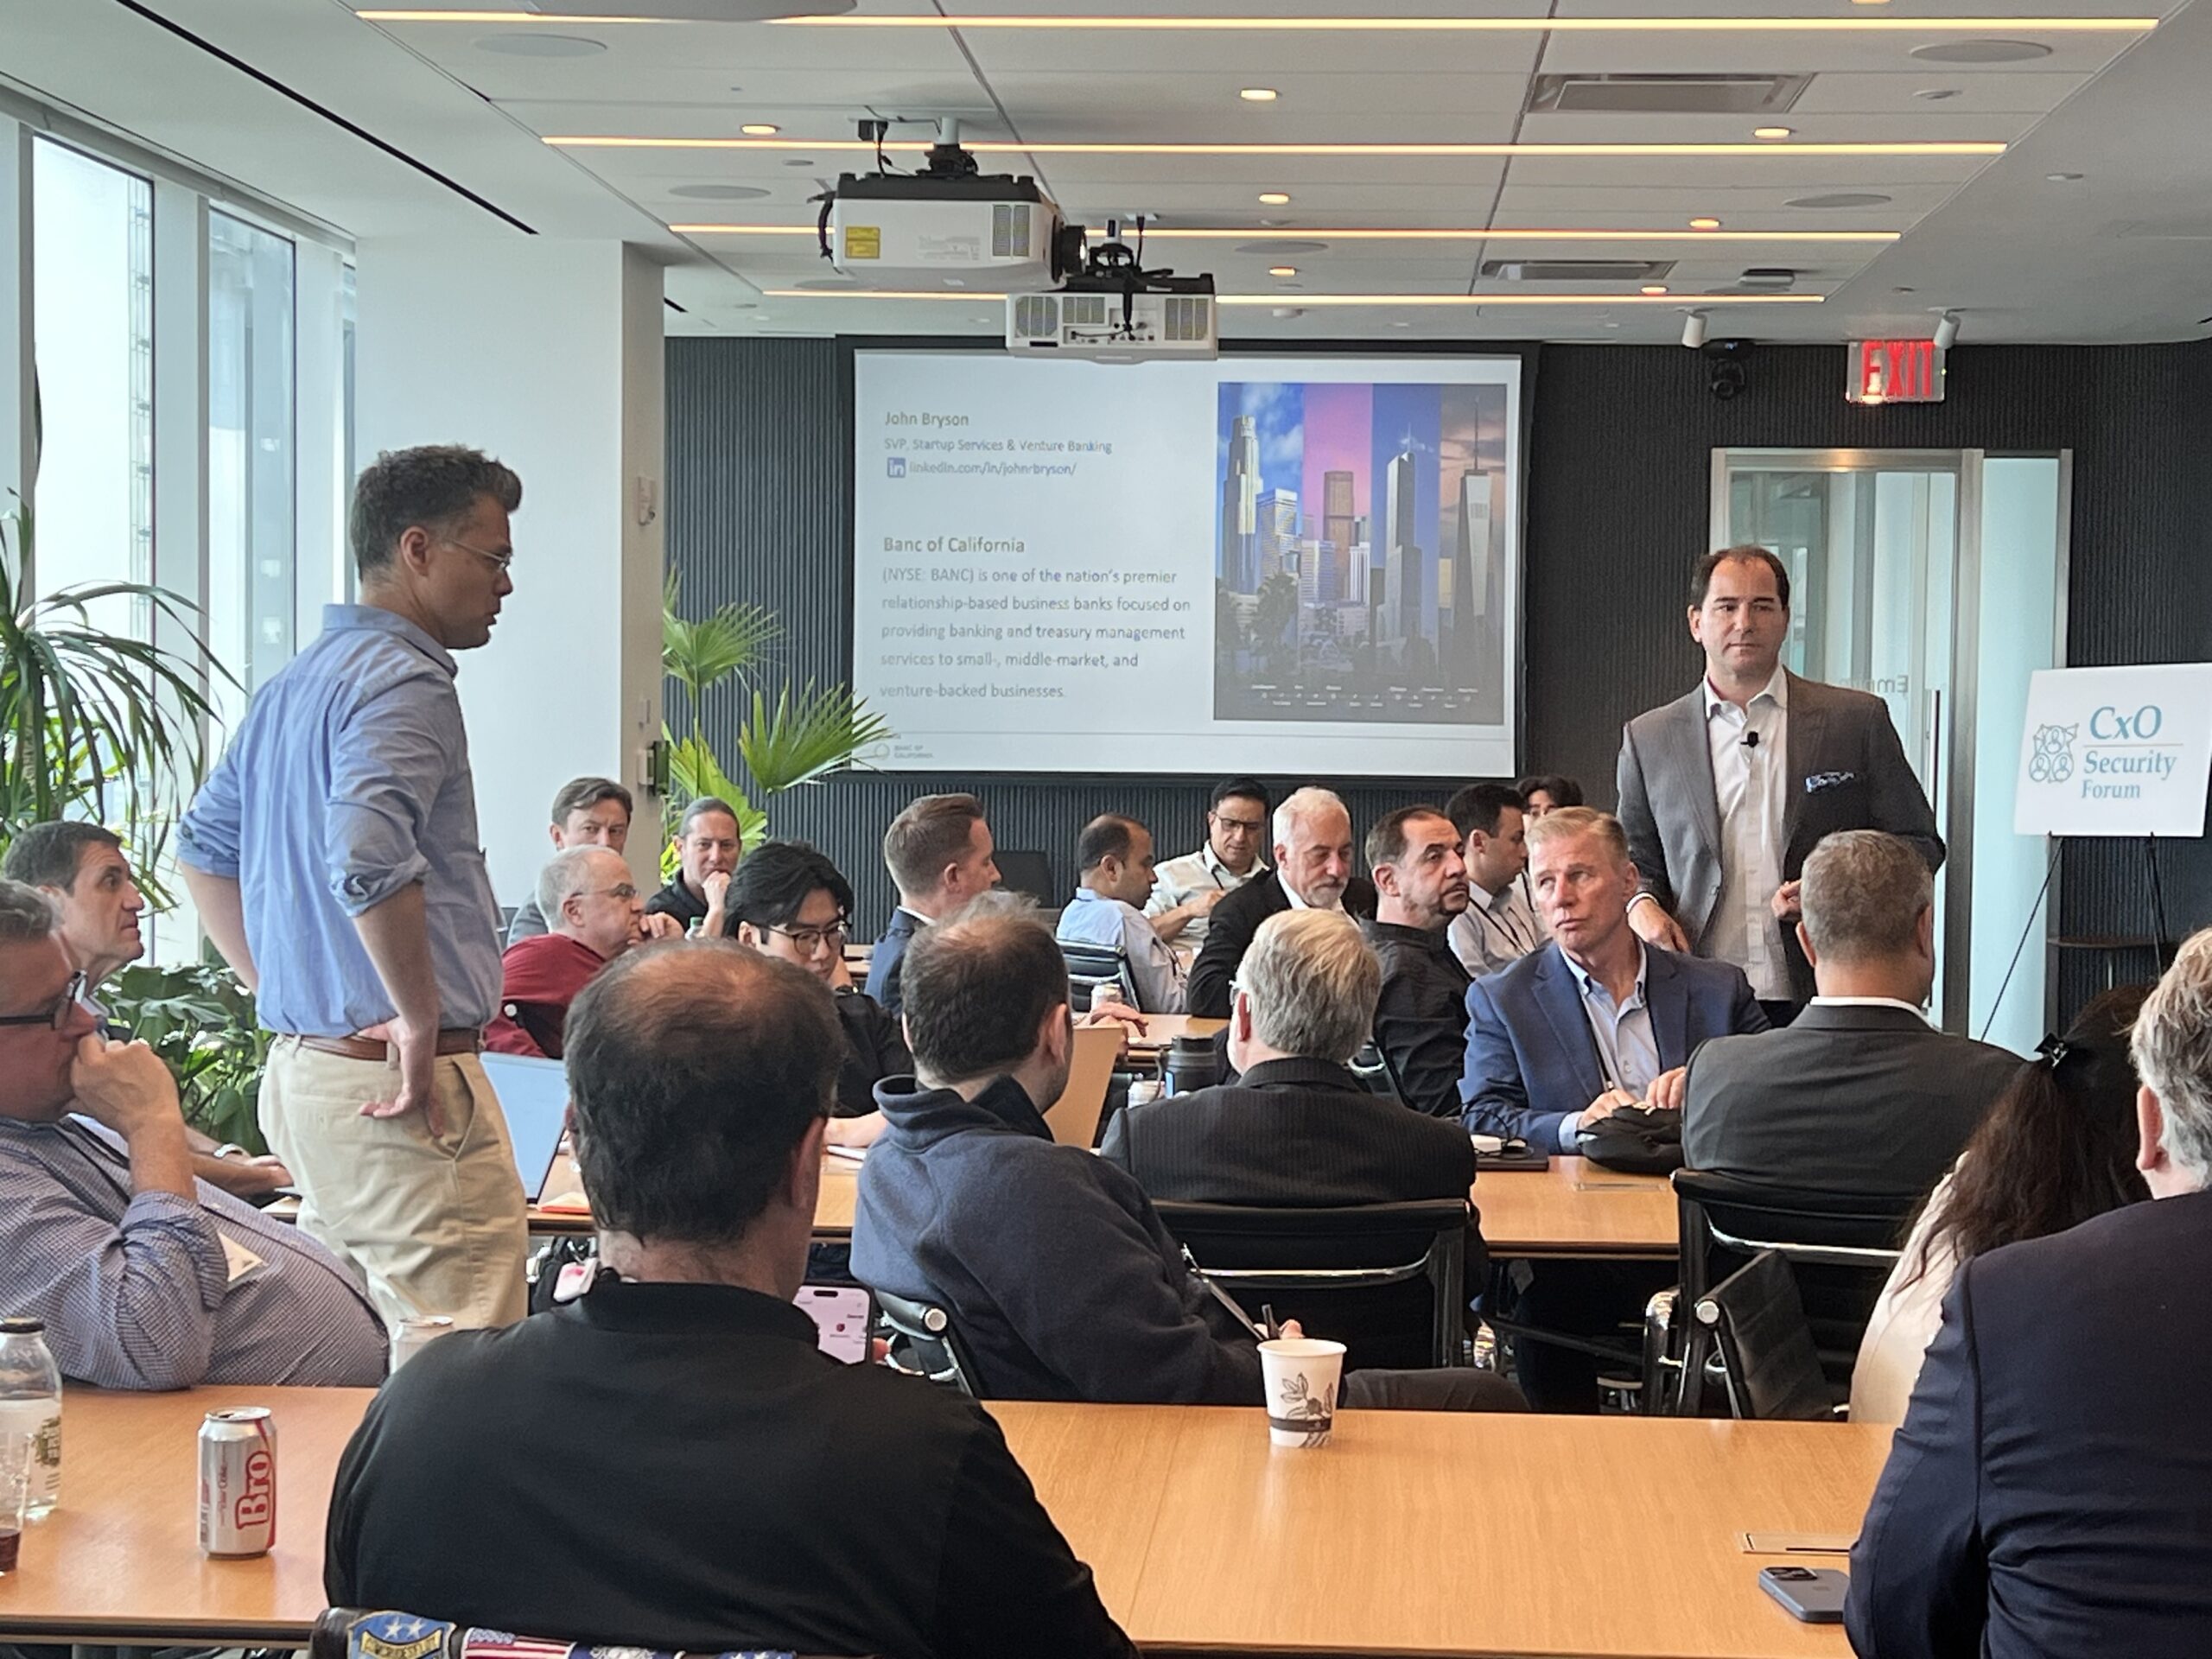
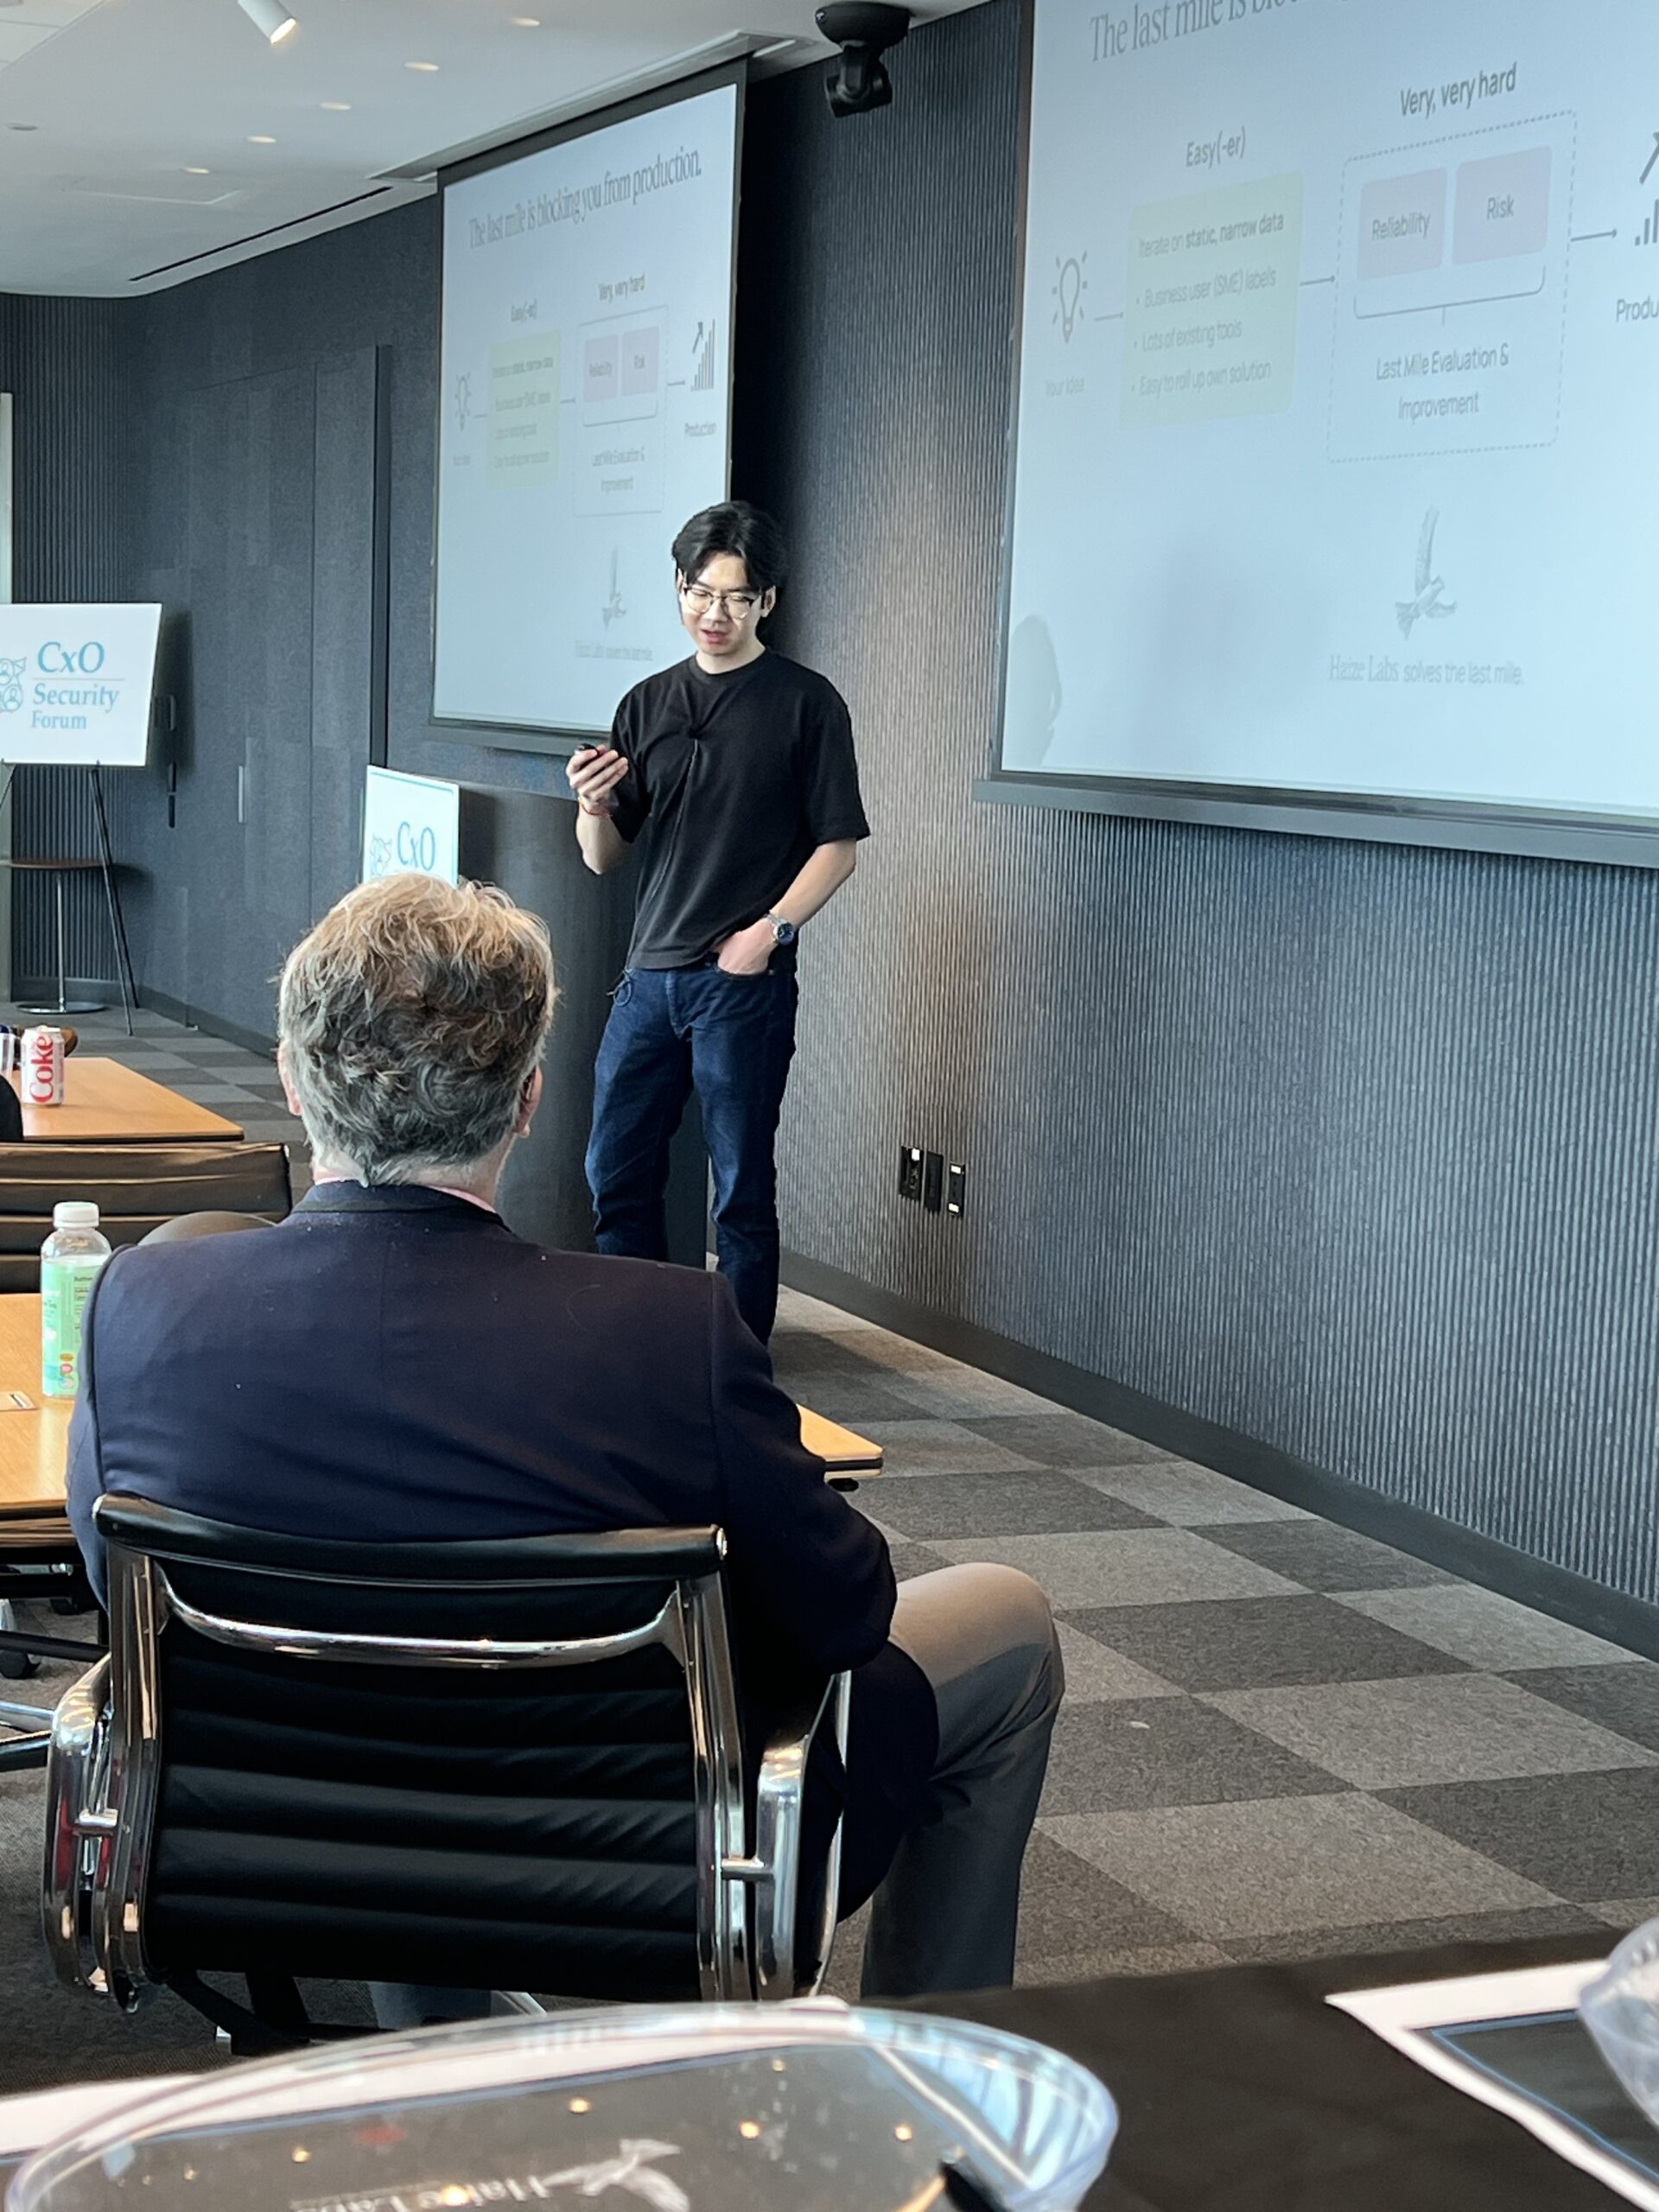
CxO Security Forum began as a response to a common frustration among senior cybersecurity leaders: the way enterprise solutions are marketed, sold, and evaluated is fundamentally broken. What started as a call for change has grown into a trusted community that puts executive practitioners at the center of the conversation.
We bring together CISOs, CIOs, and senior decision-makers who are responsible for protecting their organizations, guiding strategic risk, and navigating the evolving role of AI in security. Every forum, gathering, and conversation is designed to foster education, mentoring, and authentic peer connection.
What makes us different is our focus on relationships. Our events are intentionally small, curated, and built for real dialogue. Sponsors are carefully selected, and there are no product pitches. Participants come for thoughtful, actionable conversations that support both professional development and practical decision-making.
At CxO Security Forum, the goal is simple. Give experienced leaders a space to learn from one another, to share insight, and to build meaningful connections that last beyond the event itself.
Participation is free for qualified senior executives
Location
DLA Piper
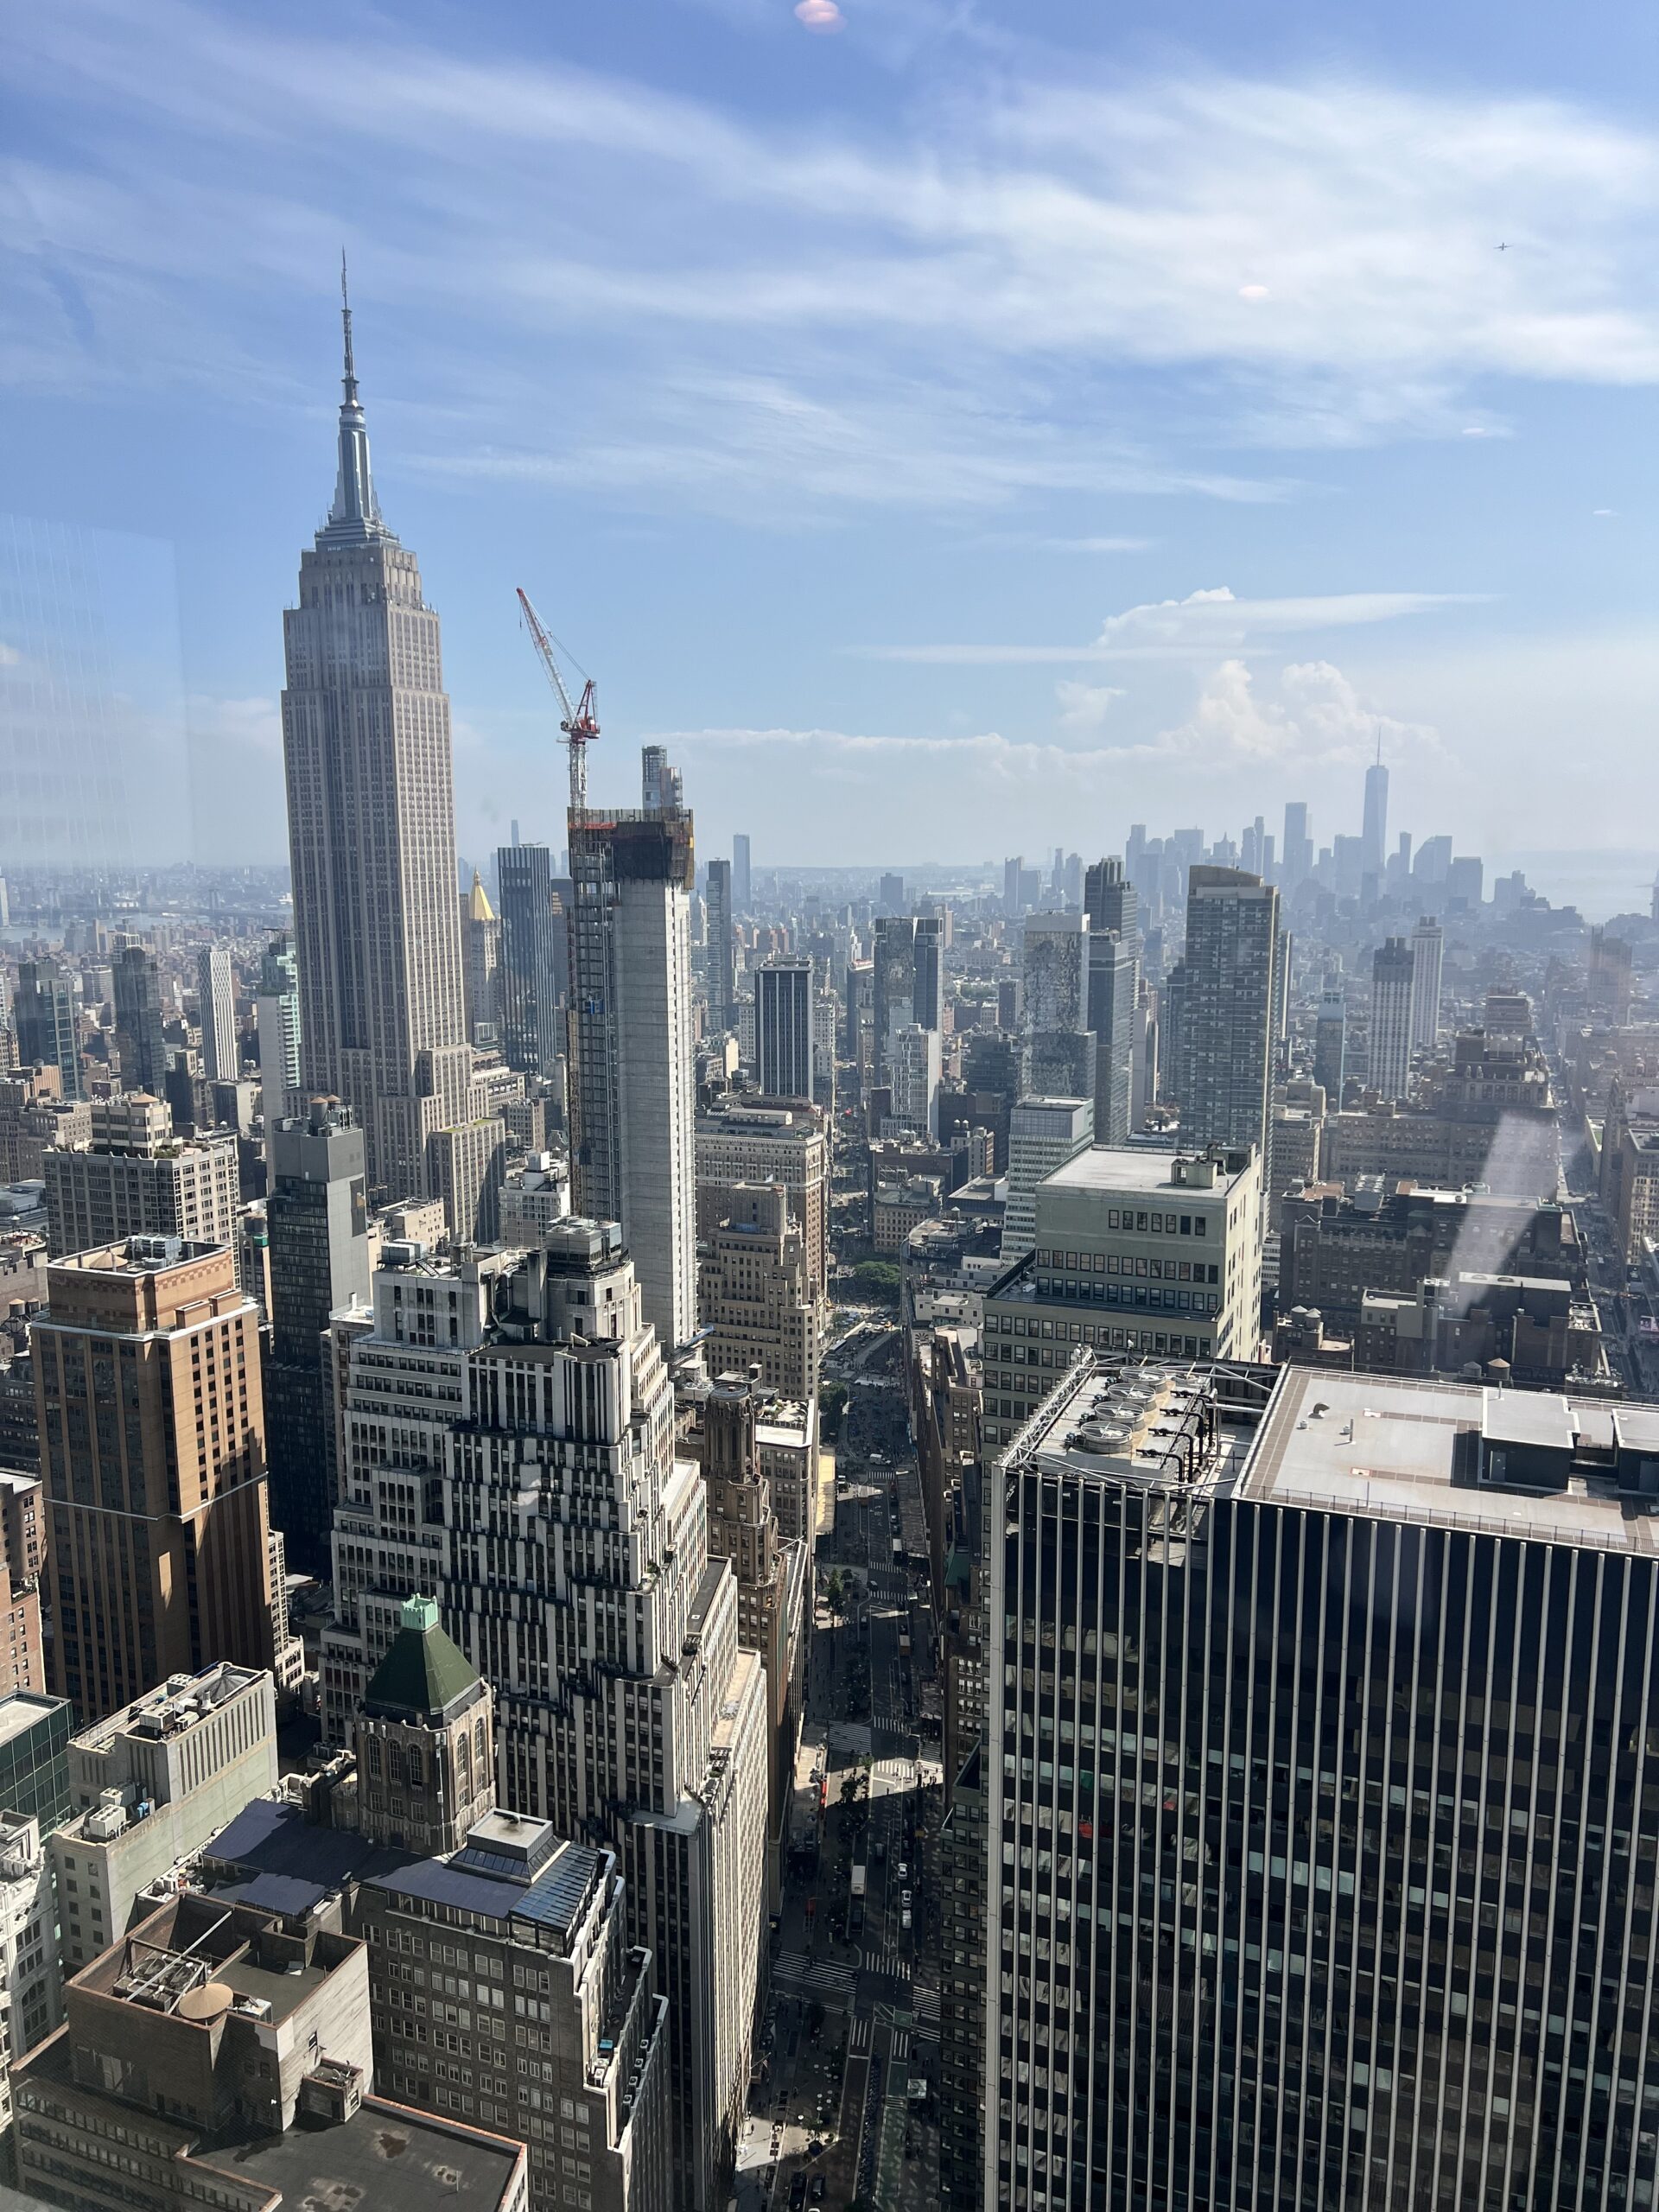
1251 Avenue of the Americas, 27th Floor New York, NY 10020
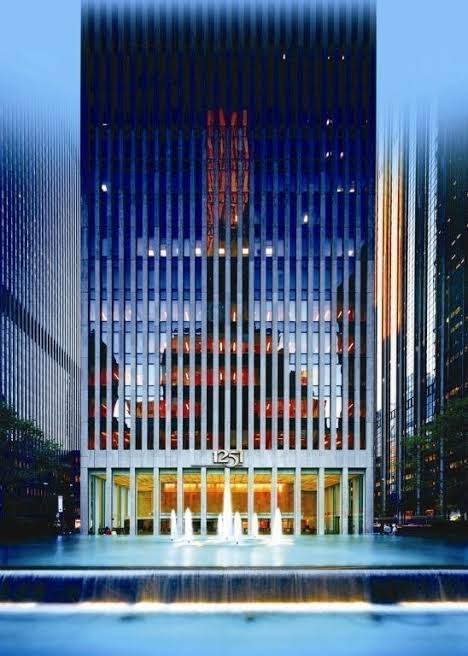
1251 Avenue of the Americas, New York City
© 2026 CxO Security Forum. All rights reserved