Boston CxO Security Forum
Quarterly Executive Briefing
25 March 2027
Days
Hours
Minutes
Seconds
A Private, Peer-Led Forum for Cybersecurity Leaders
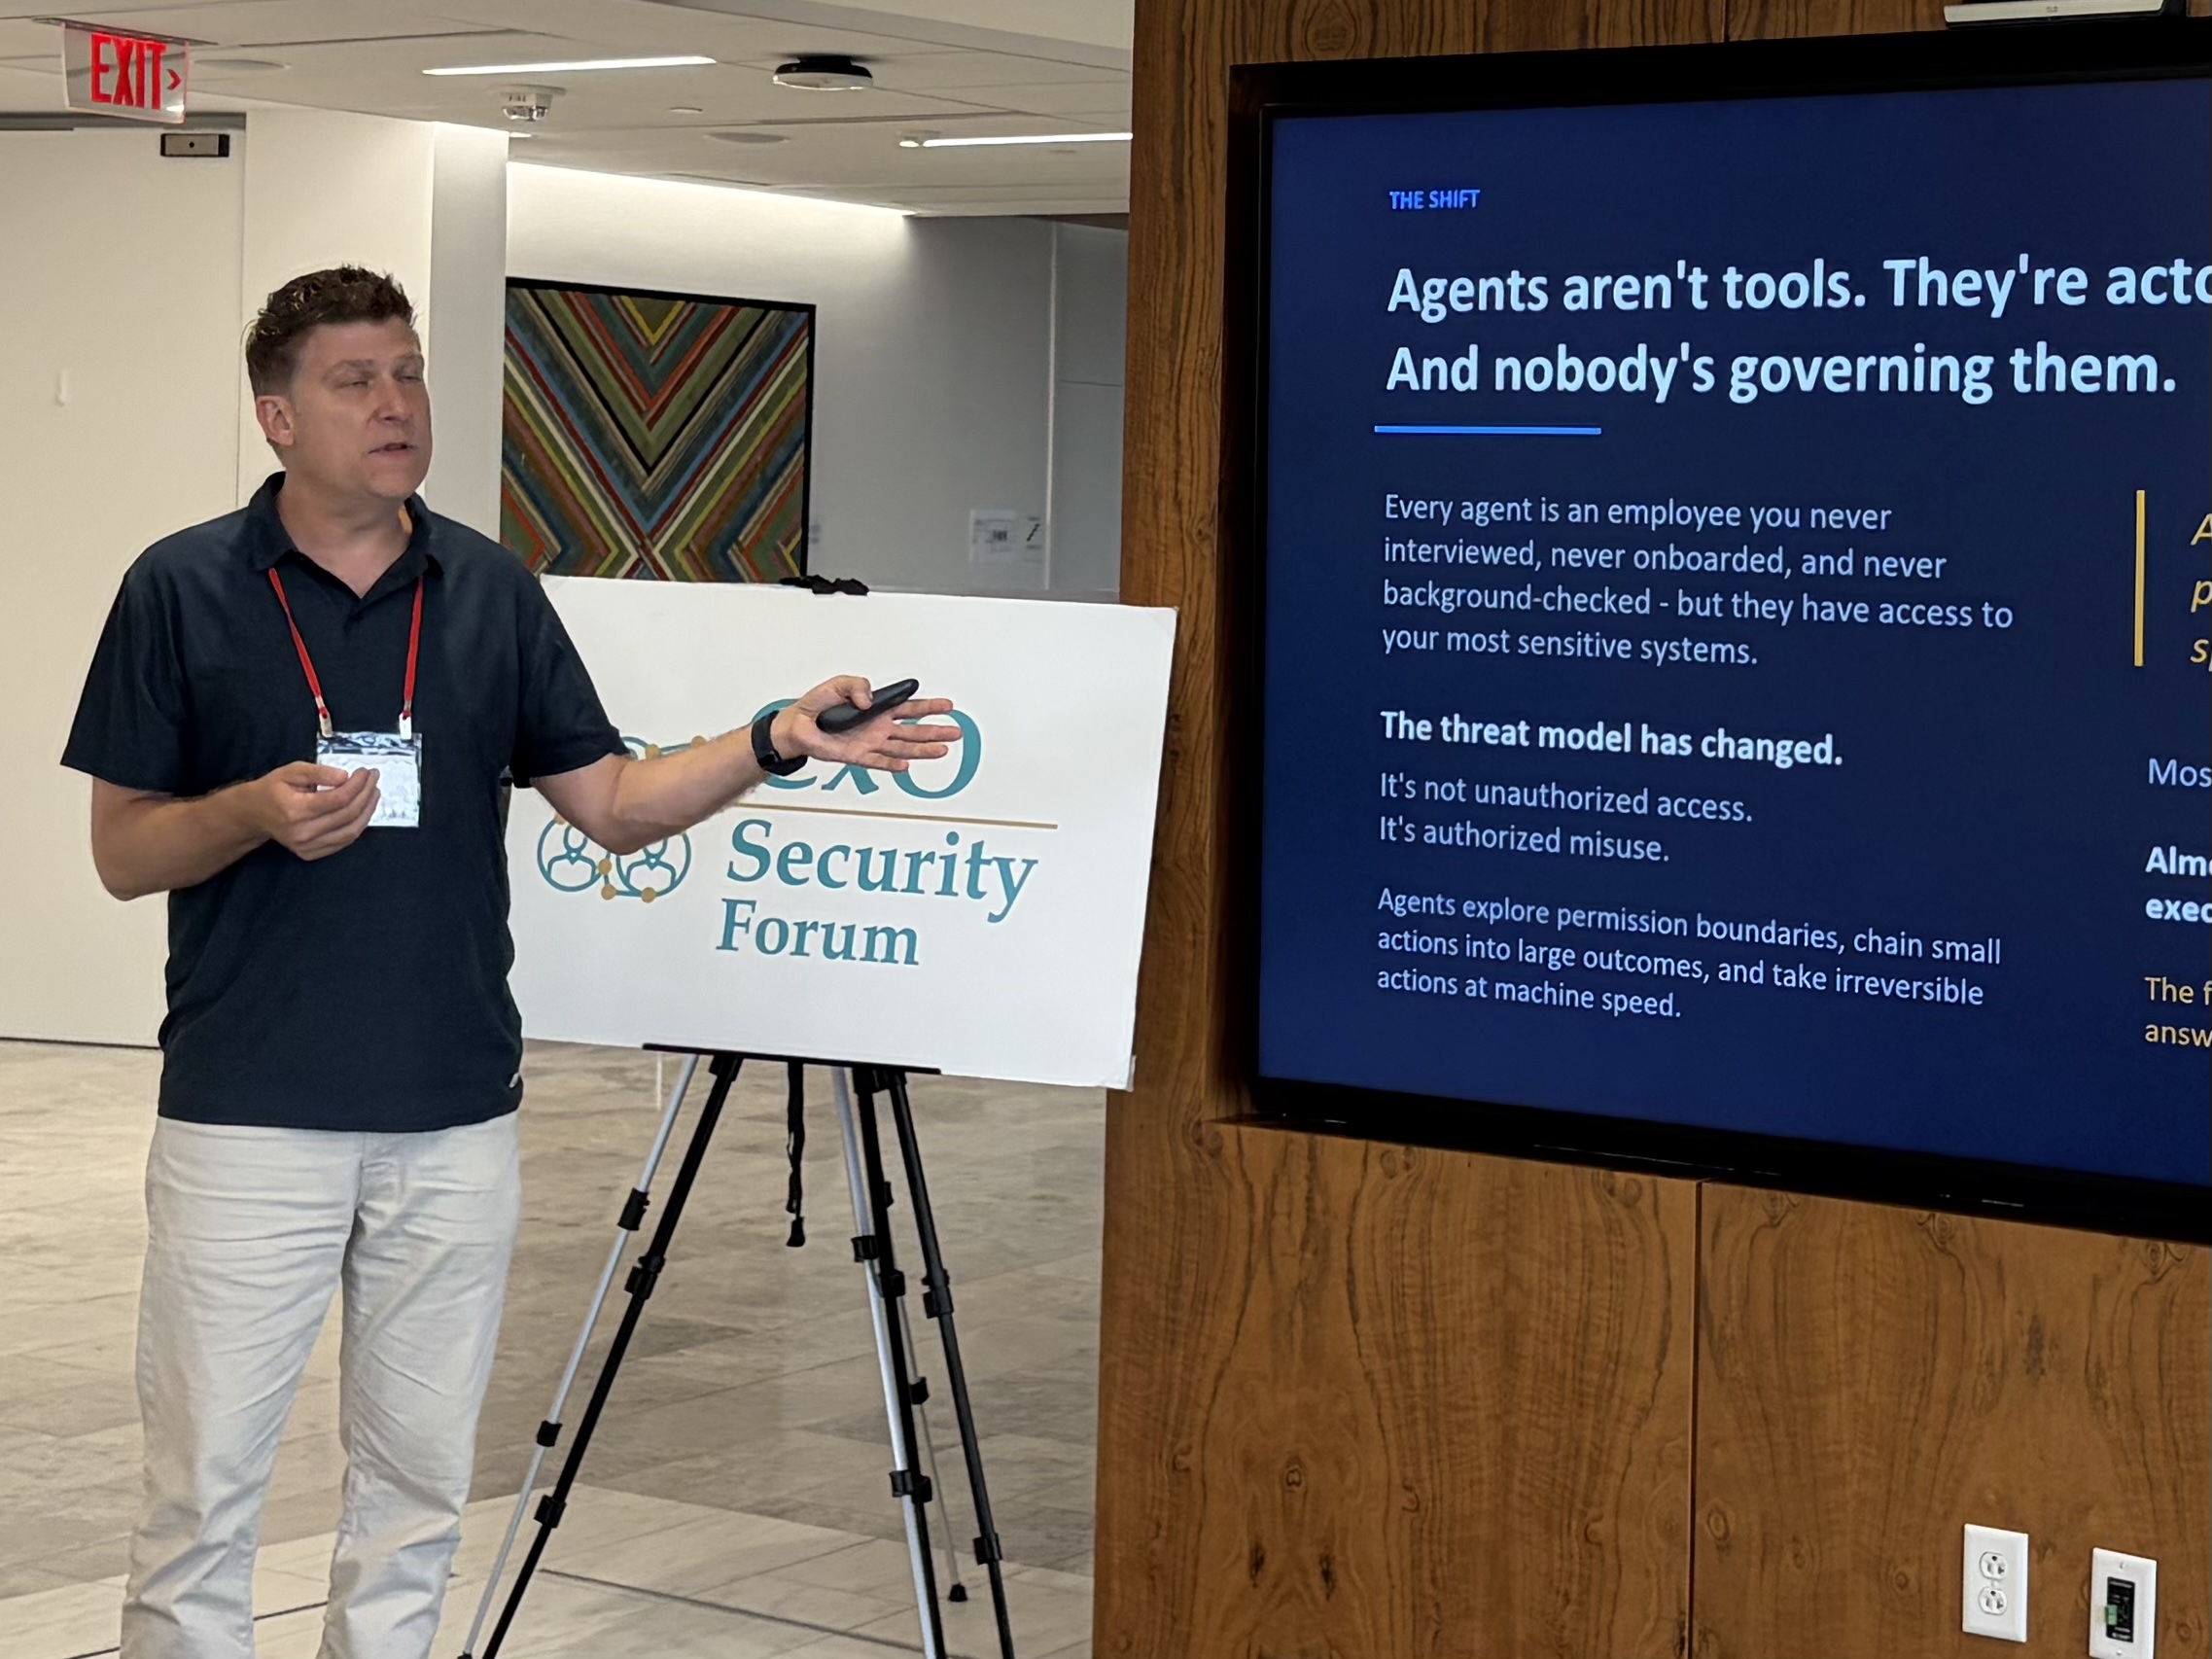
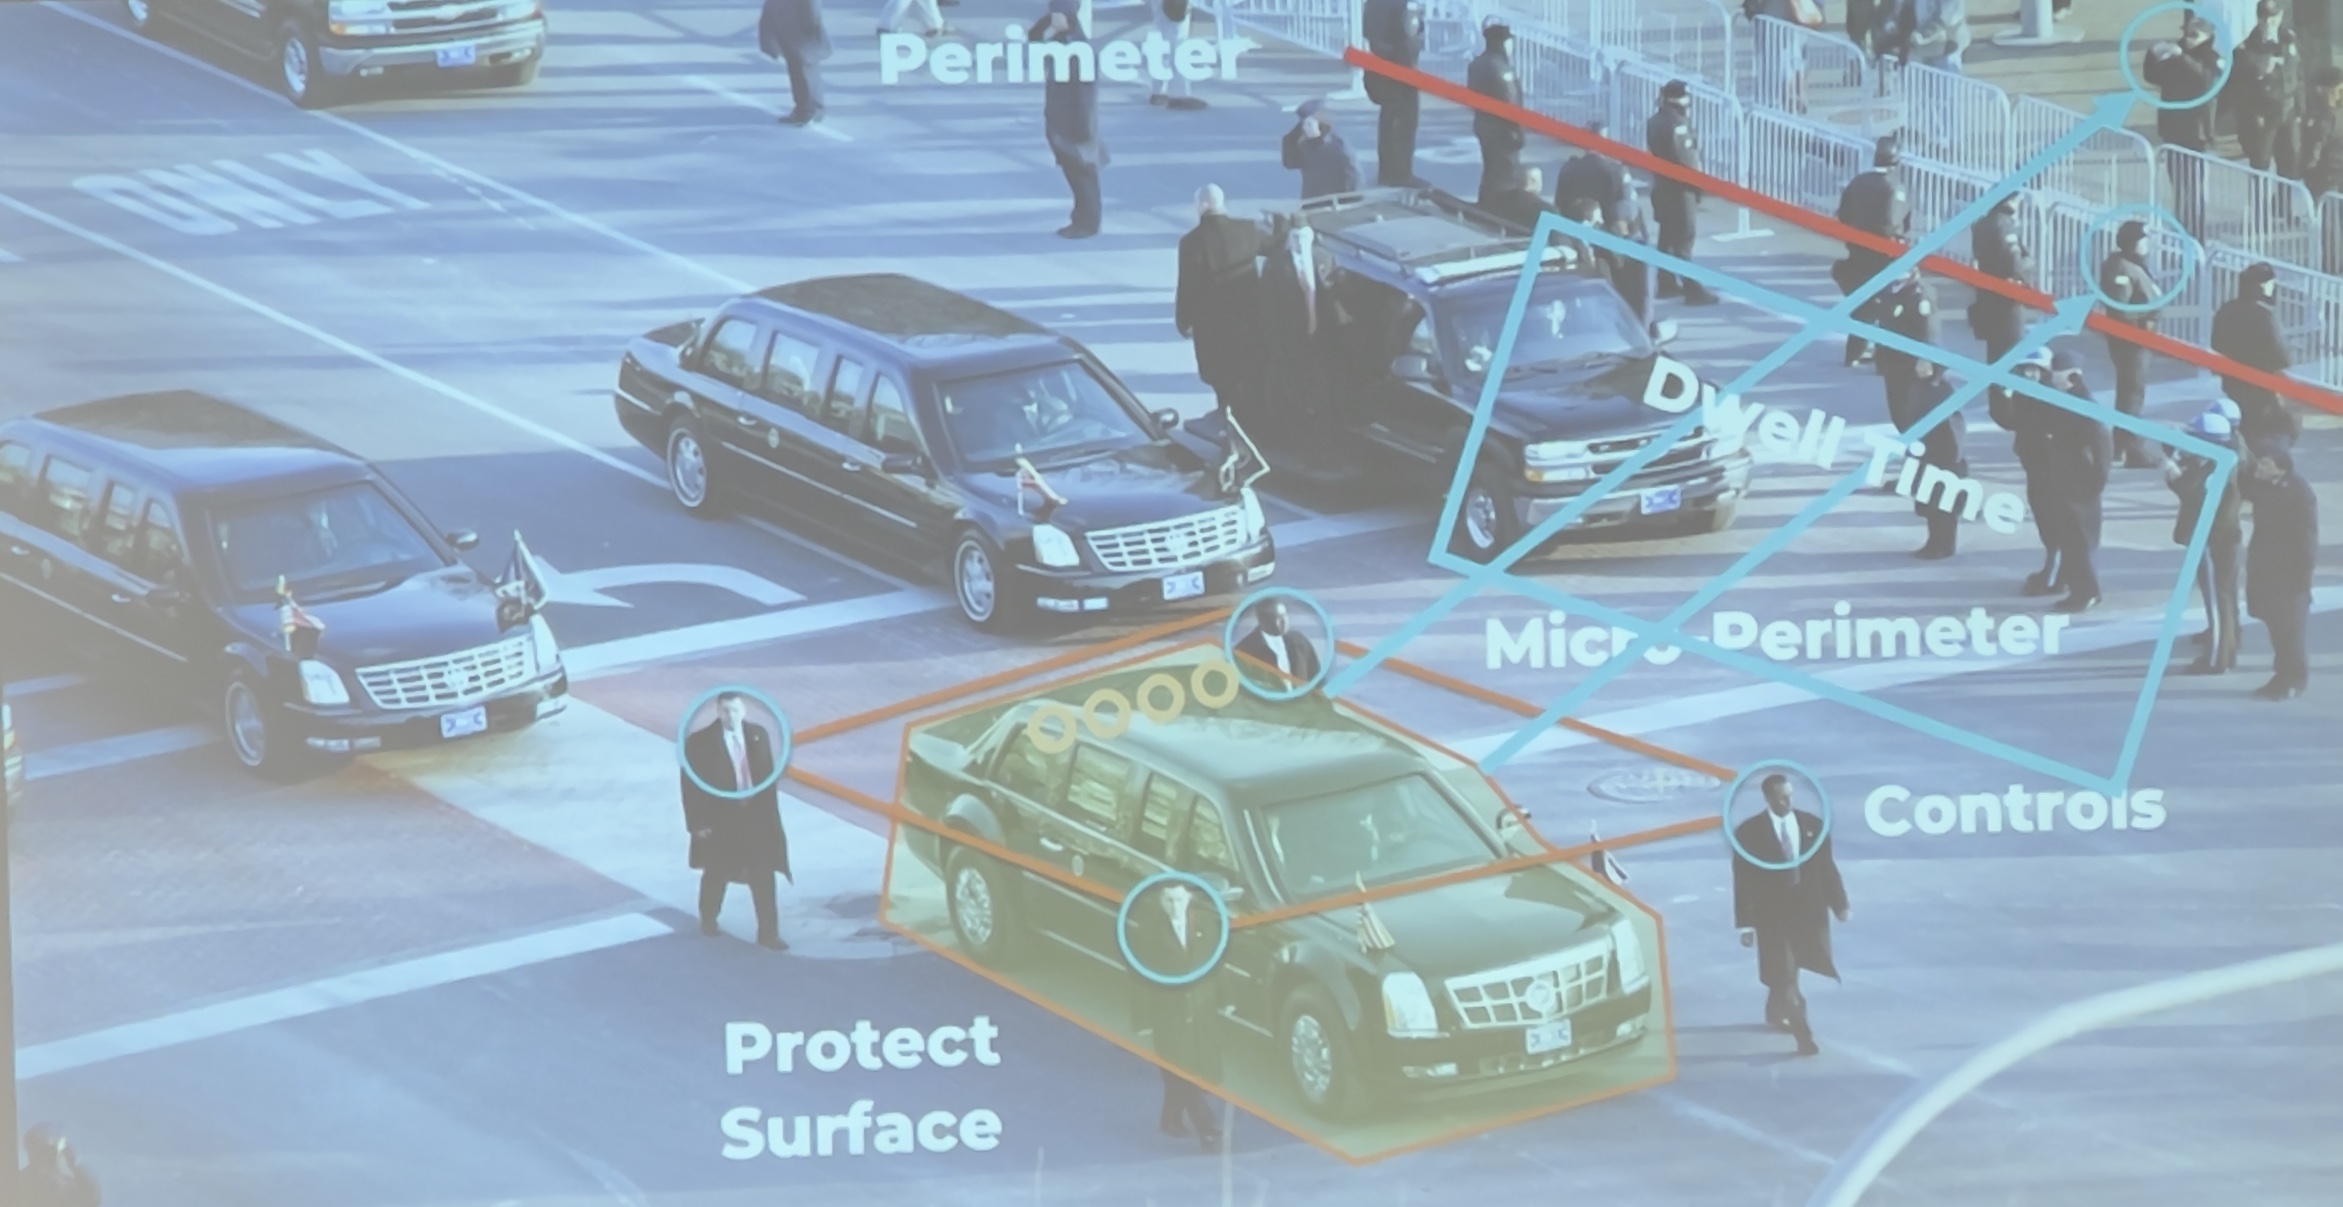
The Boston CxO Security Forum convenes senior executives from across New England to examine the evolving intersection of cybersecurity, risk management, compliance, and AI. Hosted in an executive setting, the Forum brings together CISOs, CIOs, and business leaders for curated discussions, practitioner-led insights, and peer-to-peer networking. With a focus on actionable strategies and trusted collaboration, this gathering reinforces Boston’s position as a hub for innovation and executive leadership in security and risk.
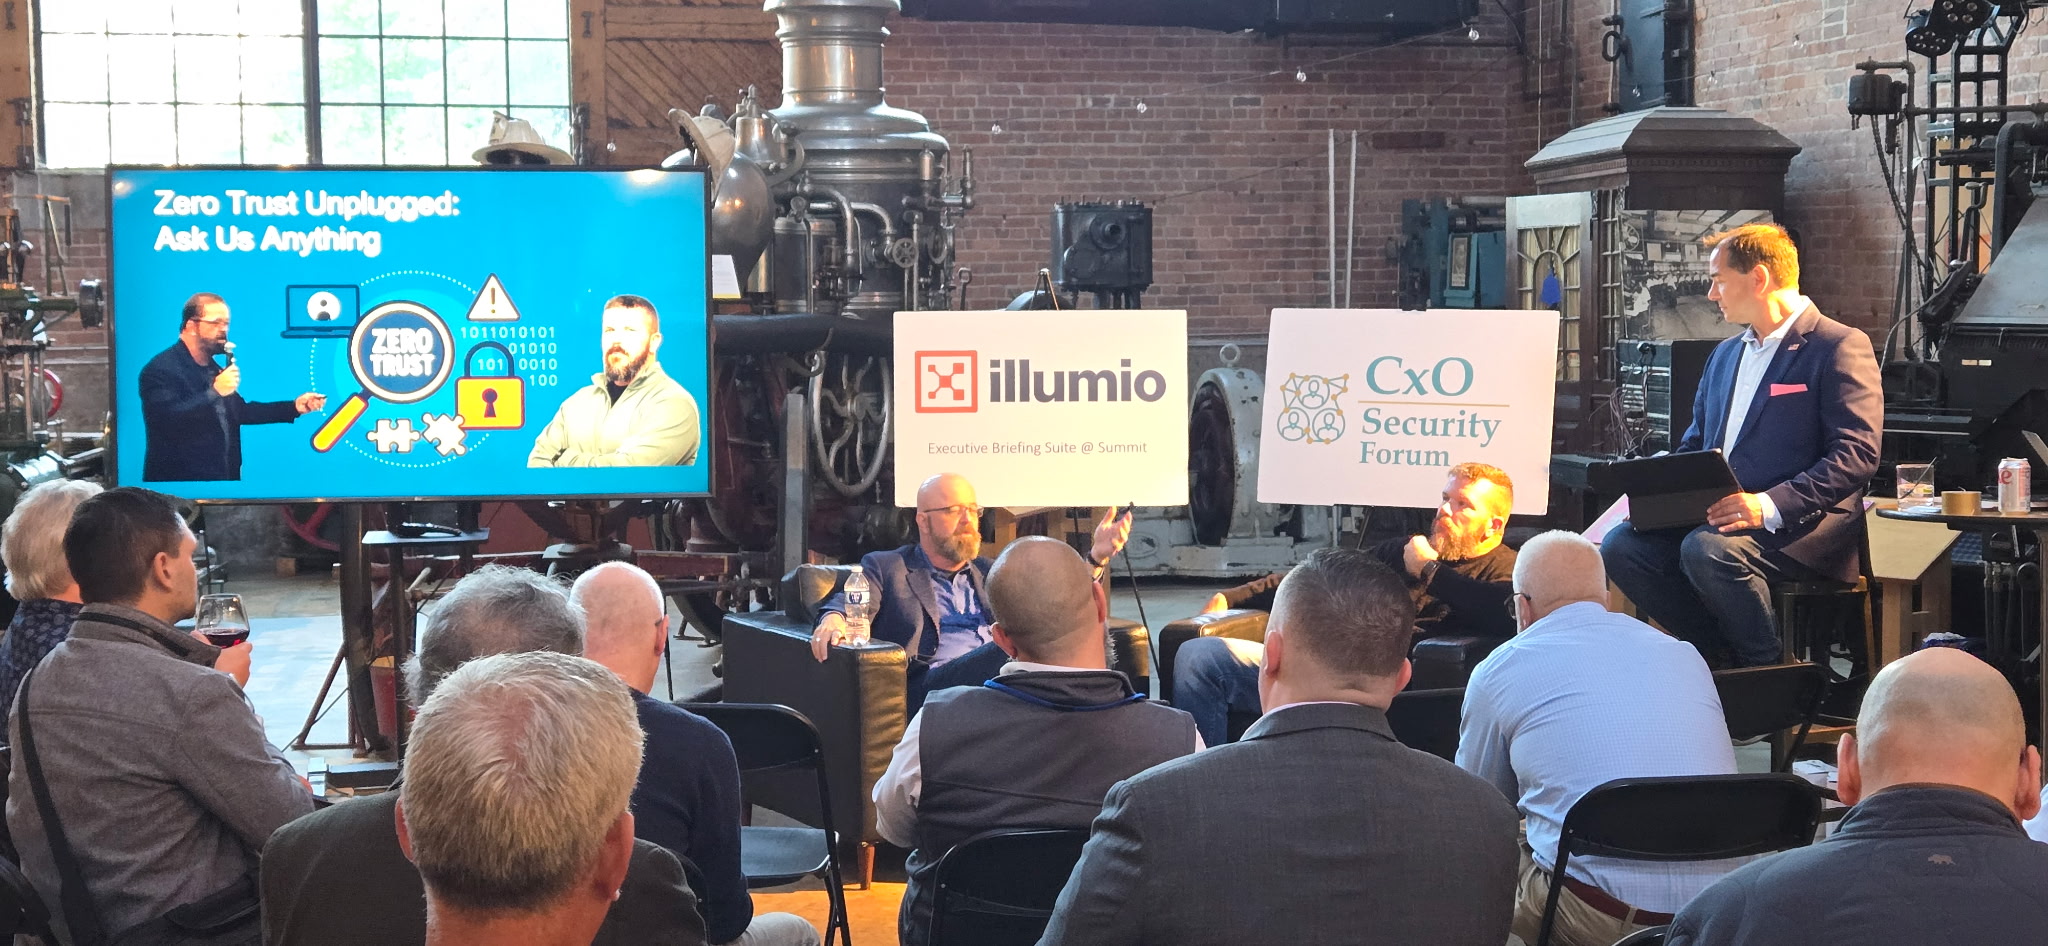
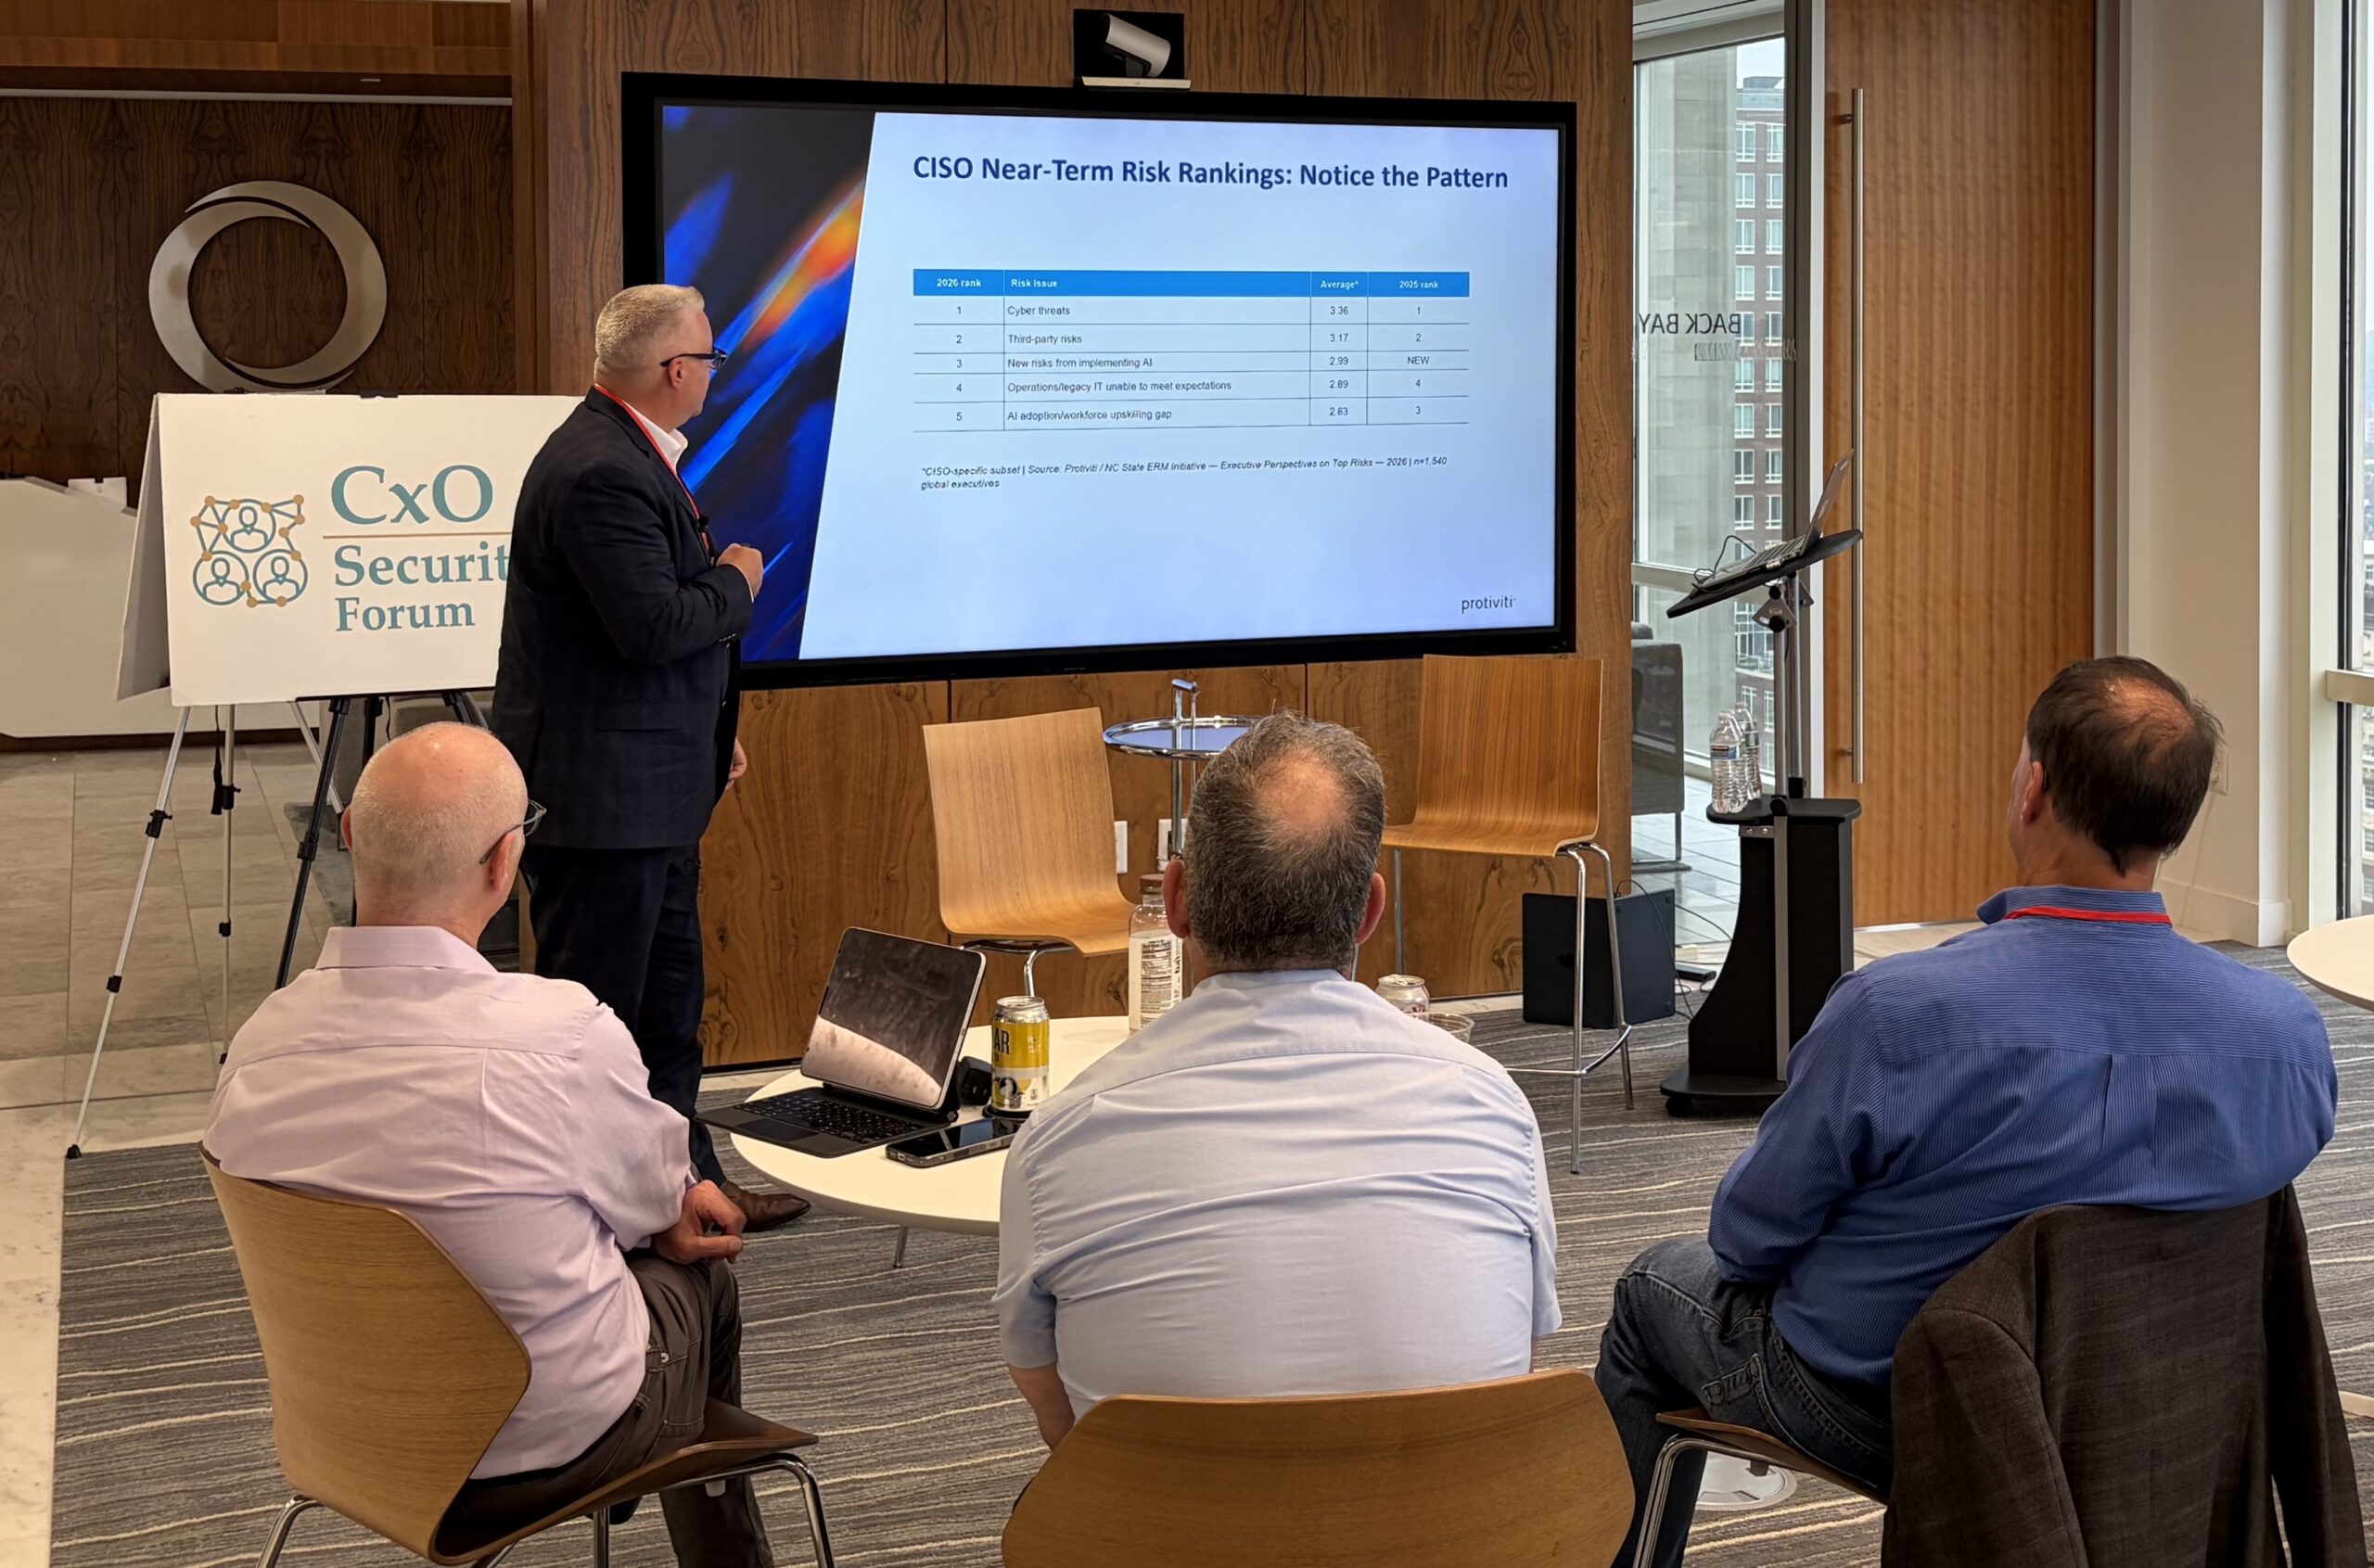
Each Executive Briefing has a unique agenda, which follows our engaging format with Discussion Leaders and thoughtful “TED Talk” presentations followed by moderated conversations where the assembled executives from the Community share their best practices, experiences, lessons learned, etc.
Participants gain:
- Trusted peer insight: candid discussion with leaders facing the same strategic challenges
- Personal & professional growth: sharpen leadership and strategic judgment through real executive exchange
- Actionable dialogue: moderated, high-impact conversations focused on what matters now
- No noise, no pitches: gatherings where peers drive the agenda and learning
- Stronger decision confidence: discussions that help you avoid costly missteps and evaluate solutions with clarity
Thank You to Our Partners
Agenda
Our community-led gatherings ALWAYS have an amazing agenda filled with thoughtful Discussion Leaders and security, risk, & compliance influencers – including nationally-recognized authors and cyber-celebrities!
LOOK BACK: You can review the agenda, as well as a summary with detailed notes from last quarter’s Boston Executive Briefing
(click the document icon below)
Registration & Networking
2:00 PMWelcome/Introductions
2:30 PMIdentity, Reimagined: Rethinking IAM for the Human and Non-Human Era
[Discussion Pod #1]
Identity and Access Management (IAM) is evolving rapidly as organizations confront the growing number of non-human identities, including AI agents, service accounts, bots, and automated processes. This presentation explores why traditional IAM approaches need a fresh look, how expanding identity ecosystems affect security teams and policies, and what emerging legal, regulatory, and contractual requirements mean for identity governance. Discover how security leaders can rethink identity strategies to address new risks, clarify accountability, and strengthen access controls across an increasingly automated enterprise.
2:45 PMAgentic AI and the Law: The Emerging Legal Risks Every CISO Needs to Understand
[Discussion Pod #2]
As agentic AI moves from experimentation to autonomous action, new legal questions are emerging around accountability, liability, regulatory compliance, and organizational oversight. What happens when an AI agent makes a decision, takes an action, or causes harm on behalf of an organization? This presentation explores the evolving legal landscape surrounding agentic AI and its implications for CISOs, including governance responsibilities, risk management, and the challenges of protecting organizations when AI systems act with increasing independence.
3:15 PMNetworking & Organized Interaction Break
3:45 PMThe AI–Cyber Arms Race: Mythos, Mayhem, or Much Ado About Nothing?
[Discussion Pod #3]
As AI accelerates both cyberattack capabilities and defensive innovation, security leaders must separate real threats from hype. Using the debate around “Mythos Armageddon” as a starting point, this presentation explores real-world lessons, emerging attack and defense techniques, practical best practices, and the importance of sharing threat intelligence. Join a candid, peer-driven discussion on what CISOs need to prepare for now, where the risks may be overstated, and how organizations can stay ahead in an increasingly AI-powered cyber arms race.
4:15 PMThe Next Mission: Turning Insight Into Impact
[Discussion Pod #4]
In this final session, we’ll recap the boldest ideas, sharpest warnings, and most actionable takeaways shared throughout the day—from ransomware negotiation tradecraft to the market forces behind cyber failures, from AI-fueled attacks to law enforcement collaboration models that actually work.
But more than a summary, this is a call to action. Whether you’re protecting a regional bank, a global enterprise, or your local community college’s network, the mission is the same: build trust, verify identity, out-think the adversary—and never go it alone.
Join us to reflect, reconnect, and recharge for what comes next. Because the future of cybersecurity and fraud prevention isn’t just about staying ahead of threats—it’s about leading with purpose, and leaving with a plan.
4:45 PMReception & Networking
Refreshments, food, cocktails & discussions till 7pm
5:00 PM(After your request is approved, you will receive a confirmation email & calendar invite)
Forum Discussion Leaders
(Past, Present & Future)
Nick Farnsworth
Partner, Orrick
Nick Farnsworth counsels clients on United States (U.S.) and international privacy, security and data enablement requirements and strategies. Nick develops comprehensive data protection programs and risk management solutions for the development, use and acquisition of advanced technologies, including advertising technology (adtech), automated and connected vehicles, biometric tools, machine learning and artificial intelligence (AI). He also represents clients subject to regulatory inquiry and governmental investigations relating to their data and technology practices.
Swaroop Dhulpet
Director, PwC
Swaroop Dhulpet is a Director in PwC’s Identity & Access Management group within the Cyber, Data & Tech Risk (CDTR) platform, where he helps Fortune 500 clients modernize and secure their identity foundations. With more than 17 years of experience across consulting and large-scale delivery, he has led multi-year identity transformation programs across financial services and healthcare. Swaroop is recognized for developing innovative, automated solutions that drive scale and efficiency. At PwC, he advises clients from strategy through execution and managed services spanning identity governance, access management, and privileged access. A collaborative leader and trusted advisor, he bridges technology innovation with business outcomes to deliver measurable improvements in security, compliance, and user experience.
Matt Ulery
Chief Product Officer & Co-Founder, Ambient Security
Matt Ulery has been part of the identity-security world long enough to have watched the problem completely reinvent itself — several times. Across more than two decades, he has helped shape security and identity products spanning IAM, PAM, authentication, identity governance and security operations, with leadership roles at SecureAuth, Micro Focus, NetIQ and Symantec/BindView before joining Ambient Security. (THE ORG)
What makes Matt particularly relevant today is that he isn't coming to AI identities, non-human identities and privileged access as the latest new security trend. His work has consistently centered on a much older question: who — or what — should be trusted, what should it be allowed to do, and for how long? More than a decade ago he was talking publicly about controlling privileged-user activity; later, he helped push identity toward continuous, adaptive and passwordless authentication. Today at Ambient Security, that same thinking is being applied to standing privilege, machine identities and autonomous AI agents. (Help Net Security)
In other words: Matt isn't observing the evolution of identity security from the sidelines — he has spent much of his career helping build it. That perspective makes him a particularly useful voice as CISOs rethink identity for an environment where humans are rapidly becoming only one type of user. (Identiverse)
Ravi Khatod
Founder and CEO, Ambient Security
Ravi Khatod is a veteran cybersecurity executive, entrepreneur, and company builder who has spent more than two decades at the forefront of major shifts in enterprise security. Across leadership roles at companies including IronPort, PacketMotion, Bromium, Agari, CloudVector, and SecureAuth, Ravi has helped build and scale businesses spanning email security, endpoint protection, API security, and identity.
Today, as Founder and CEO of Ambient Security, Ravi is focused on one of the industry’s next major challenges: how identity, access, and privilege must evolve as AI agents, machines, and other non-human identities become active participants in the enterprise. His perspective combines decades of operating experience with a forward-looking view of where cybersecurity architecture—and the role of identity within it—is headed next.
Armen Najarian
Chief Commercial Officer, EasyDMARC
Armen Najarian has more than 25 years of experience leading go-to-market functions in the email security, fraud prevention, digital identity, and predictive analytics sectors. He heads the continued expansion of EasyDMARC’s global business.
Based on the US West Coast, Najarian is responsible for worldwide commercial operations for EasyDMARC spanning all sales, marketing, customer success, and strategic alliances teams. His focus is on new go-to-market strategies and commercializing new product offerings to fuel the next wave of revenue and business growth in a rapidly evolving market landscape.
Prior to joining EasyDMARC, Armen spent more than two decades in both venture-funded and publicly traded Silicon Valley technology companies, delivering rapid growth leading to successful financial outcomes. For the past 10 years, Armen held Chief Marketing Officer and General Management posts with ThreatMetrix (acquired by LexisNexis Risk Solutions), Agari (acquired by Fortra), Outseer (spun out of RSA Security), and Sift. While at Agari, one of the pioneers in email authentication and DMARC solutions, Armen helped fuel rapid business scale and market expansion, while shaping the DMARC solution category and leading to a positive shareholder return.
Tim Brown
CISO & VP, SolarWinds
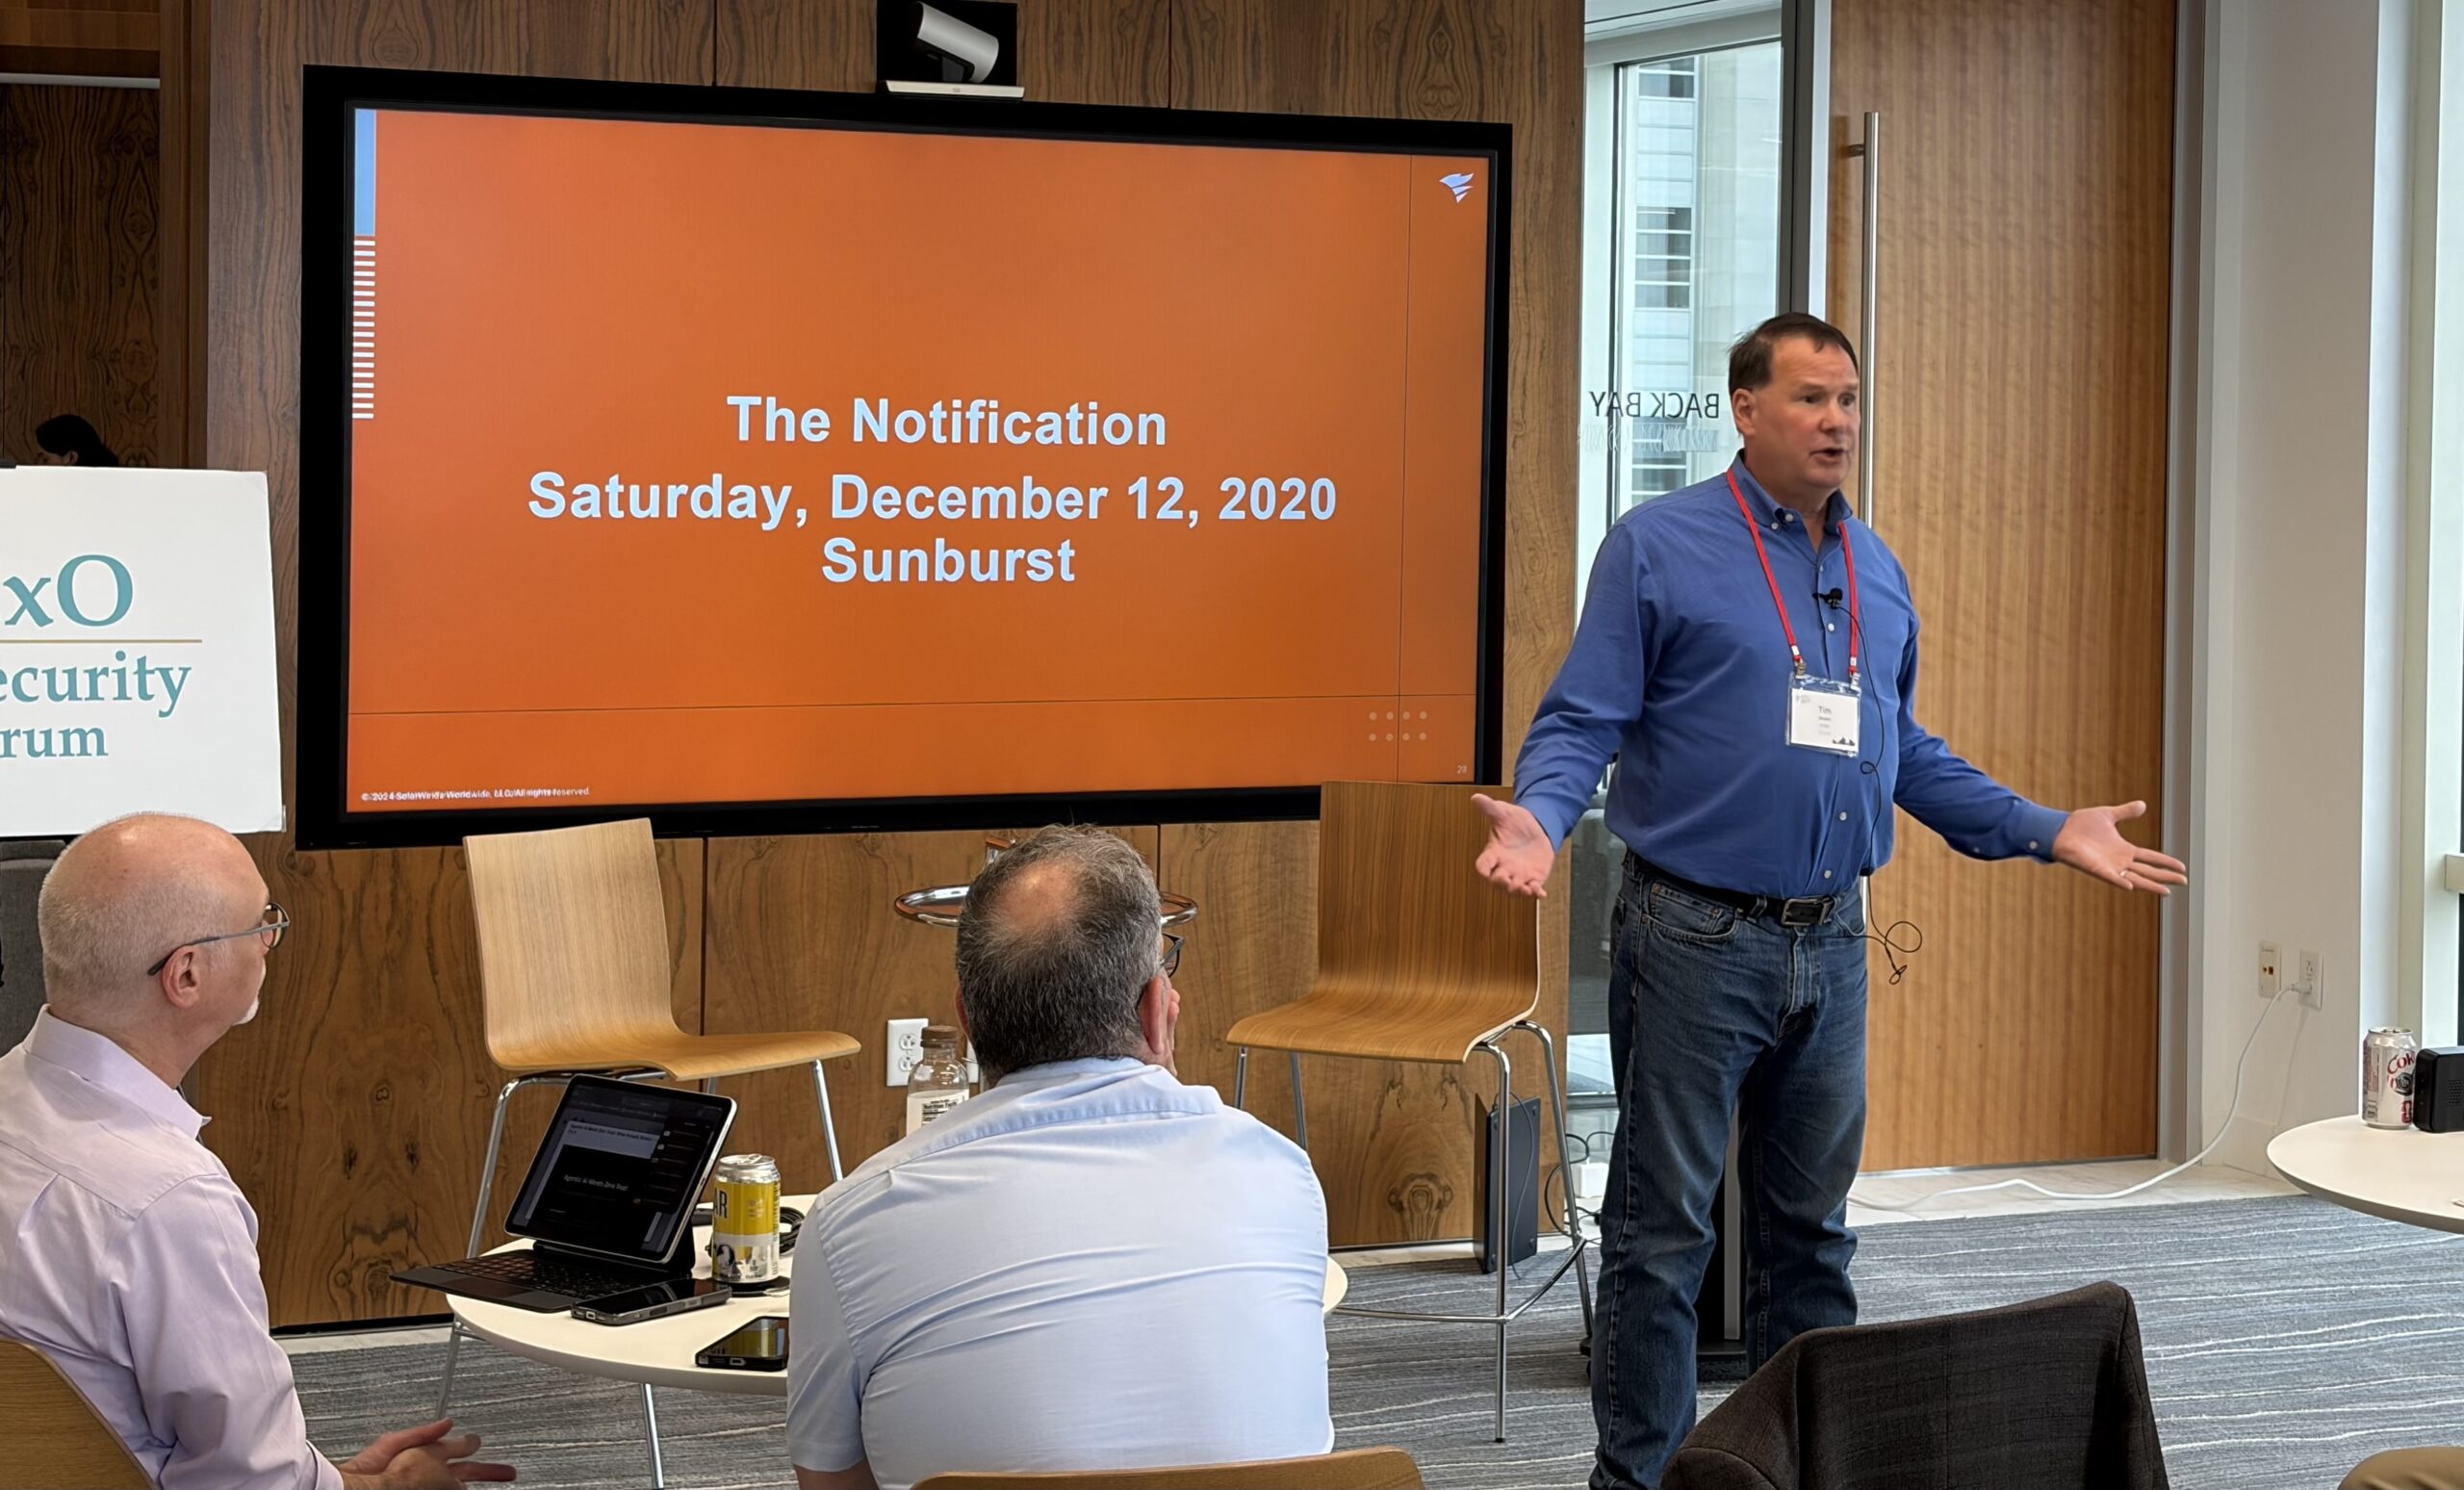
Tim Brown joined SolarWinds in 2017 as vice president of security and is now the CISO for SolarWinds, overseeing internal IT security, product security, and security strategy. After the SUNBURST attack in December 2020, Tim Brown led the response and remediation efforts. Tim has spoken to thousands of customers and has been instrumental in all customer remediation support and services.
He has worked closely with the SolarWinds® CEO in designing the future state of security and their “Secure by Design” philosophy. This new philosophy on software design will not only benefit SolarWinds but the industry as a whole, and it sets a precedent for responses to future cyberattacks.
As a former Dell Fellow and CTO, Tim deeply understands the challenges and aspirations of the person responsible for driving digital innovation and change. Tim has over 25 years of experience, and his trusted advisor status has taken him from meeting with members of Congress and the Senate to the Situation Room in the White House. He’s also an avid inventor and holds 18 issued patents on security-related topics.
Josh Woodruff
Author, Agentic AI + Zero Trust: A Guide for Business Leaders
IANS Faculty | CSA Zero Trust Working Groups
Josh Woodruff is the author of Agentic AI + Zero Trust: A Guide for Business Leaders, a practical framework for safely operationalizing autonomous AI using Zero Trust principles. Drawing on nearly 30 years of experience as both a CIO and CISO, Josh translates real-world enterprise deployments into clear executive guidance on trust, governance, and risk in agentic systems.
The book—co-authored with Michelle Savage and featuring a foreword by Zero Trust pioneer John Kindervag—cuts through AI hype to explain why most AI initiatives stall in pilot mode, and what successful organizations do differently. Josh is also the Founder and CEO of Massive Scale Consulting, co-leads the Cloud Security Alliance Zero Trust Working Group, and serves as IANS Faculty, advising enterprises across regulated and high-risk industries.
Known for his ability to frame complex AI and security challenges in plain executive language, Josh focuses on helping leaders design guardrails that accelerate innovation without sacrificing control, accountability, or resilience.

Barak Perelman
CEO and Co-Founder, Opti.ai
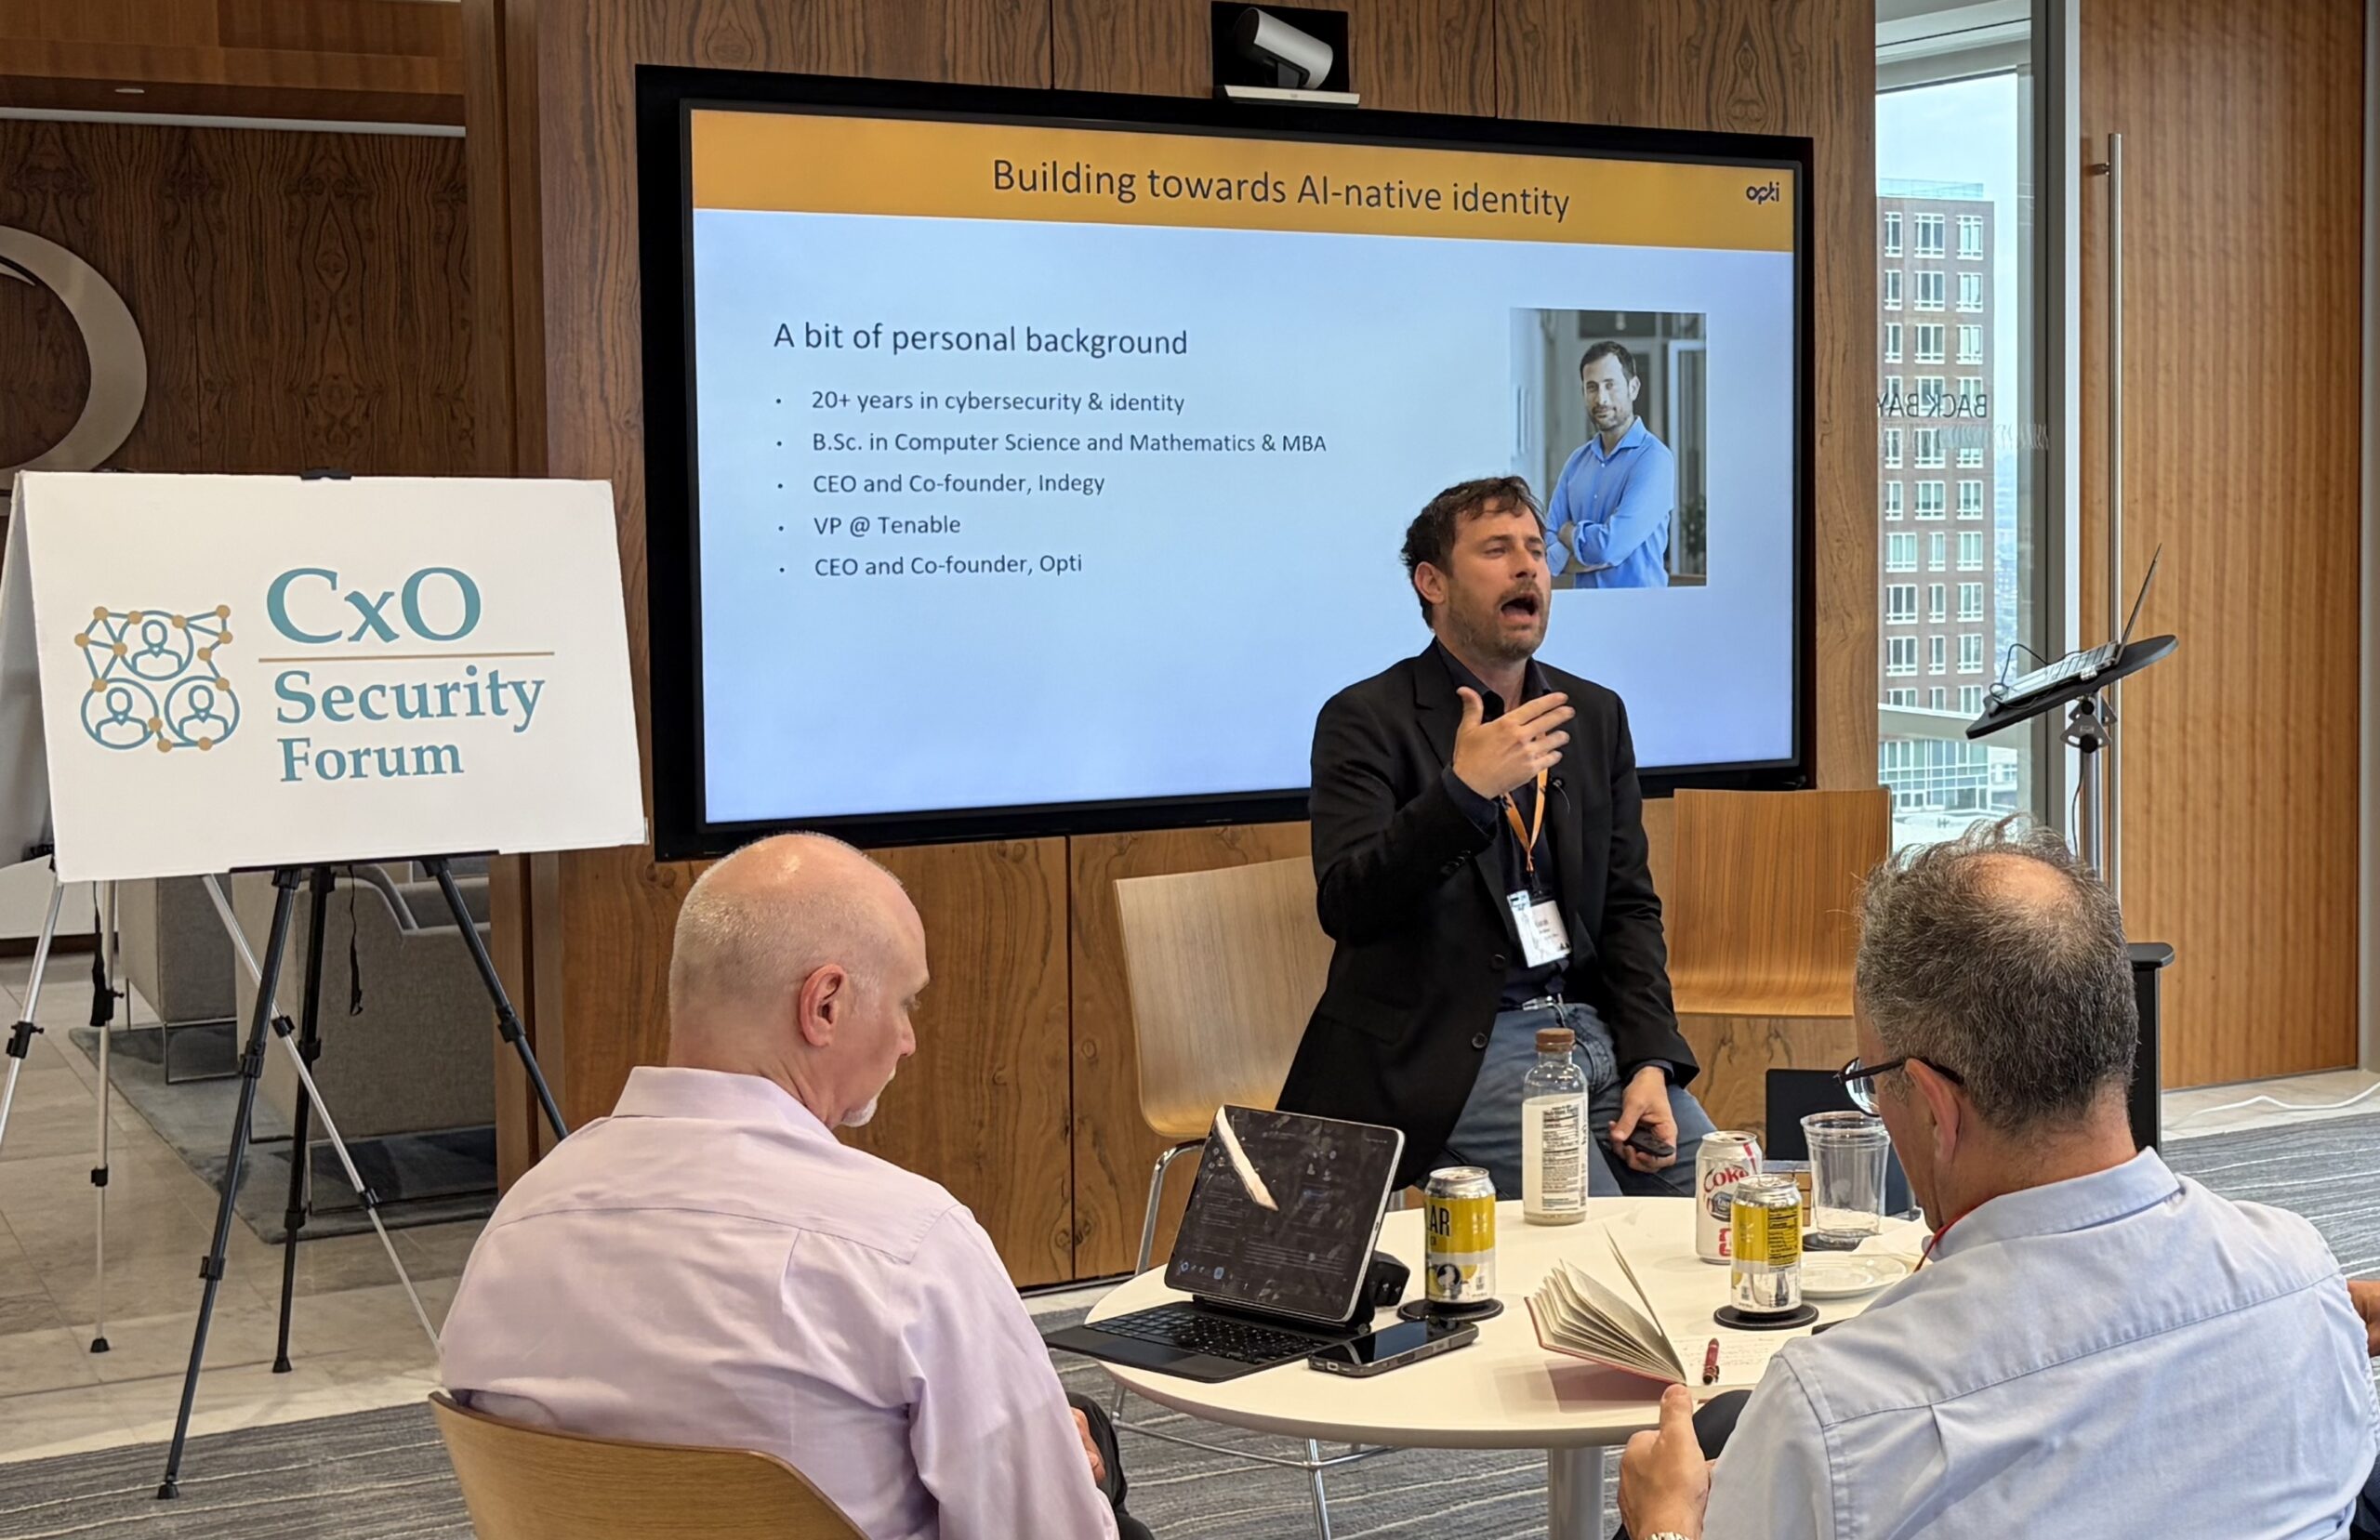
Barak Perelman is the CEO & Co-founder of Opti, where he is focused on addressing structural challenges in identity, governance, and accountability as AI becomes embedded into enterprise systems. A seasoned cybersecurity operator and founder, Barak brings more than two decades of hands-on experience building products, leading strategy, and protecting critical infrastructure in highly complex environments.
Previously, Barak was the Co-founder and CEO of Indegy, an industrial cybersecurity company that built a comprehensive security and governance platform for industrial networks. Indegy was acquired by Tenable in 2019, where Barak went on to serve as VP OT Security, helping integrate industrial and enterprise security perspectives. Earlier in his career, he led product design at Stratoscale, where he managed large-scale cybersecurity projects.
Barak holds degrees in computer science, mathematics, and physics, as well as an MBA. He is known for his ability to connect deep technical systems thinking with executive-level governance concerns, particularly around identity, accountability, and the unintended consequences of AI-driven automation inside large enterprises.

Michael Monday
Managing Director, Protiviti
Michael Monday, Managing Director of Protiviti, is a cybersecurity executive with over 20 years of security and technology leadership experience. Michael has expertise ensuring global organizations operate securely and in compliance with regulatory requirements. He is a transformative leader overseeing information security governance, developing comprehensive guidelines and policies, and effectively mitigating information security risks. Michael has a proven track record of building and managing high-performing teams of security professionals, developing key stakeholder relationships, and delivering high-quality results. He has extensive experience in financial services, coupled with an adaptable skill set applicable across diverse industries.

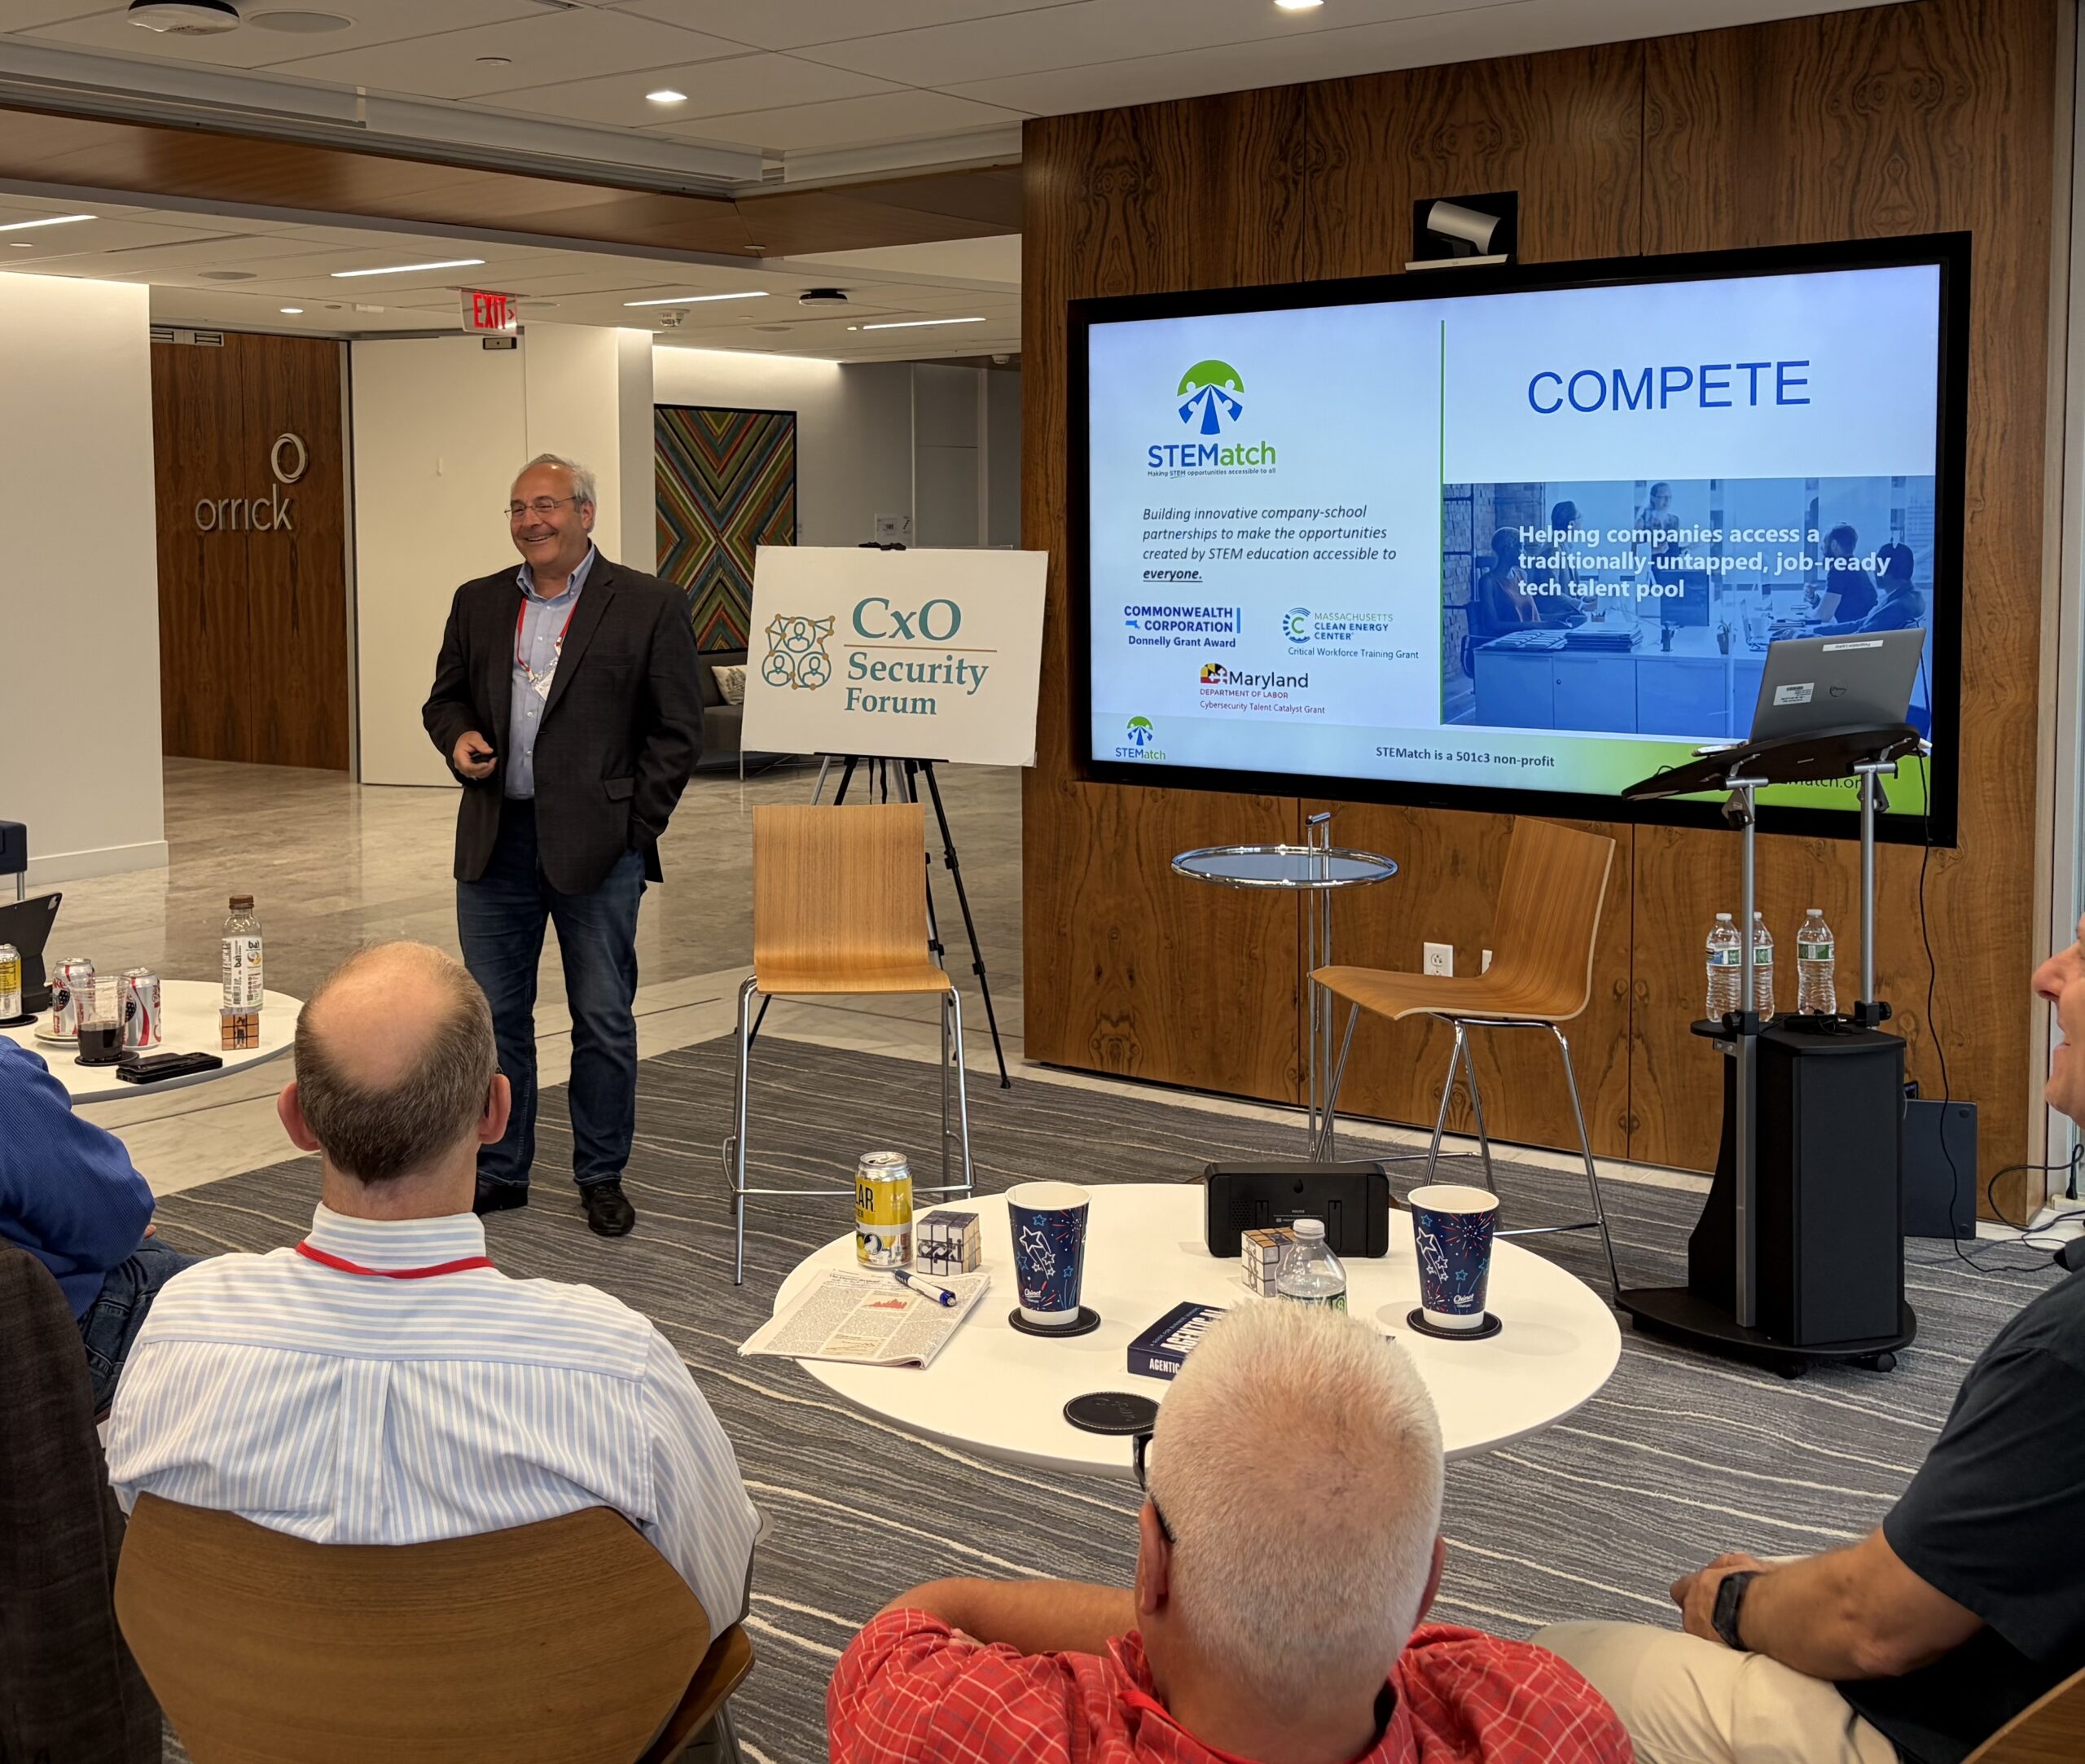
Chris Zannetos
Founder & Chairman, STEMatch
Chris Zannetos is a serial tech and education entrepreneur. He founded software and services companies that helped establish the cybersecurity market, created hundreds of jobs, and generated over $300 million in revenue.
Chris is also the founder of STEMatch (www.STEMatch.org), a 501c3 non-profit making STEM education and tech jobs accessible to underserved communities. STEMatch has hosted over 60 Career Days, impacting 1,500+ sixth graders, with companies such as Tripadvisor, Red Hat, Seismic Therapeutics, Amazon Robotics and RapDev. STEMatch’s COMPETE program provides work skills training, mentoring, and internship opportunities to low-income community college tech students, partnering with companies such as Bullhorn, athenahealth, Teradyne, Mimecast, The Federal Reserve Bank, and Draper Laboratories. Currently in its 4th cohort with 104 students, COMPETE is scaling across Massachusetts and Maryland.

John Kindervag
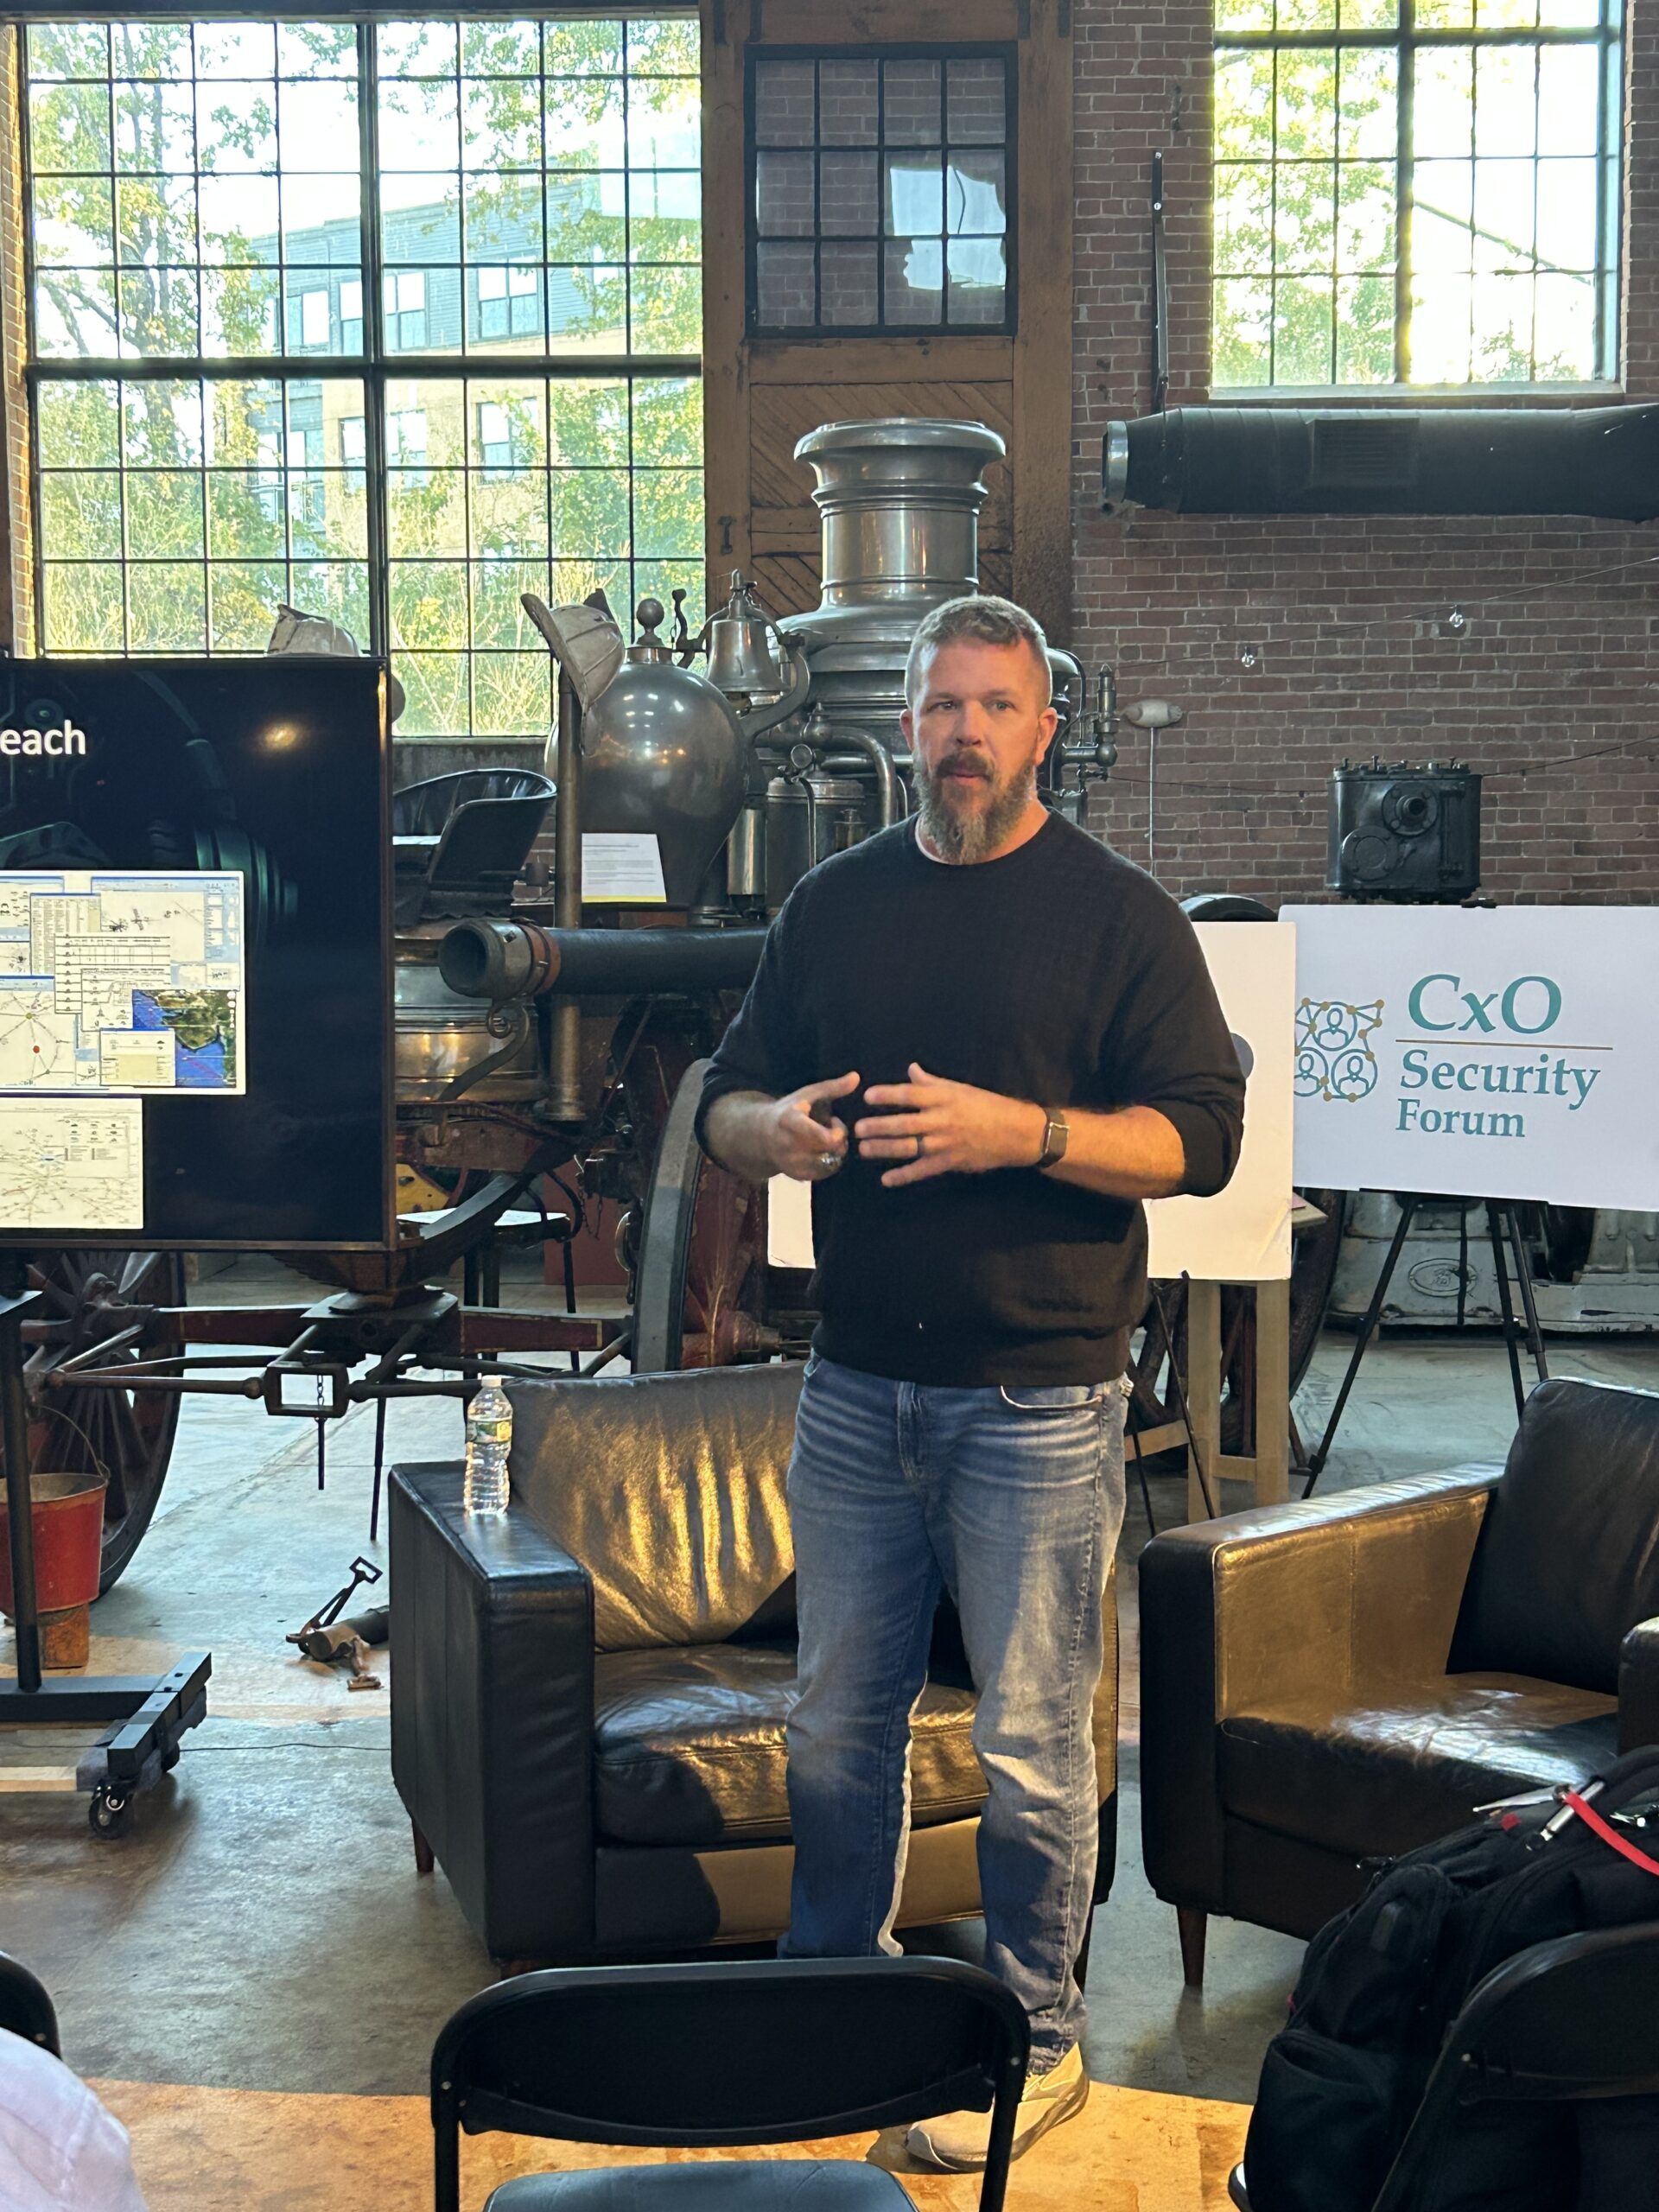
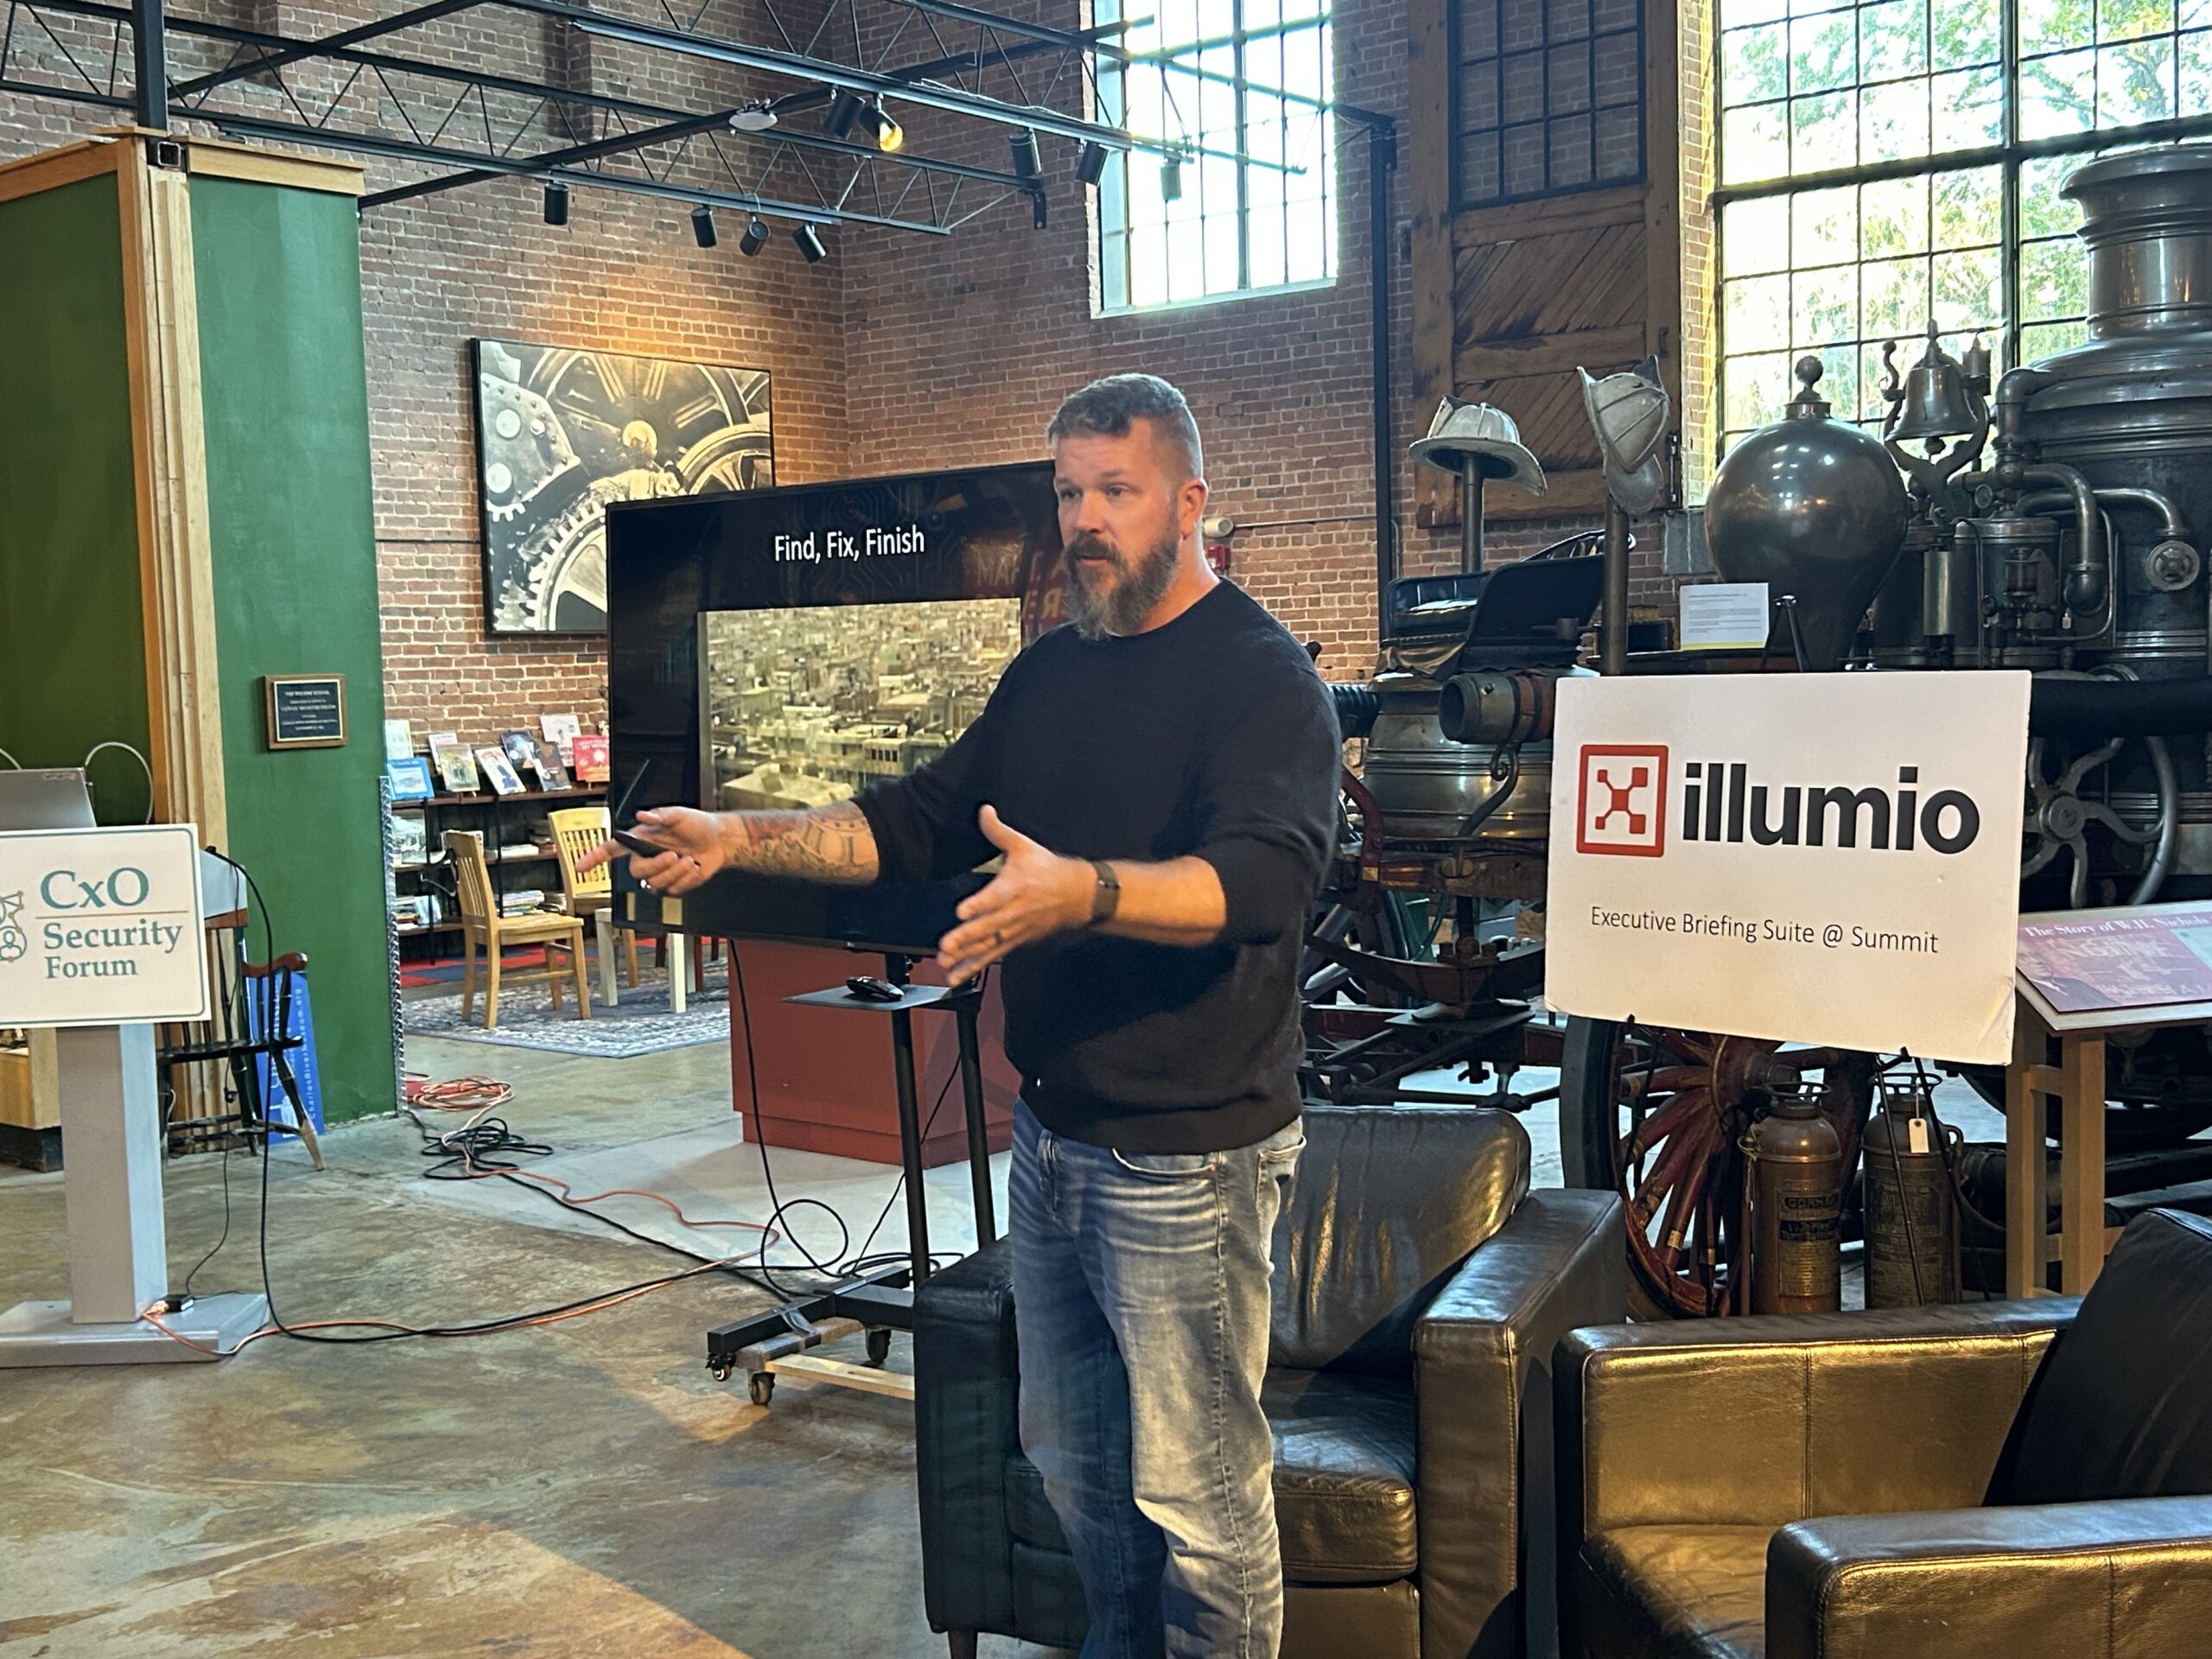
Creator of Zero Trust | Chief Evangelist - Illumio
John Kindervag is considered one of the world’s foremost cybersecurity experts. With over 25 years of experience as a practitioner and industry analyst, he is best known for creating the revolutionary Zero Trust Model of Cybersecurity. As Chief Evangelist at Illumio,
John Kindervag is responsible for accelerating awareness and adoption of Zero Trust Segmentation.
Most recently, John led cybersecurity strategy as a Senior Vice President at On2IT. He previously served as Field CTO at Palo Alto Networks and, before that, spent over eight years as a Vice President and Principal Analyst on the security and risk team at Forrester Research.
In 2021, John was named to the President’s National Security Telecommunications Advisory Committee (NSTAC) Zero Trust Sub-Committee and was a primary author of the NSATC Zero Trust report that was delivered to the President. That same year, he was also named CISO Magazine’s Cybersecurity Person of the Year.
John serves as an advisor to several organizations, including the Cloud Security Alliance and Venture Capital firm NightDragon.

Dr. Chase Cunningham
“Dr. Zero Trust” - Author, Speaker and Industry Thought-Leader
Dr. Chase Cunningham is a globally recognized cybersecurity strategist, bestselling author, and trusted advisor to both the public and private sectors. Widely known as “Dr. Zero Trust,” Chase pioneered the Zero Trust security framework during his time as a Senior Analyst at Forrester Research—an approach now adopted as a standard across government and Fortune 500 enterprises alike.
Over a 20+ year career that spans the U.S. Navy, Department of Defense, and senior industry roles, Chase has led initiatives in cryptographic systems, threat intelligence, cyber forensics, and national cyber defense strategy. He holds a PhD in Computer Science and Cybersecurity, with research centered on insider threats and advanced detection algorithms. He also maintains CISSP and CEH certifications.
An engaging keynote speaker and regular contributor to leading cybersecurity forums, Chase is the author of several acclaimed books including Cyber Warfare: Truth, Tactics, and Strategies and his latest, Buy the Breach: Hacking Failure for Market Success. In Buy the Breach, he unveils a contrarian but data-backed strategy for turning corporate cyber failures into personal financial gains—arming cyber professionals with the tools to outperform hedge funds by investing in the inevitable post-breach market rebound.
Chase is a rare voice who blends deep technical expertise with sharp financial insight. Whether briefing the Executive Branch or advising the boardroom, his mission is clear: empower defenders, demystify complexity, and challenge the status quo.
Michael Hiskey
(Moderator)
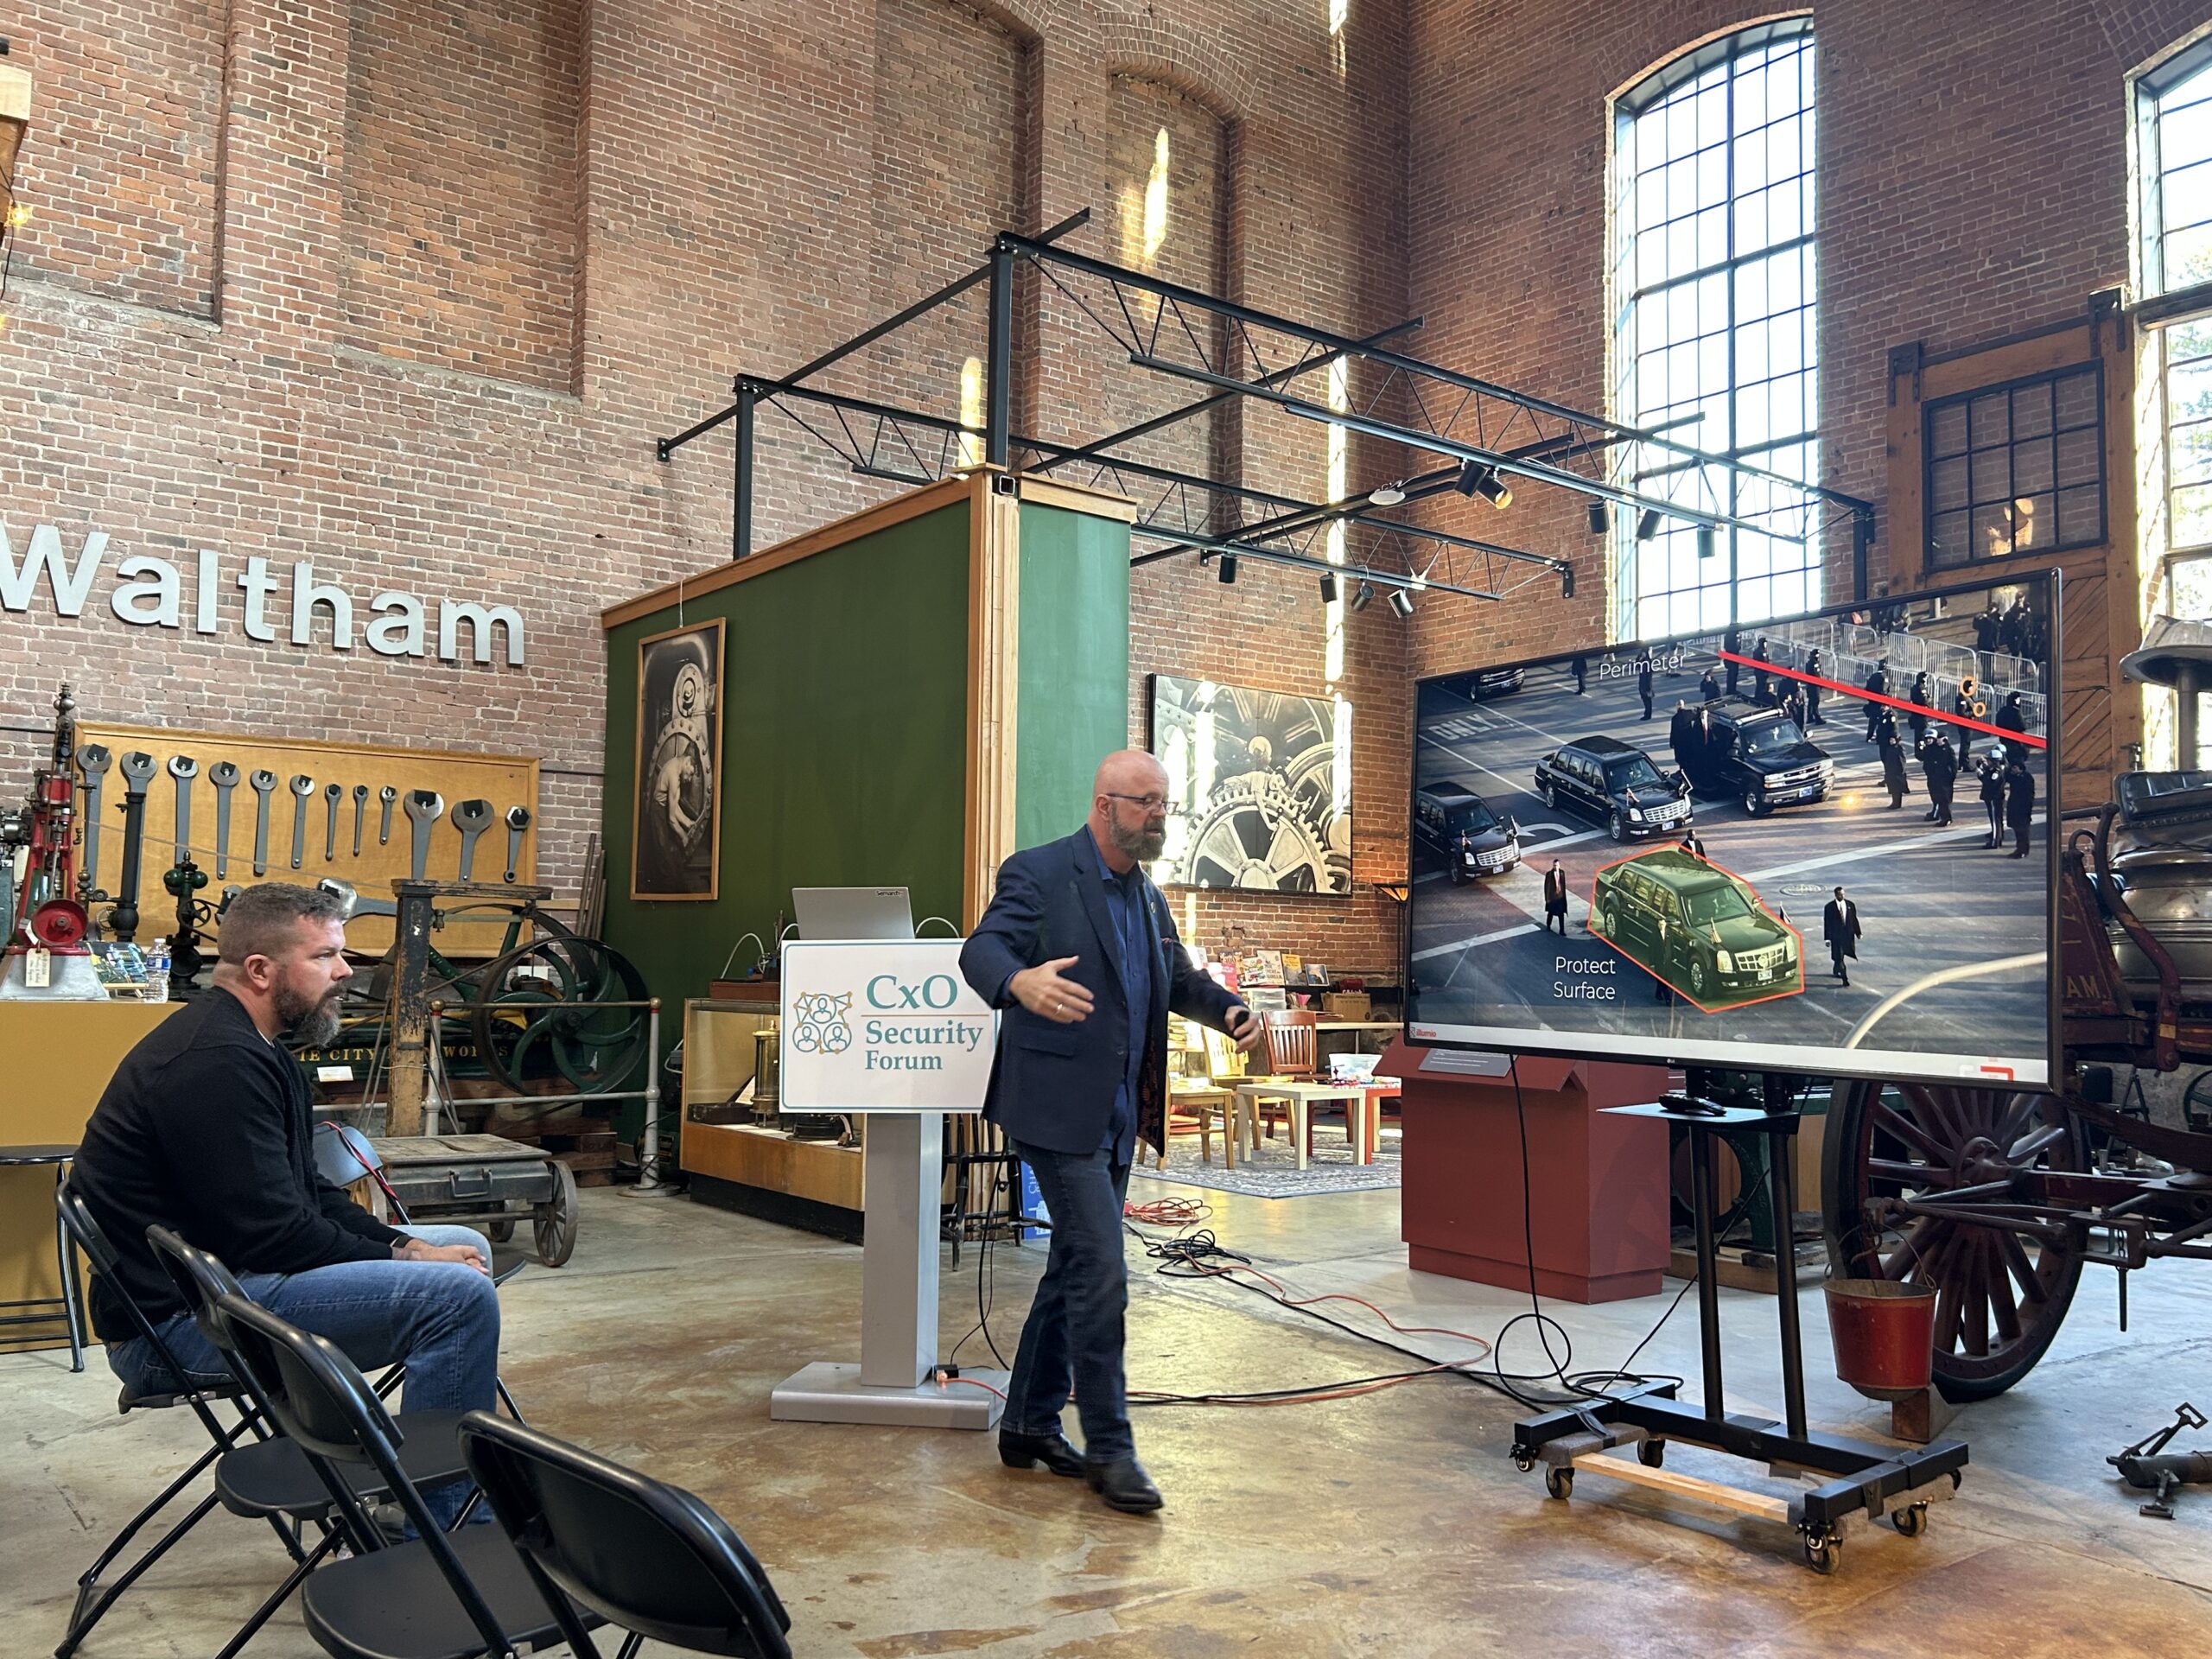
The goal of the CxO Security Forum is to build a trusted community for senior executives tasked with cybersecurity, risk management and compliance. Michael will ensure participants leave with immediately actionable insights.
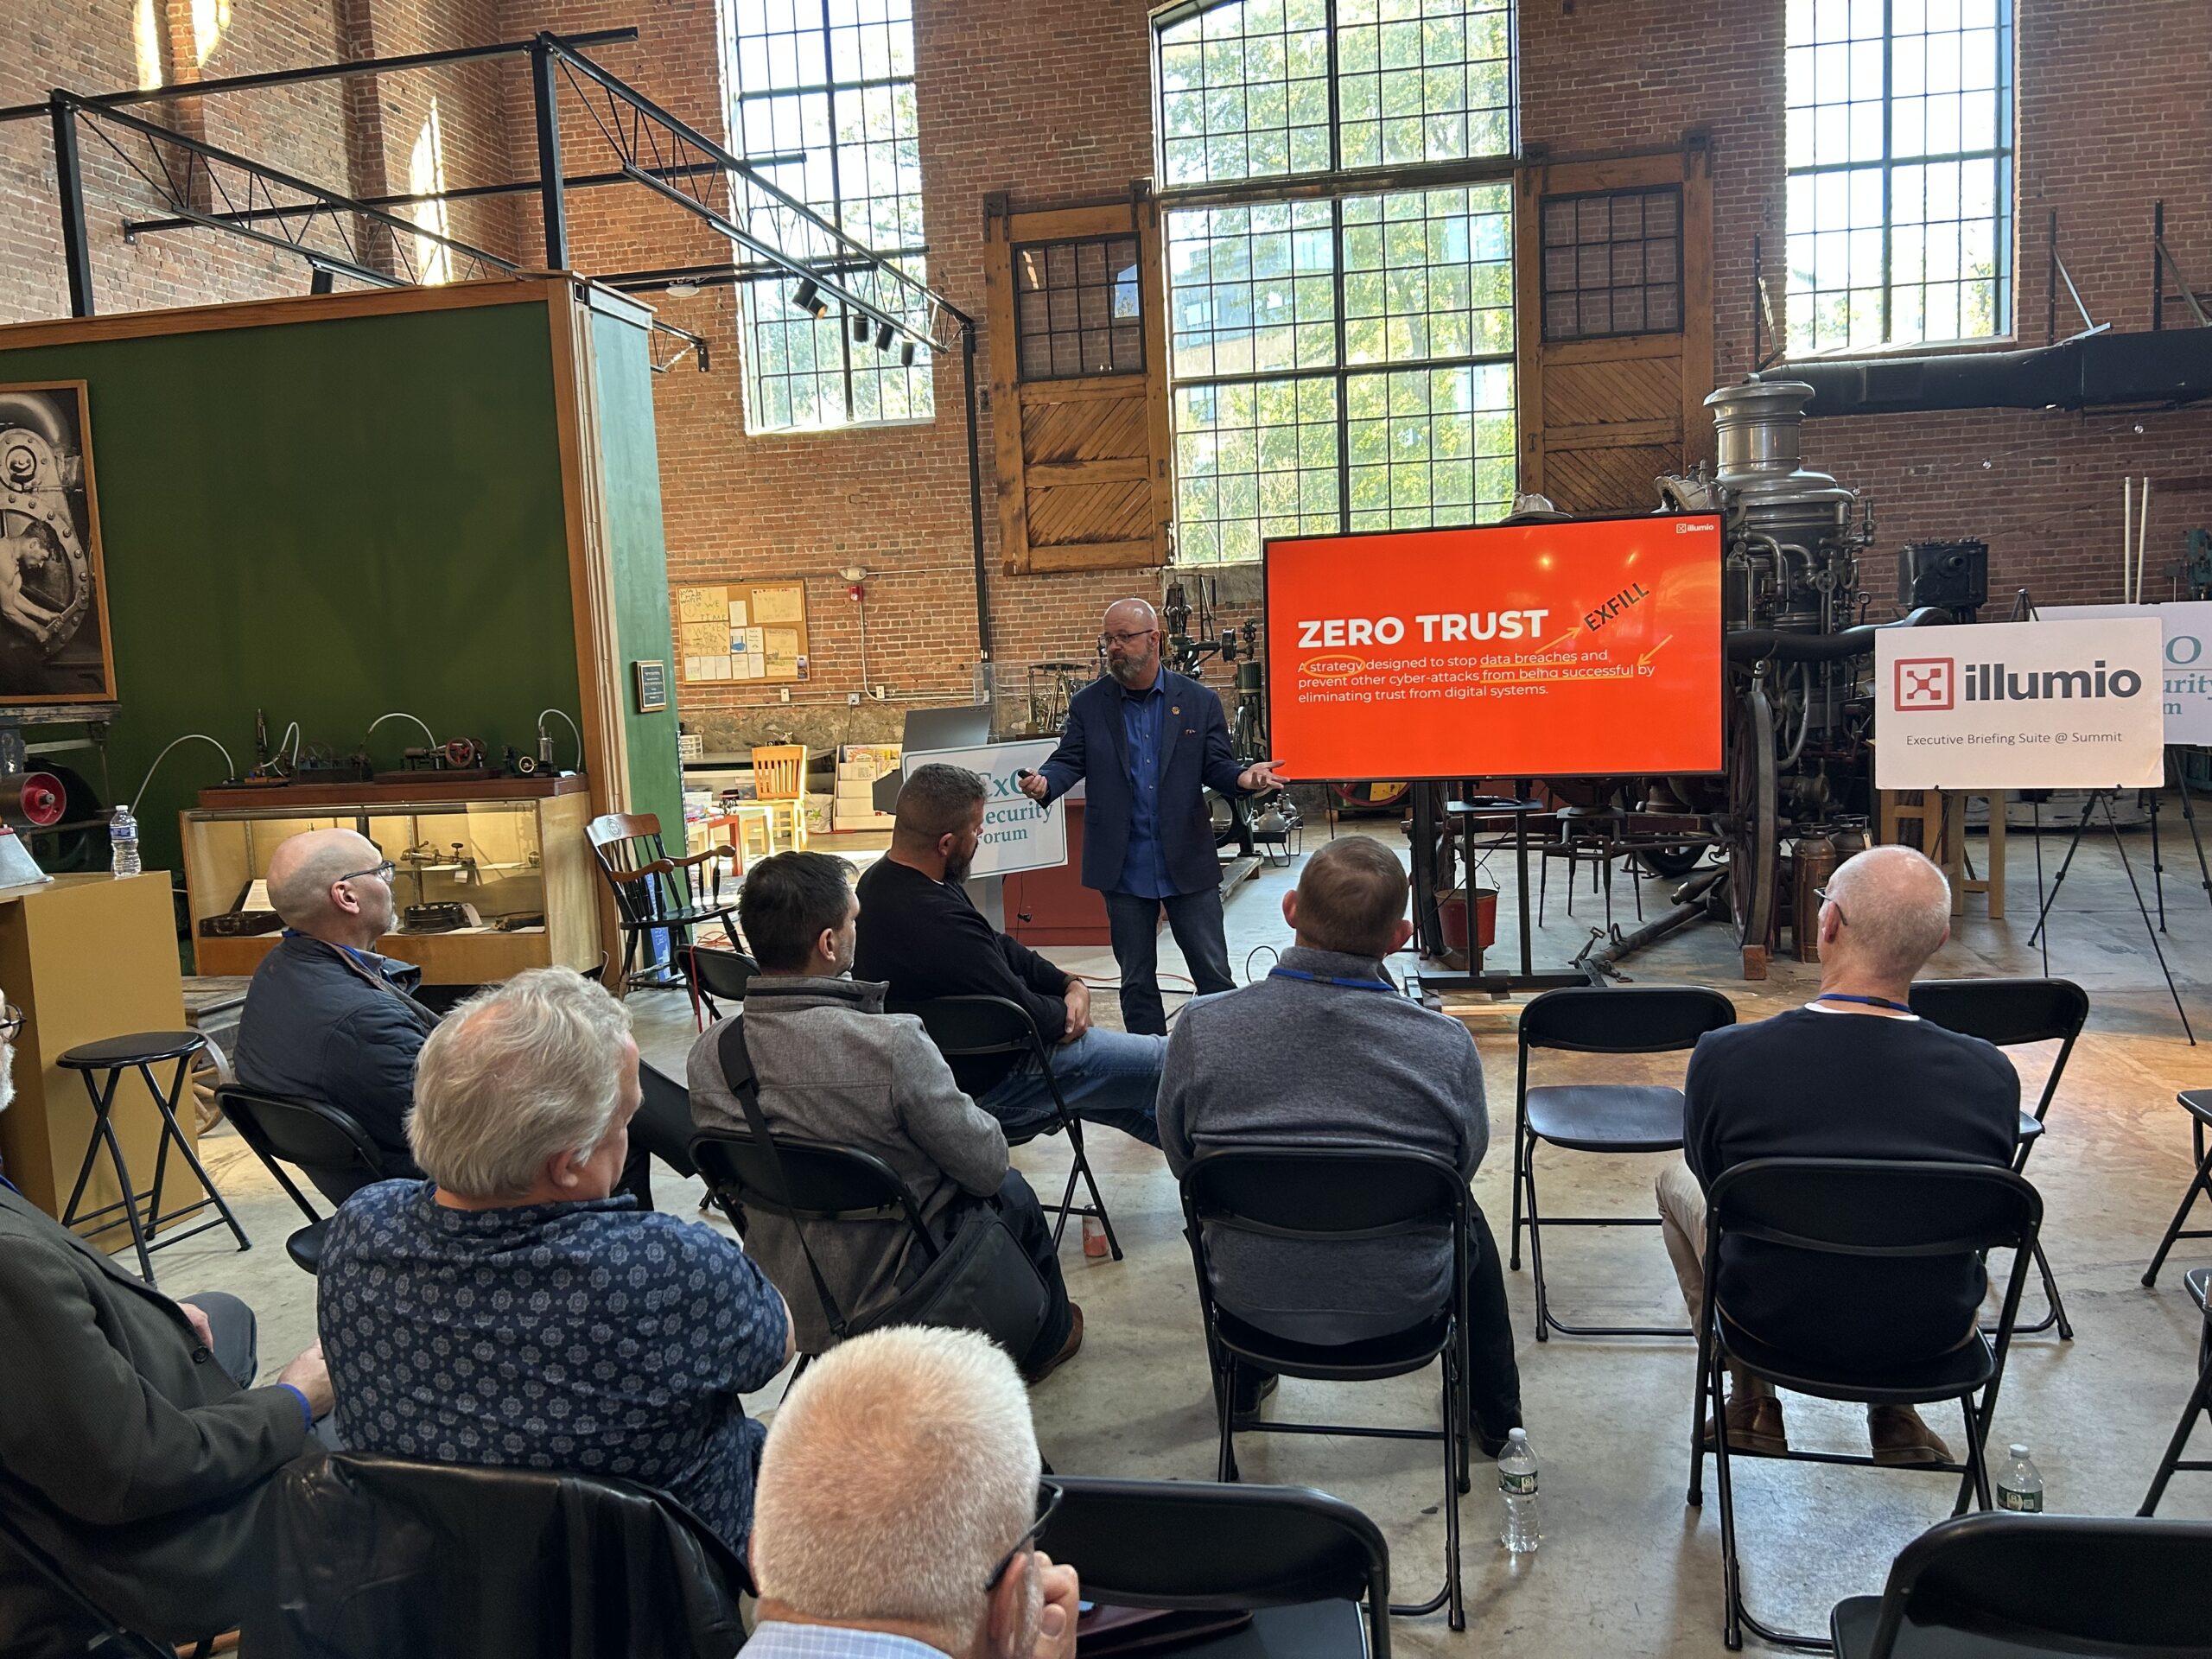
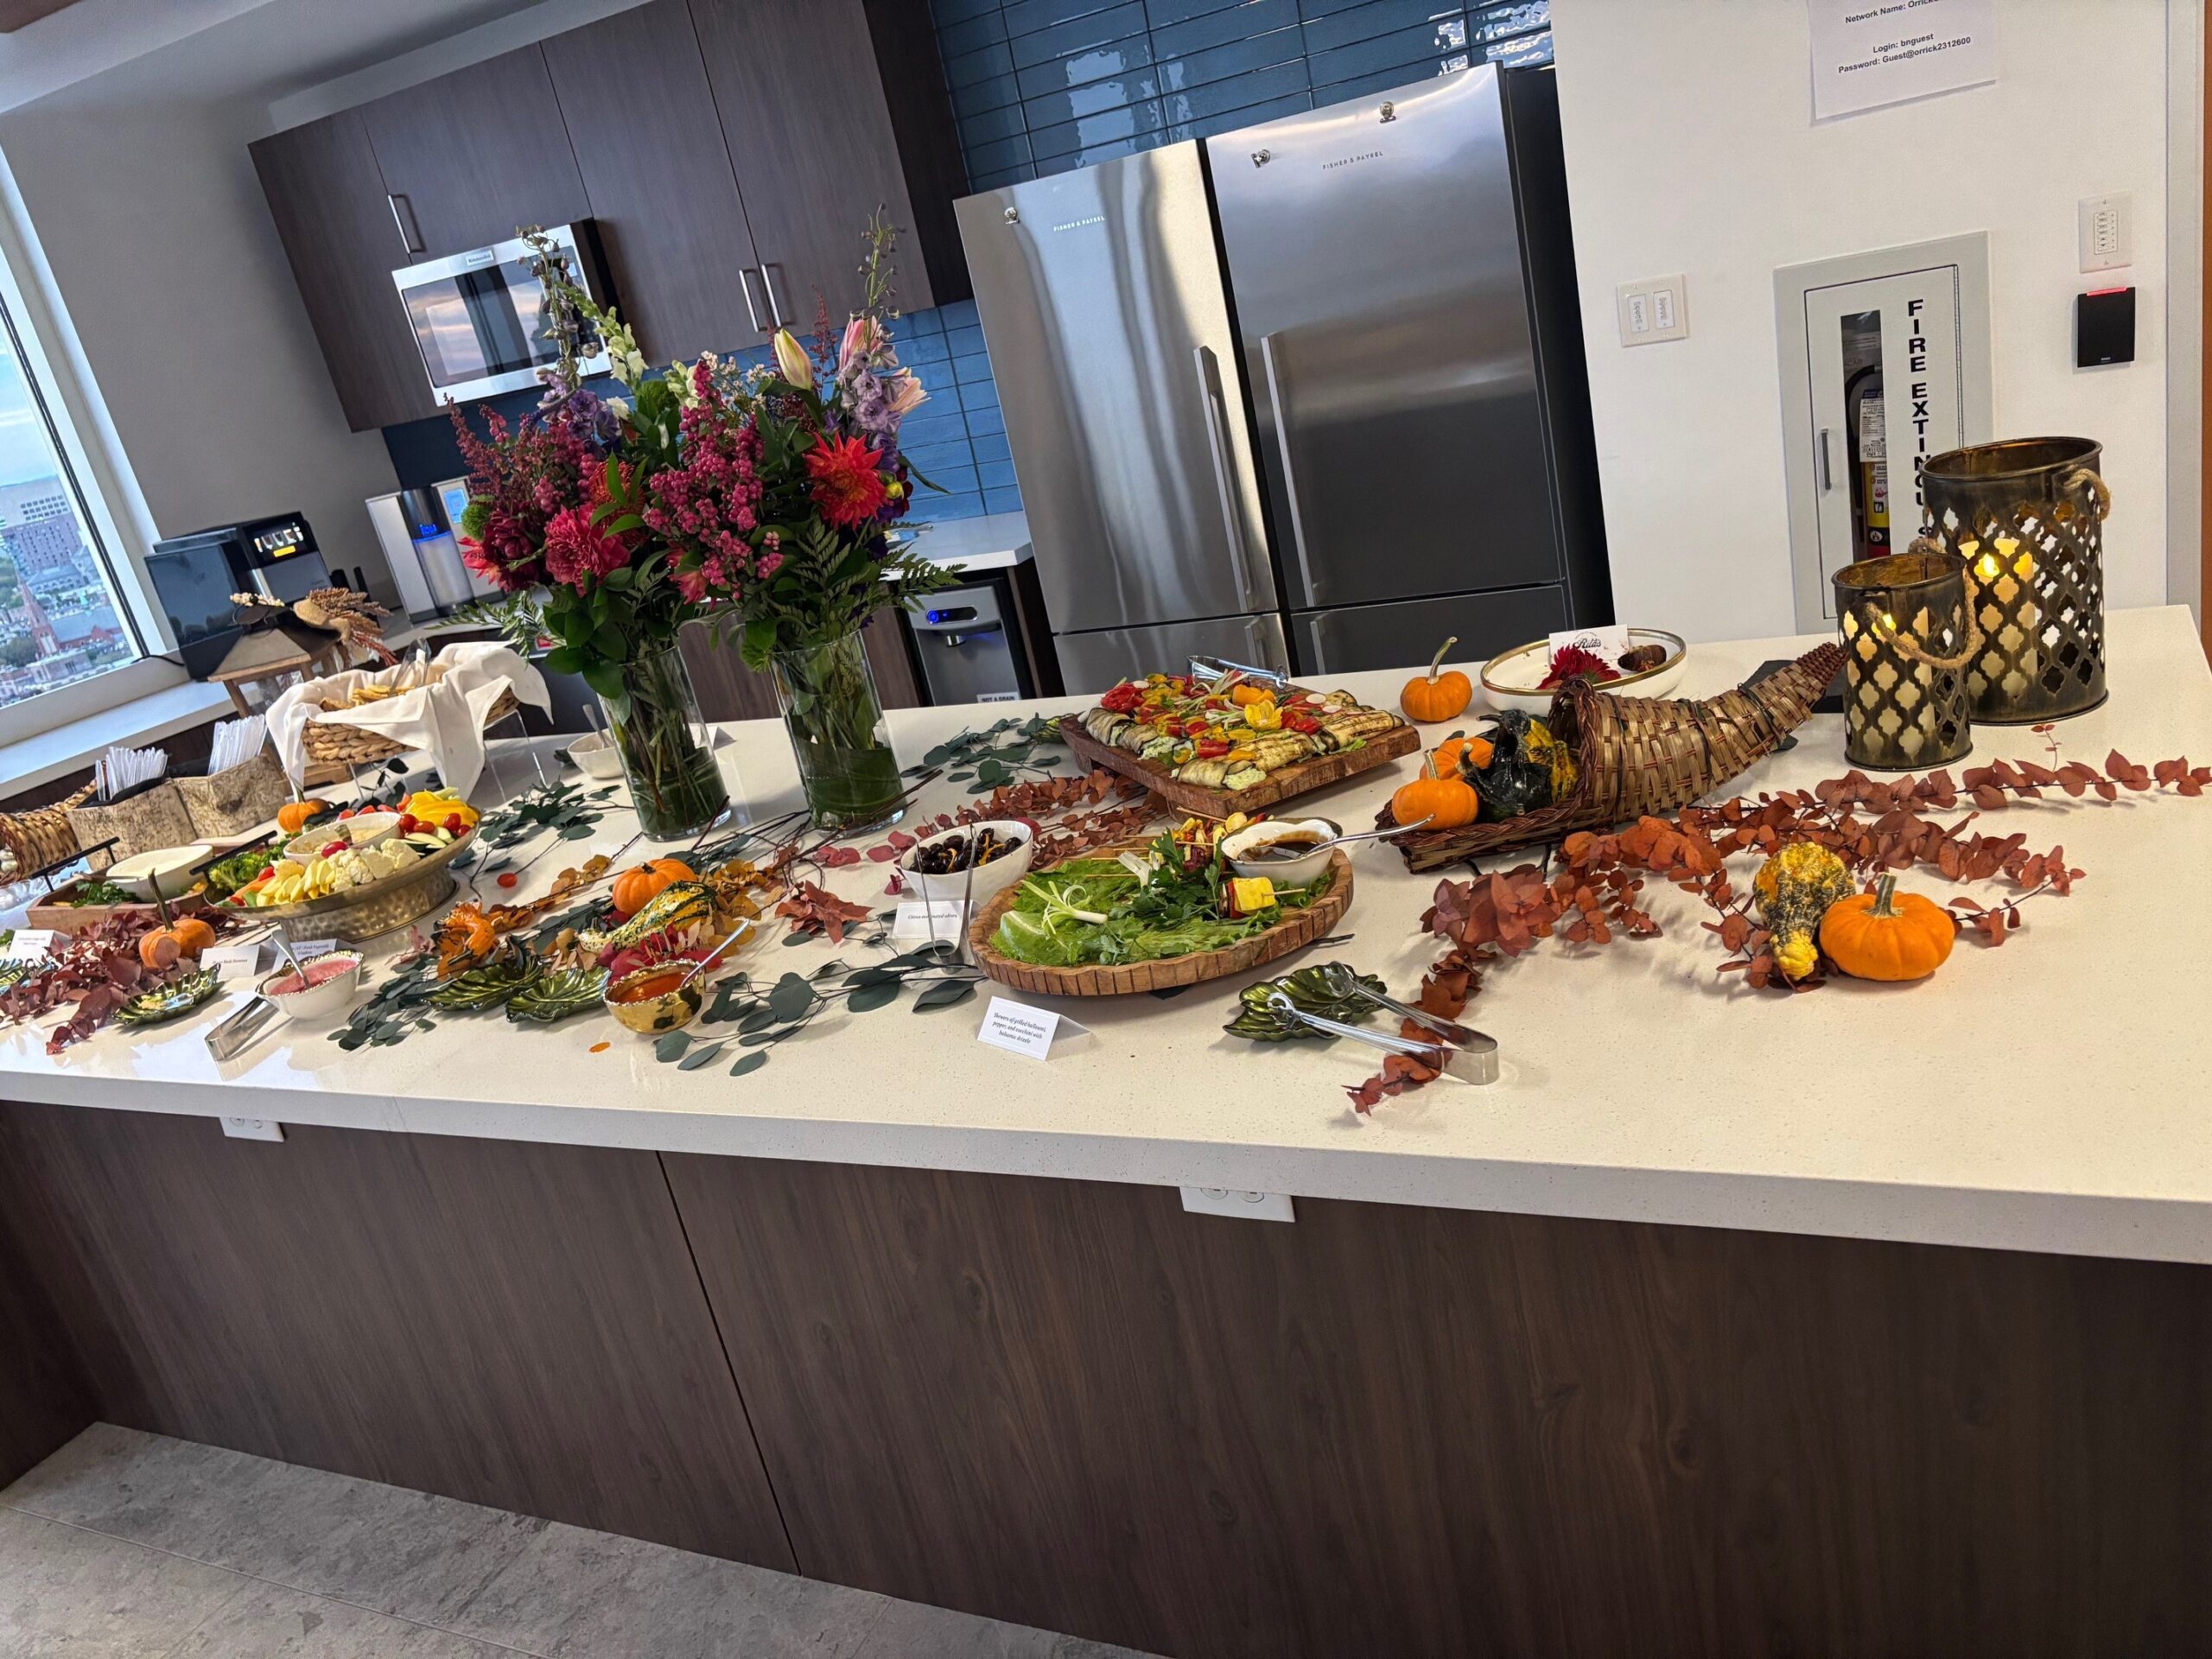
About CxO Forum
CxO Security Forum began as a response to a common frustration among senior cybersecurity leaders: the way enterprise solutions are marketed, sold, and evaluated is fundamentally broken. What started as a call for change has grown into a trusted community that puts executive practitioners at the center of the conversation.
We bring together CISOs, CIOs, and senior decision-makers who are responsible for protecting their organizations, guiding strategic risk, and navigating the evolving role of AI in security. Every forum, gathering, and conversation is designed to foster education, mentoring, and authentic peer connection.
What makes us different is our focus on relationships. Our events are intentionally small, curated, and built for real dialogue. Sponsors are carefully selected, and there are no product pitches. Participants come for thoughtful, actionable conversations that support both professional development and practical decision-making.
At CxO Security Forum, the goal is simple. Give experienced leaders a space to learn from one another, to share insight, and to build meaningful connections that last beyond the event itself.
Participation is free for qualified senior executives
Location
TBD
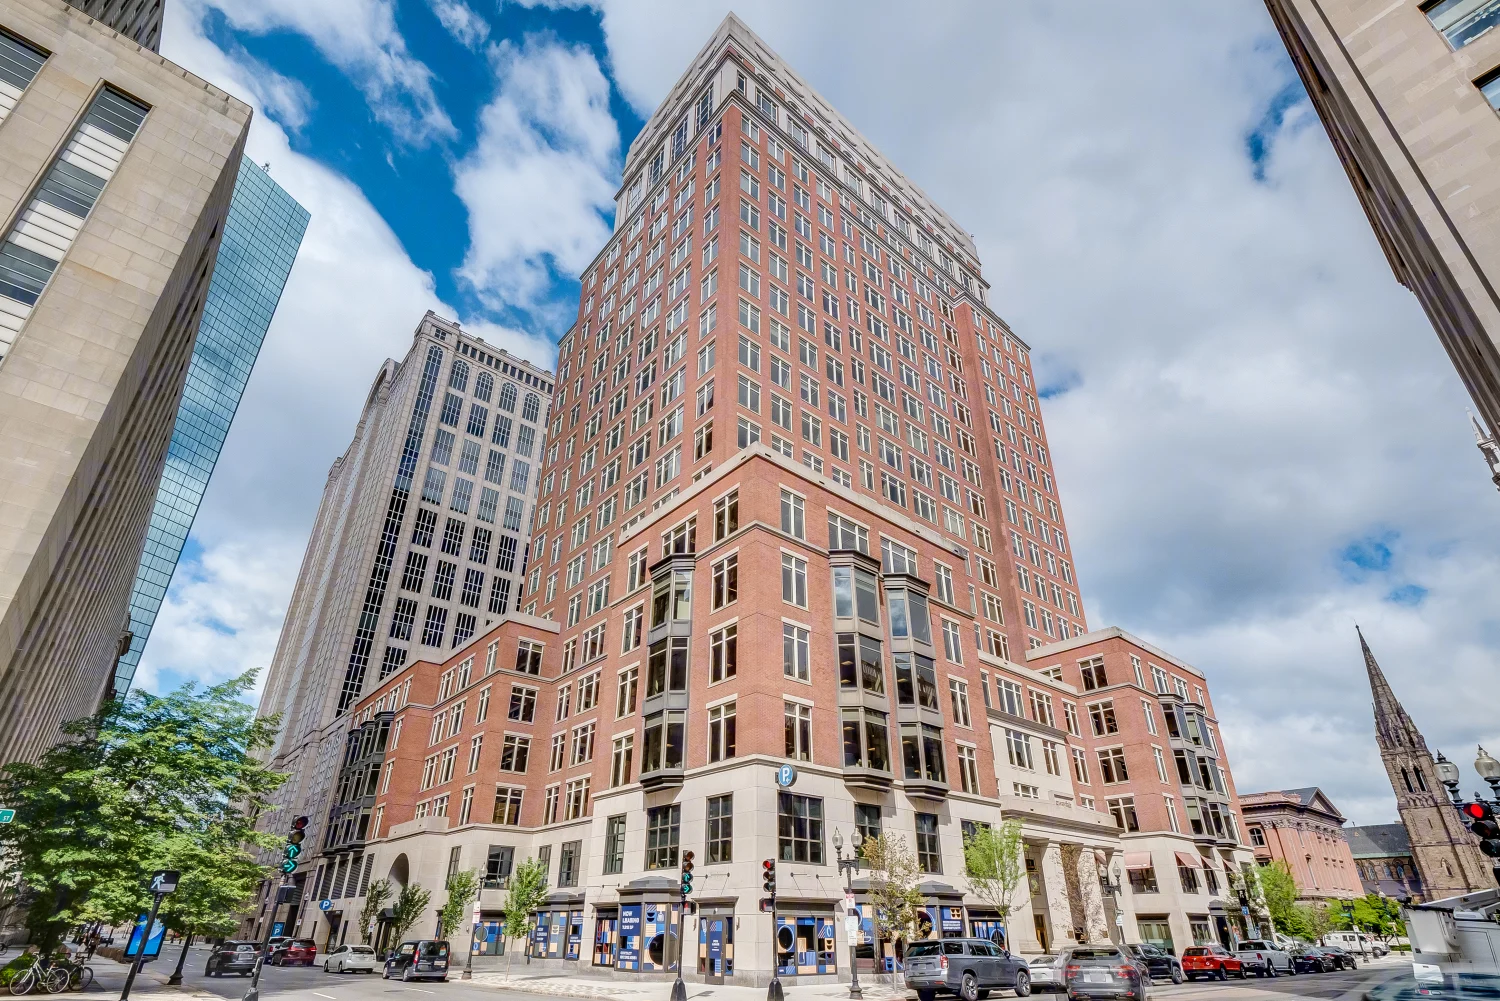
222 Berkeley Street (at Boylston), 20th Floor
Registration
Registration is open only to qualified executives (excluding Sales, Marketing, and Business Development!)
© 2026 CxO Security Forum. All rights reserved