RAPIDS 2026 — Water & Critical Infrastructure Security Summit
Securing the Systems That Manage the Colorado River
8 December 2026
Days
Hours
Minutes
Seconds
Resilient & Adaptive Cyber Protection of Industrial Control Devices & Systems
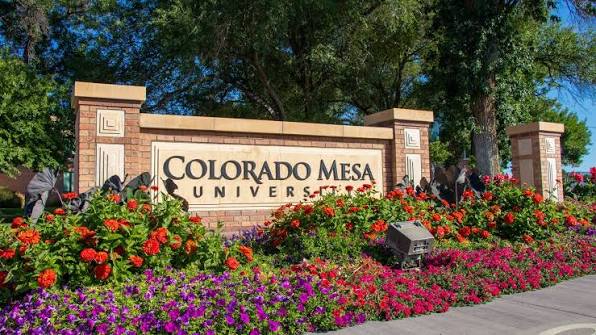
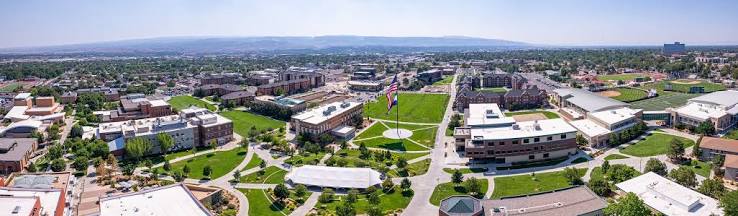
Hosted at Colorado Mesa University · Grand Junction, Colorado
Participants
FULL Registration is just $25
($25 includes breakfast, lunch, full access and CPE credits)
Why the Colorado River Is a Cybersecurity Problem
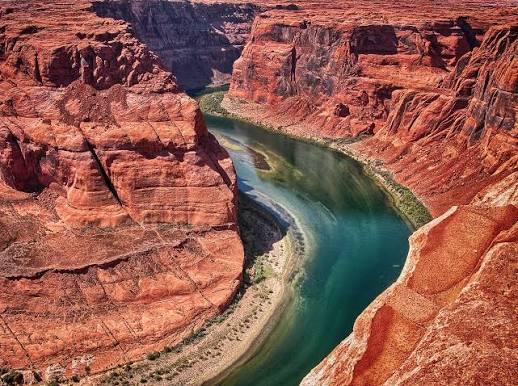
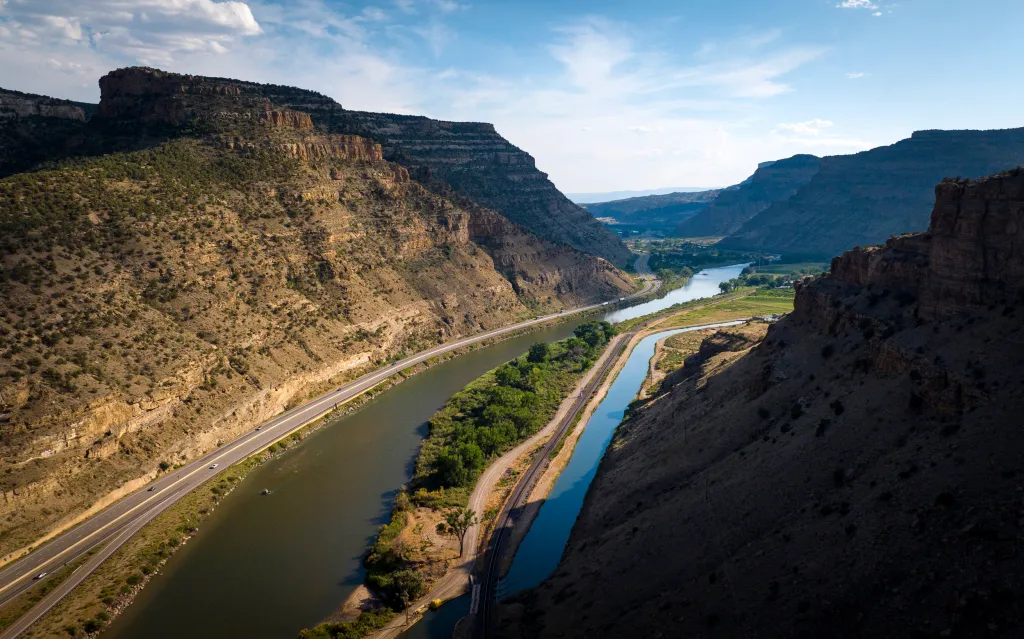
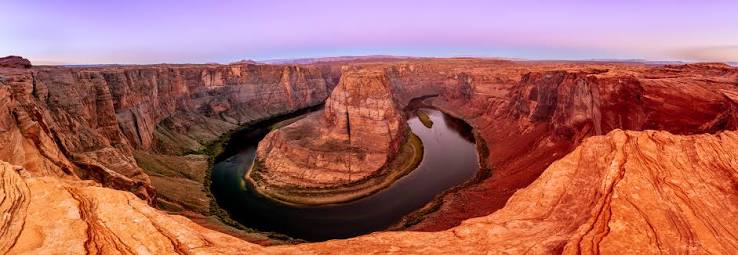
Forty million Americans drink, irrigate and power their lives from the Colorado River, and much of the infrastructure that moves it is still run by hand, because the control systems that could automate it aren’t secure. RAPIDS 2026 brings water operators, CISOs, OT engineers, policymakers and Colorado Mesa University students to Grand Junction, where about 68% of the river’s volume passes, for one practitioner-first day on securing the industrial control systems behind critical infrastructure. Short framing talks, then roundtables under Chatham House Rules. The conversation belongs to the room.
Why it matters:
- ~40M people served
- ~25% of U.S. economic activity
- ~5M acres irrigated
- 2–4M acre-foot annual deficit
- ~68% of the river’s flow passes through Grand Junction
What is RAPIDS?
RAPIDS (Resilient & Adaptive Cyber Protection of Industrial Control Devices & Systems) is a consortium building a repeatable model for securing the industrial control systems behind critical infrastructure, starting with the Colorado River. Its first step is Minimum Viable Measurement: the smallest set of secure, verifiable measurements every stakeholder can trust. Partners include Colorado Mesa University, GJEP, the Colorado River District, the City of Grand Junction, Mesa County and Colorado OEDIT. [Learn more at rapidsproject.com]
Who Should Attend:
- Water and utility leaders: district GMs, operations and engineering
- CISOs, CIOs and security leaders responsible for OT, ICS or SCADA
- Public-sector and emergency-management leaders
- Technology and measurement partners (by invitation)
- Academic, workforce and CMU students
- Funders
Technology and measurement partners attend by invitation. No vendor pitches.
How the day works:
Short framing talks in the morning. In the afternoon, peer-only roundtables, each seeded by a speaker:
- Defining Minimum Viable Measurement
- Hardening what’s already deployed
- The workforce pipeline
- Funding & partnership
The day closes with table report-outs and a draft set of shared principles.
Agenda - 8 December 2026
8:30 | Registration & coffee | |
9:00 | Welcome & civic framing | Michael Hiskey (Emcee) · Mayor Cody Kennedy |
9:15 | The RAPIDS vision | Kurtis Minder |
9:40 | Keynote: The threat landscape | Richard Stiennon |
10:10 | Morning break | |
10:30 | Cyber-physical risk in water systems | Beau Woods |
11:05 | Measurement & data integrity (MVM) (topic to be confirmed) | Dean Ford |
11:40 | Operator & implementation view (topic to be confirmed) | Andy Mueller |
12:10 | Lunch provided by Colorado Mesa University | |
1:10 | Building the workforce | Taylor Banks |
1:45 | Panel: Securing the Colorado | Moderated by Michael Hiskey · all speakers |
2:25 | Afternoon break | |
2:40 | Closing & call to action | Kurtis Minder |
3:00 | Networking reception | |
Registration & Networking
8:30 AMWelcome/Introductions
The Summit is a collaboration point for the many member-driven professional associations across the region. Hear a brief introduction from Board Members of each of those InfoSec & Fraud Associations as we open the agenda
9:20 AMThe State of Cybersecurity 2026: Mapping the Industry, Measuring AI’s Real Impact, and Making Sense of 4,550 Vendors [Discussion Pod #1]
Richard Stiennon, veteran analyst and industry provocateur will kick off the Summit, taking us on a data-rich tour of the entire cybersecurity industry—all 4,550 vendors, 660 subcategories, and $12 billion in recent funding. Drawing from his forthcoming book, Stiennon will share insights derived from two decades of studying cyber trends at Gartner and now IT-Harvest—the only firm systematically cataloging the global cyber vendor ecosystem.
This talk is not just about the numbers. Richard will break down the practical implications for executives:
- How to navigate a vendor landscape bloated with similar claims and vague value props
- Where AI is truly being built in cybersecurity—what’s real, what’s noise, and what agentic AI might change
- What vendor origin says about product capability, reliability, and alignment with enterprise needs
- Why vendor consolidation isn't the answer—and what to do instead
He’ll also spotlight key global dynamics, such as Israel’s IDF-fueled innovation engine, Germany’s vendor loyalty culture, and the emergence of AI Security as a distinct and fast-growing segment.
If you’ve ever asked “What should I actually be paying attention to in cybersecurity right now?”—this is your answer. This session will set the tone and context for the day, offering a strategic foundation for every discussion that follows.
9:45 AMWhen Cyber Hits the Fan: Who to Call, What to Share, and How to Get Real Help [Discussion Pod #2]
John Felker, former Assistant Director for Integrated Operations at CISA, will lead a discussion to cut through the confusion. Drawing on decades of leadership across government, military, and private-sector cybersecurity, Felker will explain how key agencies actually fit together, when each should be engaged, and how organizations can build relationships before an incident occurs.
When a serious cyber incident unfolds, most security leaders face the same problem: who do you call first, what do you share, and how do you get meaningful help fast? Between CISA, the FBI, Secret Service, regulators, ISACs, state fusion centers, and InfraGard, the landscape can feel fragmented—especially under pressure.
He will also address a major shift in the cyber landscape: in many cases, the private sector now develops threat intelligence as fast as—or faster than—the government. As AI, quantum, and nation-state activity accelerate risk, effective defense increasingly depends on trusted two-way collaboration.
The moderated discussion to follow will focus on real operational scenarios: when to call CISA vs. the FBI, how to engage government partners without triggering unnecessary scrutiny, how ISACs and InfraGard fit into an enterprise threat-intelligence strategy, and what practical steps CISOs can take to build trusted relationships before an incident occurs.
10:20 AMInside the Mind of the Adversary: Espionage, Negotiation, and the Battle for Digital Control [Discussion Pod #3]
Kurtis Minder has spent the last decade doing what most cybersecurity professionals only read about—negotiating directly with cybercriminals, including ransomware gangs, nation-state affiliates, and digital extortionists. As the founder and CEO of GroupSense, Minder built a world-class cyber espionage team, managing over 4,000 personas in multiple languages. He helped victims navigate headline-making ransomware attacks, and briefed everyone-from Congress to the Intelligence Community.
In this gripping, TED-style keynote, Kurtis draws from his new book, Cyber Recon, and his real-world experience leading some of the largest ransomware response efforts globally. He’ll walk attendees through the tradecraft of cyber reconnaissance, the nuances of engaging threat actors using mindful negotiation, and what it really takes to protect your organization in today’s hostile digital landscape.
Blending operational insights with personal stories—from fake identities like “Vinny,” to briefing Congressional subcommittees—Kurtis offers a rare, behind-the-scenes look at the human element of cyber conflict. Whether you lead security for a Fortune 500 or a regional bank, you’ll leave with concrete lessons on digital risk, negotiation, and resilience in the age of cybercrime.
The CVE Ecosystem Today & the AI Agents Burning Watts to Fix It [Discussion Pod #4]
Tim Rohrbaugh, back at NEACS by popular demand, has taken a very deep look at the CVE pipeline (Common Vulnerabilities and Exposures), its 429 CVE Numbering Authorities (CNAs), timelines of reporting, and the ecosystem of scores, updates, and rankings.
News Flash: Everything we know about CVEs is wrong.
The CVE pipeline is bursting at the seams—and the downstream ecosystem that enterprises rely on to make sense of it (CVSS scores, vendor advisories, scanners, ticketing) is lagging, inconsistent, and noisy. Meanwhile, security teams are asked to do more with less while the volume of new "Published" and Updated CVEs are relentless.
In this session, Tim explores what’s fundamentally broken—then shows how cyber leaders can deal with it. He will demonstrate how small teams can stand up trustworthy, domain-tuned synthetic-reasoning agents (AI) to shoulder the grunt work for quality analysis that can give teams focused daily updates to protect systems and data.
Participants will learn:
- Where the current understanding of CVE/NVD/scorecard is broken—and what to stop trusting and start questioning.
- How to build “home-grown” AI assistants that prioritize, explain, and script fixes safely.
- How to use Distillation to make efforts highly accurate without exposing sensitive details
Lunch & Solution Showcase Networking Discussions
Participants will enjoy a lovely full hot lunch while connecting with the thoughtful Solution Providers who are supporting the community at the Summit!
12:20 PMIt’s Not Just Bad Hygiene—It’s Criminal Negligence [Discussion Pod #5]
What the Largest Bank Fine in U.S. History Means for Cybersecurity Leaders
Presented by: Special Agent Carlo Nastasi, IRS-Criminal Investigations
Moderator/Framing Remarks: Michael Hiskey, Founder – CxO Security Forum
IRS-Criminal Investigations will talk us through what started as a routine money laundering investigation and then became the largest criminal BSA case in U.S. history: TD Bank pled guilty and paid a record-breaking $3 billion fine for failing to detect and report financial crimes between 2018 and 2024. But this wasn’t just a banking compliance failure—it was a breakdown of fundamental controls that cybersecurity teams should recognize as eerily familiar: weak identity verification, outdated monitoring tools, no internal escalation, and massive blind spots in onboarding.
With the passage of the AI Clarity Act and GENIUS Act, any company involved in digital asset transactions—especially fintechs and crypto-related entities—will now fall under the Bank Secrecy Act (BSA). That means cybersecurity functions may be criminally liable if they fail to detect malicious or illicit behavior.
This session reframes cybersecurity risk from “fear of breach” to fear of prosecution. If your organization touches crypto, stablecoins, or manages digital financial flows, this talk is your wake-up call. Learn what went wrong at TD, how BSA violations can stem from cyber failings, and what proactive cyber leaders should do now to protect not just their companies—but themselves.
1:15 PMAgentic AI Meets Zero Trust: What Actually Breaks—and How to Fix It [Discussion Pod #6]
Presented by: Josh Woodruff, Author, Agentic AI + Zero Trust
In the rush to deploy autonomous/semi-autonomous AI, Community Members have shared their doubts that existing identity, data, and control frameworks are ready. Drawing from years of research for his book and field experience, Josh will share:
- Why most agentic AI initiatives fail operationally, not technically
- How Zero Trust principles must evolve for AI agents, workflows, and non-human identities
- Where security teams need to rethink identity, authorization, and monitoring
- What CISOs and CIOs can do now to avoid costly architectural mistakes
This session blends short-form insights with moderated group discussion, focused on immediately actionable takeaways for enterprise leaders.
1:50 PMDegrees, Certs & Entry-Level Grit: What Cyber Grads Can (& Can’t) Do For You
[Panel]
This panel discussion features a real-world exchange between cyber educators and industry leaders. Professors will share how they’re designing programs with hands-on labs, industry-funded projects, and even high school hackathons. CISOs and CTOs will weigh in on the “last-mile” problem: grads with zero experience, mismatched expectations, and a professionalism gap that’s hard to ignore.
With over 700,000 unfilled cybersecurity jobs in the U.S., you’d think the hiring problem would solve itself. But here’s the rub: cybersecurity programs are churning out grads, and CISOs still ask, “What can they actually do on day one?” Are they SOC-ready? Do they understand fraud prevention, governance, compliance—or even what cybersecurity is?
We’ll dig into big questions:
- Are four-year degrees still the gold standard—or are certs and bootcamps the smarter play for mid-career upskilling?
- How do you hire interns and set expectations when “everyone is busy”?
- What can companies do (without breaking budgets) to actually shape the talent pipeline?
- And how can we close the generation gap without lowering the bar?
Come for the honest dialogue, stay for the practical takeaways—and leave with a few ideas for fixing a system that isn’t working for educators, employers, or students.
2:30 PMThe Next Breach Won’t Look Like the Last One: Preparing for What You’re Not Measuring [Discussion Pod #7]
Every security program today is optimized to prevent the last breach.
The controls, dashboards, budgets, and board conversations are all shaped by yesterday’s incidents—ransomware, phishing, endpoint compromise. But the next wave of risk is already forming outside those models: non-human identities, AI-driven decisioning, supply chain entanglement, and silent data manipulation that doesn’t trigger alerts.
In this closing session, we’ll challenge a dangerous assumption: that improving today’s controls will protect you from tomorrow’s threats.
This discussion will explore:
- Why most enterprise security programs are overfit to known attack patterns
- Where visibility is breaking down (AI agents, APIs, third-party logic, machine-to-machine trust)
- How attackers are shifting from disruption to subtle manipulation and persistence
- Why traditional metrics (MTTR, patch SLAs, alert volume) may be giving false confidence
- What leading organizations are doing to rethink detection, trust, and resilience before the next wave hits
This is not a prediction talk. It’s a reality check. Expect a fast-paced, candid discussion that forces a simple but uncomfortable question: What risks are we blind to—because we’re not even looking for them?
3:00 PMClosing Discussion & Networking
Stay & Connect: Informal Networking + Solution Showcase
Before hitting the road, grab a coffee and take time to connect. Trade insights with peers, chat with Solution Providers, and follow up on the ideas sparked throughout the day.
No panels, no pitches—just real conversations to wrap things up right.
3:30 PMA Full-Day Convening of the RAPIDS Consortium
Speakers & Discussion Leaders
Agenda is still being confirmed — planned Discussion Leaders include:
Cody Kennedy
CIVIC WELCOME
Council Member (District A) &
former Mayor, City of Grand Junction
Cody Kennedy represents District A on the Grand Junction City Council. He was first elected in April 2023 and re-elected in 2025, and served as Mayor for the 2025–2026 term.
Before joining council, Kennedy served Grand Junction for 17 years as a police officer, finishing his career as a detective investigating complex financial crimes and homicides.
He is a small-business owner with 20 years in the Grand Valley's housing sector and volunteers with a local nonprofit helping residents facing housing scarcity. His council priorities include fiscal responsibility, affordable housing and public safety.
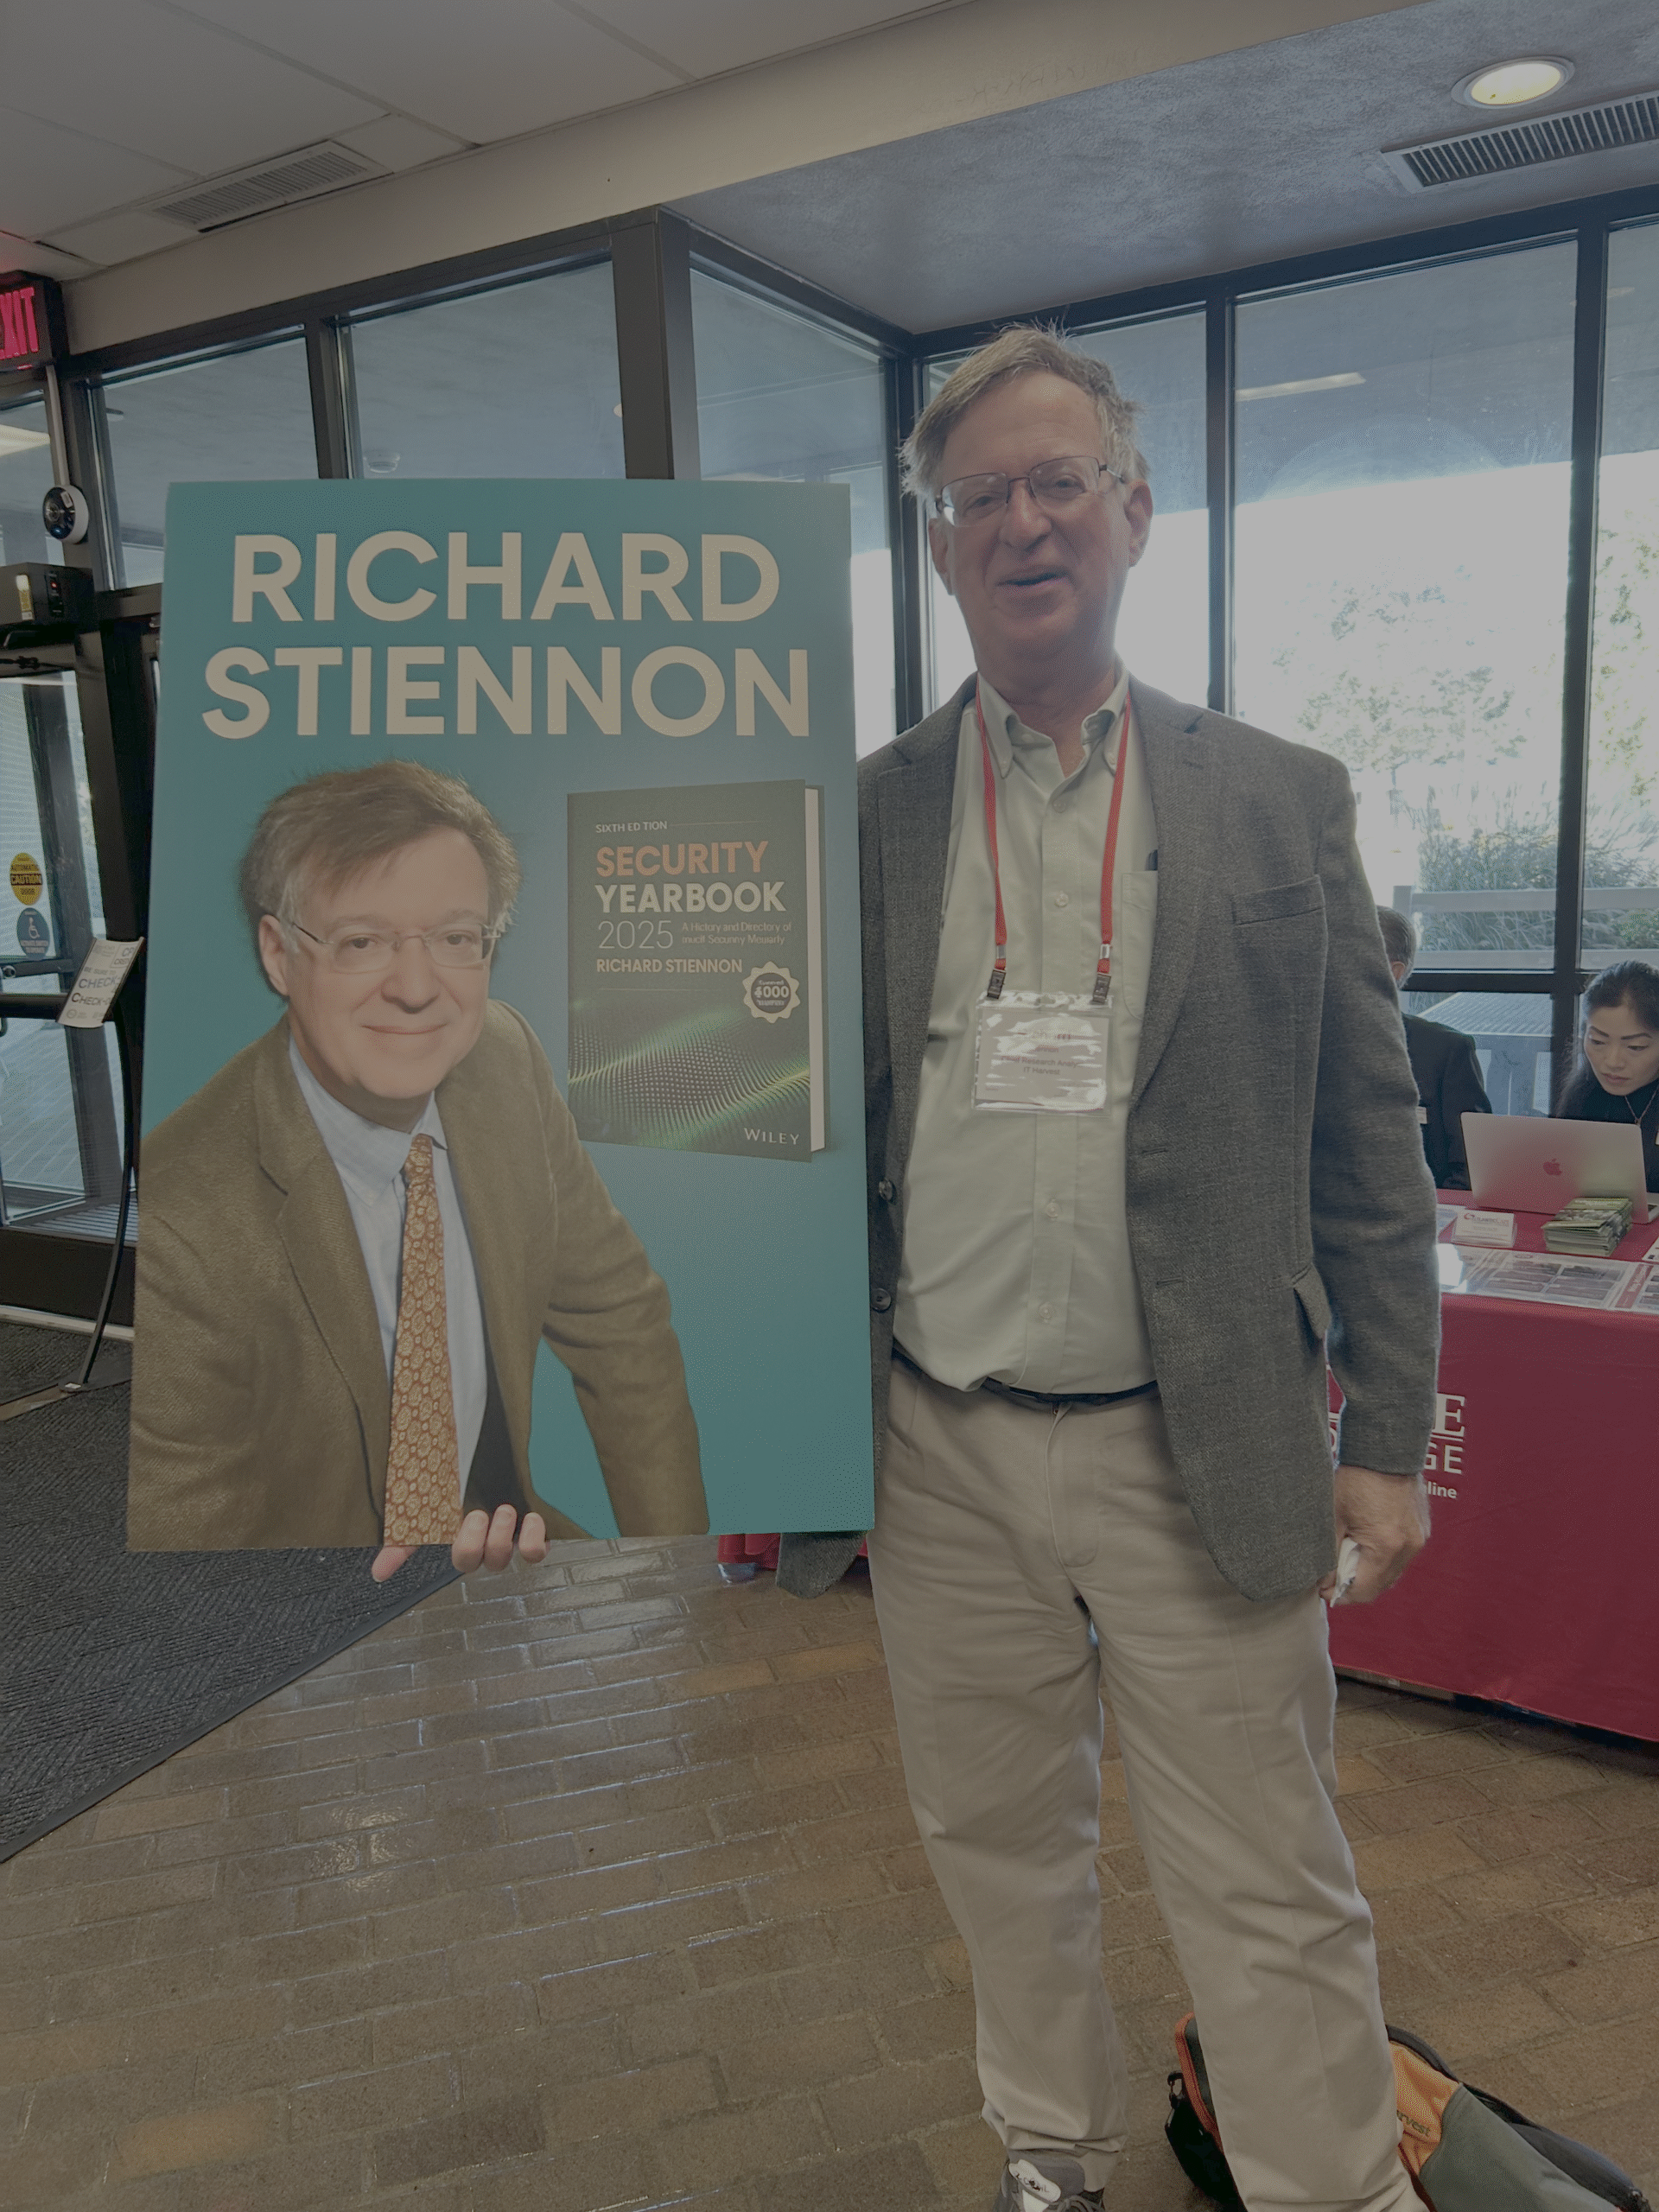
Richard Stiennon
Chief Research Analyst - IT Harvest
frmr. VP of Research - Gartner
Richard Stiennon is Chief Research Analyst at IT-Harvest, the data-driven research firm he founded in 2005 to track the vendors that make up the IT security industry. He joined Gartner in 2000 as its second security analyst and rose to VP of Research, then served as VP of Threat Research at Webroot, CMO at Fortinet and Chief Strategy Officer at Blancco Technology Group.
He has written ten books on cybersecurity and the analyst industry, including There Will Be Cyberwar, Surviving Cyberwar and the Security Yearbook series (Wiley). He has spoken in 29 countries on six continents and holds a BS in Aerospace Engineering from the University of Michigan and an MA in War in the Modern World from King's College London.
Curtis Englehart
REGIONAL DEVELOPMENT
Executive Director, Grand Junction Economic Partnership
Curtis Englehart is Executive Director of the Grand Junction Economic Partnership (GJEP), leading economic growth, business development and talent attraction for Grand Junction and Mesa County. He took the role in August 2022, bringing nearly a decade of senior leadership in workforce and economic development.
He previously directed the Mesa County Workforce Center, which he joined in 2015, building partnerships across education, industry and government, and earlier served as a Human Services Administrator with Mesa County. A Western Slope native, he holds a Business Administration degree from Colorado Mesa University.
Kurtis Minder
RAPIDS · Principal, Ping Theory
Kurtis Minder is a technologist, negotiator and author who leads RAPIDS, a Grand Junction initiative using technology and shared data to secure and manage the systems behind the Colorado River.
Minder has more than 20 years in information security. He co-founded GroupSense, a digital risk protection and cyber reconnaissance company founded in 2014, and served as its CEO, building its threat-intelligence operation and leading some of the largest ransomware and data-extortion negotiations on record. Cognyte acquired GroupSense in May 2025. He now advises cybersecurity technology companies and serves as a cyber board advisor.
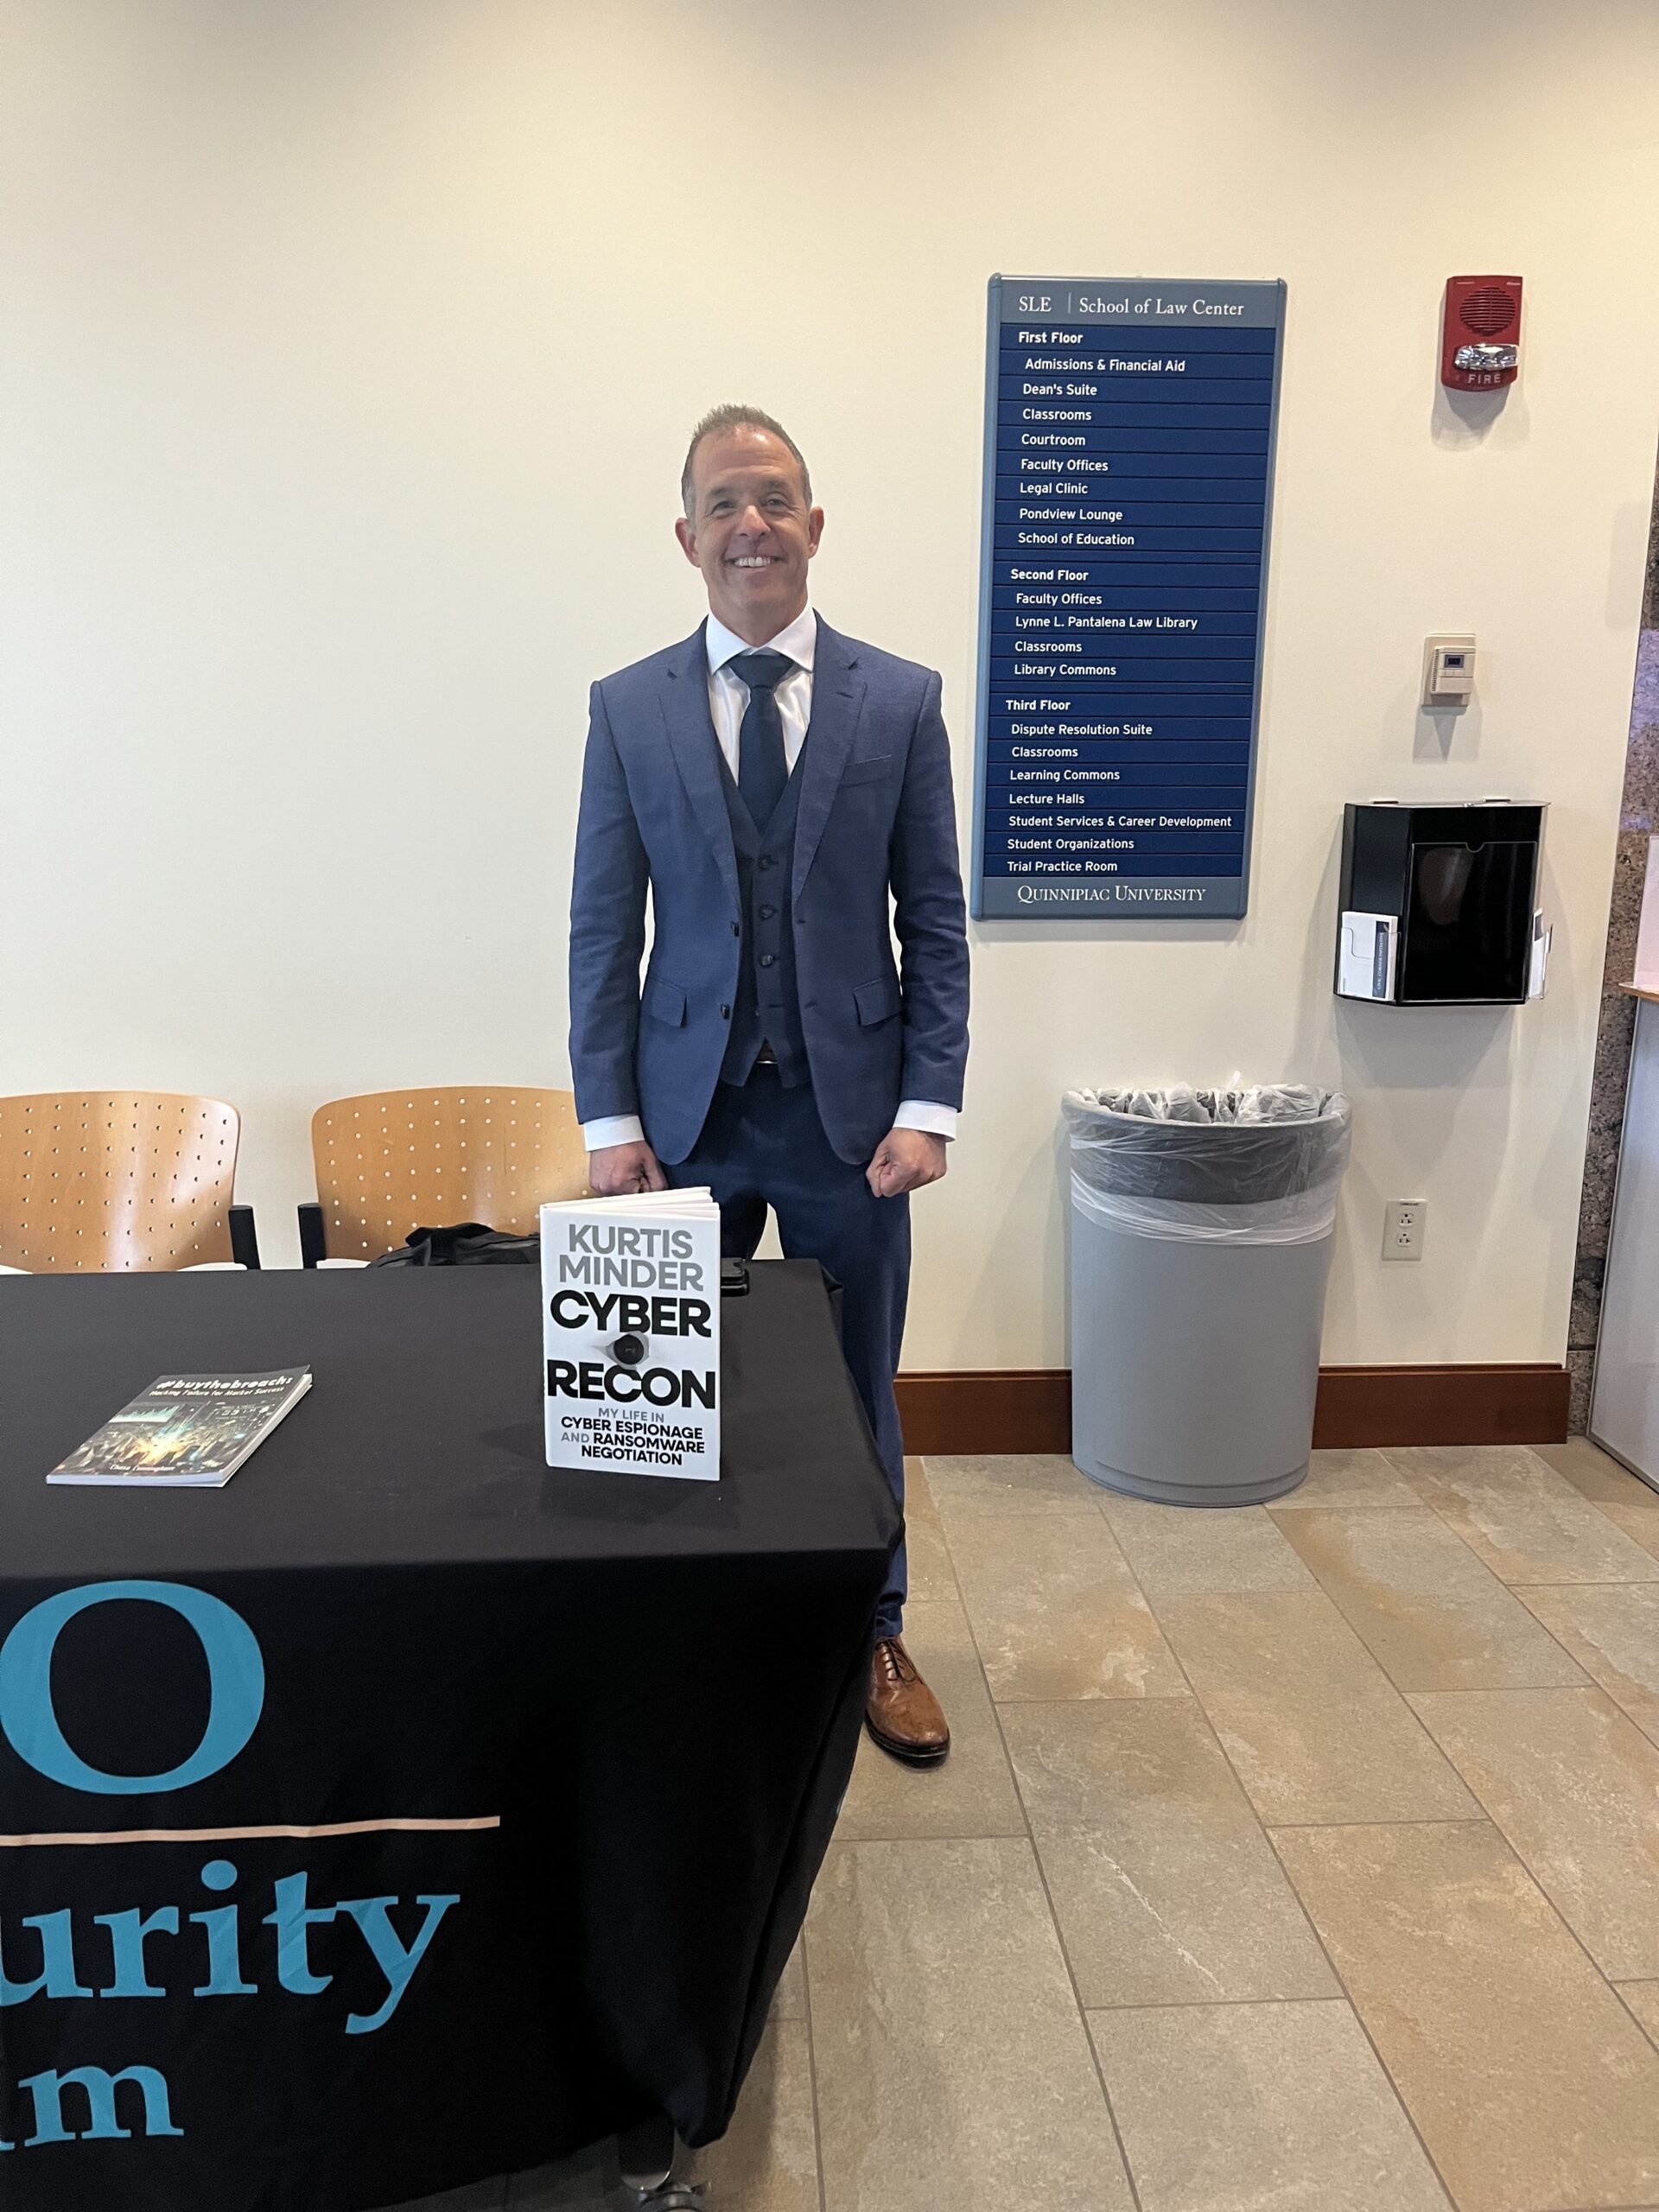
He is the author of Cyber Recon: My Life in Cyber Espionage and Ransomware Negotiation (Wiley, 2025) and holds a FEMA certification in Critical Infrastructure Protection. His work has been covered by The New Yorker, Fortune, WIRED, VICE, CNN and Good Morning America.
Beau Woods
CRITICAL-INFRASTRUCTURE SECURITY
Founder & CEO, Stratigos Security
Beau Woods has more than 20 years advising on cybersecurity, risk and strategy. He is founder and CEO of Stratigos Security, a leader of the I Am The Cavalry grassroots initiative, and a bridge between security researchers and policymakers, focused on making connected technology that affects human life and safety worthy of trust.
He leads Policy @ DEF CON, is a Cyber Safety Innovation Fellow with the Atlantic Council and a founding member of the ICS Village. He previously served as a Senior Advisor at CISA, Entrepreneur in Residence at the U.S. FDA and Managing Principal Consultant at Dell SecureWorks, and has advised Congress, the White House and the energy, healthcare, automotive, aviation and rail sectors.
Dean Ford, CAP, PE
MEASUREMENT & DATA INTEGRITY
Co-founder & Managing Principal Engineer, Muddy Paws Automation
Dean Ford is co-founder and Managing Principal Engineer of Muddy Paws Automation, an operations-first consultancy for plant systems and water utilities, and co-founder of OTEMIS, which is building an AI-powered observability platform linking IT and OT data to physical process behavior. His career spans more than 30 years in manufacturing and utility automation, from process control and industrial IT to IT/OT convergence.
A licensed control-systems engineer in 24 states, Certified Automation Professional and ISA Senior Member, he is past chair of AWWA's Water Utility Technology and Automation Committee and active in WEF and SWAN. He speaks widely on keeping critical infrastructure running, including at BSides Las Vegas. He holds a BSEE from Missouri S&T and an Executive MBA from the University of Maryland.
Andy Mueller
WATER OPERATIONS
General Manager, Colorado River District
Andy Mueller is General Manager of the Colorado River District, the public water-policy agency representing 15 Western Slope counties; he succeeded longtime GM Eric Kuhn in 2018. Before that he spent 23 years in private law practice on the Western Slope, handling water, natural-resource, land-use and community matters, first in Ouray and later in Glenwood Springs.
He represented Ouray County on the River District's board from 2006 to 2015, serving as Board President his final two years. He sits on the advisory board of the Family Farm Alliance and is an ex-officio member of the Water for Tribes Initiative Advisory Board. He holds a JD from the University of Colorado and a BA in history from Kenyon College.
Taylor Banks
WORKFORCE & SECURITY COMMUNITY
Principal, Cyber Summit Co.
Taylor Banks has worked in IT since 1992 and in information security since 1997, specializing in applied hacking and countermeasures. He founded ACE Hackware in 2011 and has delivered penetration testing and security training for corporations, the United Nations, the National Weather Service, several U.S. military branches and federal agencies.
Earlier he was a Senior Security Engineer at VeriSign and Chief Security Architect at InfoWeapons.
A longtime voice on privacy and anonymity, he co-founded the kaos.theory security research group, which created the Anonym.OS live CD, and led DC404, Atlanta's DEF CON group, from 2003 to 2013. He has spoken at or volunteered for DEF CON, Black Hat and Security BSides.
Kelly Moan
FIRESIDE · Former CISO, City of New York
Kelly Moan served as Chief Information Security Officer of the City of New York, the first woman to hold the role, leading NYC Cyber Command in defending the largest municipal network in the United States across more than 100 agencies serving over 8 million residents.
During the global CrowdStrike outage her team kept essential city services running, and in 2022 she launched the NYC Cyber Academy to train city employees in incident response.
Before that she was CISO of the NYPD, and earlier a Division Chief at the U.S. Department of Homeland Security leading security architecture and engineering, where she also served as FedRAMP Joint Authorization Board technical representative to the CIO.
She is a Fellow at George Mason University's National Security Institute and holds degrees from American University and Penn State.
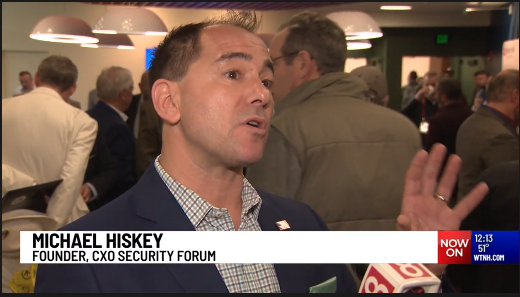
Michael Hiskey
[Moderator]
Founder, CxO Security Forum
Founder and Chief Strategy Officer of the CxO Security Forum, a community-led, practitioner-first series convening senior security executives. Serves as master of ceremonies for the summit and moderates the afternoon roundtable report-outs.
Michael brings 20+ years in enterprise B2B strategy across cybersecurity, fintech, data and AI, including CMO and CSO roles at Avanan, Semarchy, Socure, Kognitio, Trifacta, Data Connectors and Engagez, and nearly a decade at IBM, including time in Brazil.
He holds an Executive MBA from Columbia Business School and a BS from the University at Albany, and has guest-lectured at St. John's and Baruch.
An author, moderator and speaker, he has been published in Forbes, InformationWeek, WSJ.com and ITProPortal and has appeared on CNBC and C|Net.
About CxO Forum
CxO Security Forum began as a response to a common frustration among senior cybersecurity leaders: the way enterprise solutions are marketed, sold, and evaluated is fundamentally broken. What started as a call for change has grown into a trusted community that puts executive practitioners at the center of the conversation.
We bring together CISOs, CIOs, and senior decision-makers who are responsible for protecting their organizations, guiding strategic risk, and navigating the evolving role of AI in security. Every forum, gathering, and conversation is designed to foster education, mentoring, and authentic peer connection.
What makes us different is our focus on relationships. Our events are intentionally small, curated, and built for real dialogue. Sponsors are carefully selected, and there are no product pitches. Participants come for thoughtful, actionable conversations that support both professional development and practical decision-making.
At CxO Security Forum, the goal is simple. Give experienced leaders a space to learn from one another, to share insight, and to build meaningful connections that last beyond the event itself.
Location
Colorado Mesa University
1100 North Avenue
Grand Junction, CO 81501-3122
© 2025 CxO Security Forum. All rights reserved